
030611/dsh-verification-receipt
面向DeepSeek Harness的隐私最小化启发式逐轮验证摘要
Project Overview项目介绍
This is a native plugin built exclusively for core DeepSeek Harness, designed to collect lightweight execution summaries after each completed turn. It appends a privacy-minimal heuristic summary to a lightweight local JSONL file, recording only tool call counts and lexical verification signals, not semantic correctness of any code or tests. To install the pre-built published package, run the executable dsh plugin --profile <your-profile> add dsh-verification-receipt via the DSH CLI, and for local development, clone the repository, install dependencies with pnpm, then point the add command to your local checkout path.
The plugin runs passively in the background after each turn ends, so it does not add any new tools to the model, change existing session logs, or add extra token cost to your OpenAI API calls. It does not impact core turn latency, as it queues all disk I/O asynchronously after the turn completes. The default output file path is $DSH_HOME/verification-receipts/v1/receipts.jsonl, which resolves to ~/.dsh if DSH_HOME is not set. You can override the output path with an absolute path in your profile configuration to fit your specific storage or auditing needs.
Version 0.1.1 of this plugin is compatible with DSH versions 0.1.2-alpha.3, 0.1.2-alpha.4, and 0.1.2-alpha.5, and requires Node.js version ^22.19.0 || >=24.0.0 to run. It is released under the open source MIT license, and has several documented limitations to be aware of when using it. For example, it cannot backfill history from before the plugin was loaded, abrupt process termination can lose queued receipts, and it does not support signal detection for aliased or nested commands. You should always configure a trusted private path to avoid common cross-process write conflicts.
这是一款专为DeepSeek Harness开发的原生插件,在每次可持久化会话回合结束后,会将一份隐私最小化的启发式执行摘要追加存储到本地JSONL文件。它仅记录工具调用次数和词法验证相关的执行轨迹,不证明代码或测试的语义正确性,也不提供证据审计账本、哈希链或声明证据关联等功能。可通过DSH CLI命令添加到目标配置文件,本地开发可克隆仓库后指定路径安装。
开发者可使用该插件收集DSH执行过程中的工具调用统计和潜在验证信号,用于后续审计或分析AI工作流。默认输出路径为$DSH_HOME/verification-receipts/v1/receipts.jsonl,未设置DSH_HOME时会解析到~/.dsh目录下,也可在配置文件中自定义绝对路径输出。该插件被动运行,不会新增工具调用、不改变会话日志,也不增加token成本或核心回合延迟。
该插件采用MIT许可证开源,当前0.1.1版本明确支持DSH的三个alpha版本,要求Node.js版本为^22.19.0 || >=24.0.0,依赖Schemastery运行时。它存在多个已知限制,比如无法回溯填充插件未加载时的历史记录,进程崩溃可能丢失排队的收据,不支持别名或嵌套命令的信号匹配。使用时需注意配置可信私有路径,避免多进程写入冲突。
请帮我安装这个 DSH 插件。安装前先完成【兼容性检查 + 安全性检查】,检查通过再动手。

插件:dsh-verification-receipt(030611/dsh-verification-receipt)
仓库:https://github.com/030611/dsh-verification-receipt
本站详情页:https://www.yhbd.top/plugins/030611-dsh-verification-receipt/
本站登记:类型 plugin · 归类 原生 DSH 插件 · 许可证 MIT · ⭐ 4 · 最近提交 2026-09-03 · 主语言 TypeScript

按下面顺序执行,每步先把结论告诉我,再进入下一步:

【1 兼容性检查】
① 我这边:DSH 版本、Node 版本、操作系统、当前 profile(web / desktop)。
② 读它的 README、package.json、插件 manifest,列出它要求的 DSH 版本 / Node 版本 / 操作系统 / 外部依赖 / 需要另外先装的运行时。
③ 逐条比对,结论只写「满足 / 不满足 / 未知」三种;不满足的给出可行替代方案。
④ 检查是否和我已装的插件冲突:命令名重复、skill / tool 重名、端口占用、重复注册的 MCP server。

【2 安全性检查】
① 仓库可信度:和上面「本站登记」是否一致;star / fork 数、创建时间、最近提交,是否归档或长期停更。
② 安装脚本:逐行看 package.json 的 preinstall / install / postinstall,以及 install.sh、setup.ps1 之类脚本。出现 curl|bash、下载后直接执行、混淆代码、访问与插件功能无关的域名,立刻停下来告诉我,不要继续装。
③ 依赖:列出新增依赖,标出无人维护、或与知名包拼写近似的可疑包(typosquatting)。
④ 权限与副作用:它会读写哪些目录、访问哪些域名、需要哪些 DSH 权限(filesystem / network / shell / clipboard 等),以及怎么卸载和回滚。
⑤ 如果它要求 sudo / 管理员权限,或权限明显超出功能所需,先停下来问我。

【3 安装】
上面两步没有「不满足」和「高危项」时才执行;用官方推荐方式安装,不要自行提权。

【4 汇报】
用表格输出:检查项 / 结论 / 依据 / 是否需要我决策。拿不准的一律写「未知」并说明要我怎么确认——不要猜,也不要替我决定。
Send this message to DSH in your current session: it verifies compatibility and security first (answering met / not met / unknown item by item) and only installs once everything checks out — it will stop and ask you if it finds a high-risk item. The box scrolls; the copy is the full prompt. CLI install commands may not be accurate across systems, so DSH is the safer route.把上面这条消息直接发给当前会话里的 DSH:它会先核对兼容性与安全性(逐条给「满足 / 不满足 / 未知」),确认没问题再安装,有高危项会停下来问你。框内可滚动,复制到的是完整提示词;安装命令不一定准确,发给 DSH 更稳。
- Only 4 stars - very few users, little community feedback星标只有 4,几乎没人在用,遇到问题缺少社区反馈
DSH walks through these 9 checksDSH 会逐条核对这 9 项
Compatibility兼容性
- DSH, Node, OS and profile requirementsDSH 版本 / Node 版本 / 操作系统 / profile 是否满足要求
- External dependencies and runtimes (Electron / Python / Docker, ...)外部依赖与运行时(Electron / Python / Docker 等)是否齐备
- Conflicts with installed plugins: command names, skill / tool names, ports, duplicate MCP registration与已装插件是否冲突:命令名、skill / tool 重名、端口占用、重复 MCP 注册
Security安全性
- Repo matches the facts registered here; archived or abandoned?仓库是否与页面登记一致,是否归档或长期停更
- Safety of preinstall / install / postinstall and install.sh / setup.ps1preinstall / install / postinstall 与 install.sh、setup.ps1 是否安全
- curl|bash, download-then-execute, obfuscation, unrelated domains → stop immediatelycurl|bash、下载即执行、混淆代码、无关域名 → 立刻停止
- Typosquatting or unmaintained packages among the new dependencies新增依赖里有没有 typosquatting 或无人维护的包
- Requested permissions vs. what the feature actually needs申请了哪些权限、是否超出功能所需(filesystem / network / shell / clipboard)
- Any sudo / admin requirement, plus uninstall and rollback是否要求 sudo / 管理员权限,以及卸载与回滚方式
Anything uncertain must be marked unknown with a note on how to confirm it. This site's signal screen is a static snapshot, not a security audit.拿不准的必须标「未知」并说明要我怎么确认。本站的信号筛查是静态快照,不能替代安全审计。
Or use CLI install (for developers)或使用命令行安装(适合开发者)
CLI Install命令行安装
dsh plugin --profile web add dsh-verification-receipt把 030611/dsh-verification-receipt 加入你的 DSH 配置(web profile)即可启用。
READMEREADME
DSH Verification Receipt


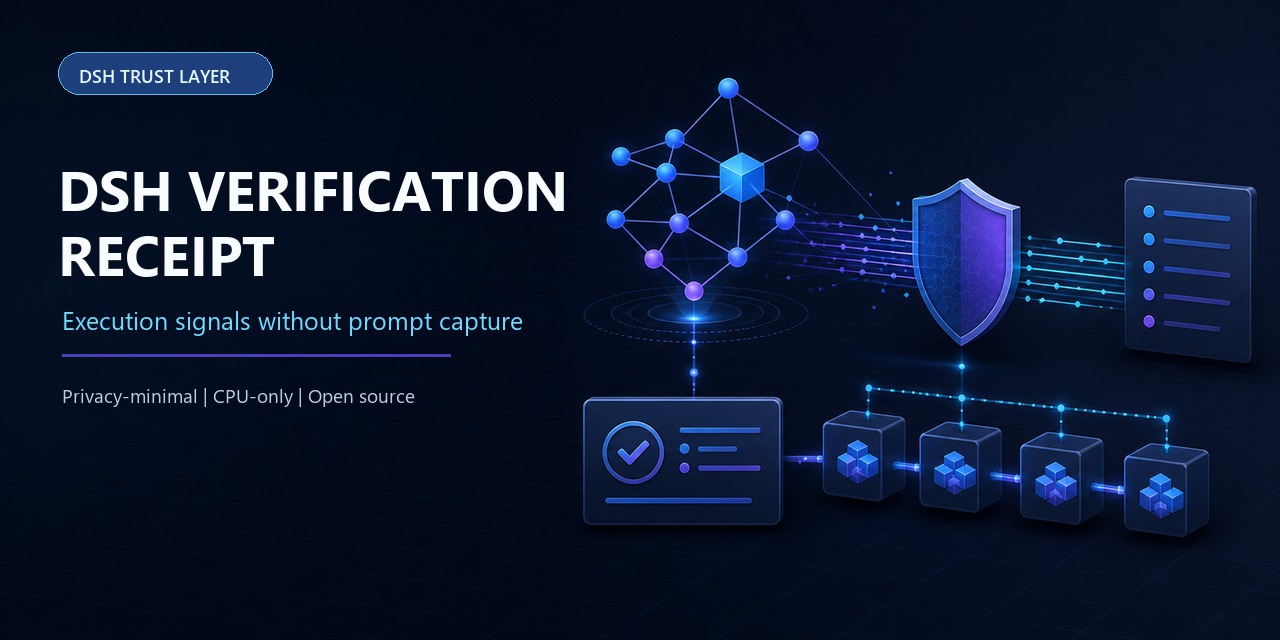
Ask a smaller, checkable question: what verification-shaped execution signals did DSH record this turn?
dsh plugin --profile web add dsh-verification-receipt
The receipt summarizes recorded tool counts and lexical verification-shaped signals. It does not prove that tests ran or that code is correct.
Community-maintained and not an official DeepSeek project. Related trust-layer plugins: Telemetry Redactor, Evidence Audit, and Context Provenance.
DSH Verification Receipt is a small, passive Profile Bundle for DeepSeek Harness. After each durable turn/end, it appends one privacy-minimal, heuristic execution summary to a local JSONL file.

It records execution traces, not semantic correctness. A receipt shows only that DSH logged tool calls and that a lexical heuristic found a possible verification signal. It never proves that a test ran. It cannot show that the right command executed, that assertions were sufficient, that output was truthful, or that the assistant's conclusion was correct.
This is intentionally not an evidence-audit ledger: rows stay independent and there is no hash chain, artifact capture, claim-evidence linkage, or protocol attestation.
Showing the opening section of the README — the full document lives in the repository以上为 README 开头摘要,完整文档在仓库内 · View the full README on GitHub →在 GitHub 查看完整 README →
Related相关推荐
- ranxianglei/billion-context 基本稳定可用 A context-compression plugin for small context windows (a 100K context is enough), token savings (5x fewer tokens…
-
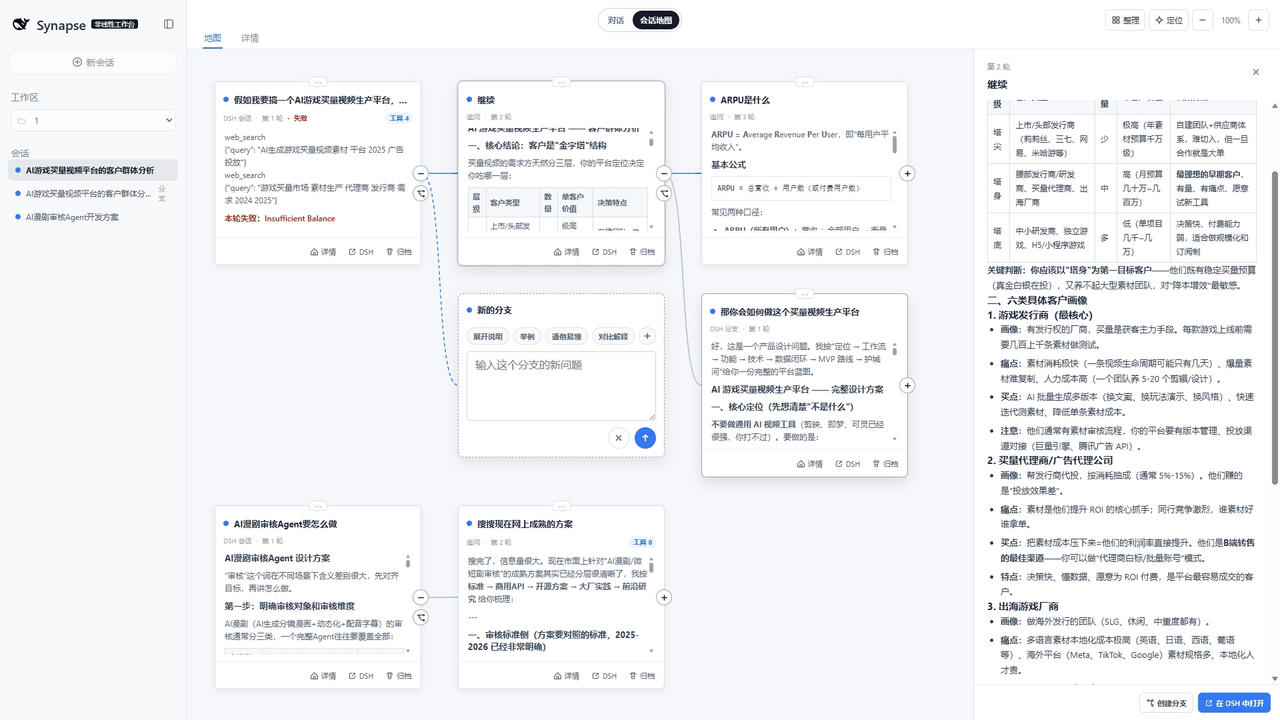 liangmianya/dsh-synapse
A visual, non-linear conversation workspace plugin for DeepSeek Harness ; A canvas-based session explorer and branching …
-
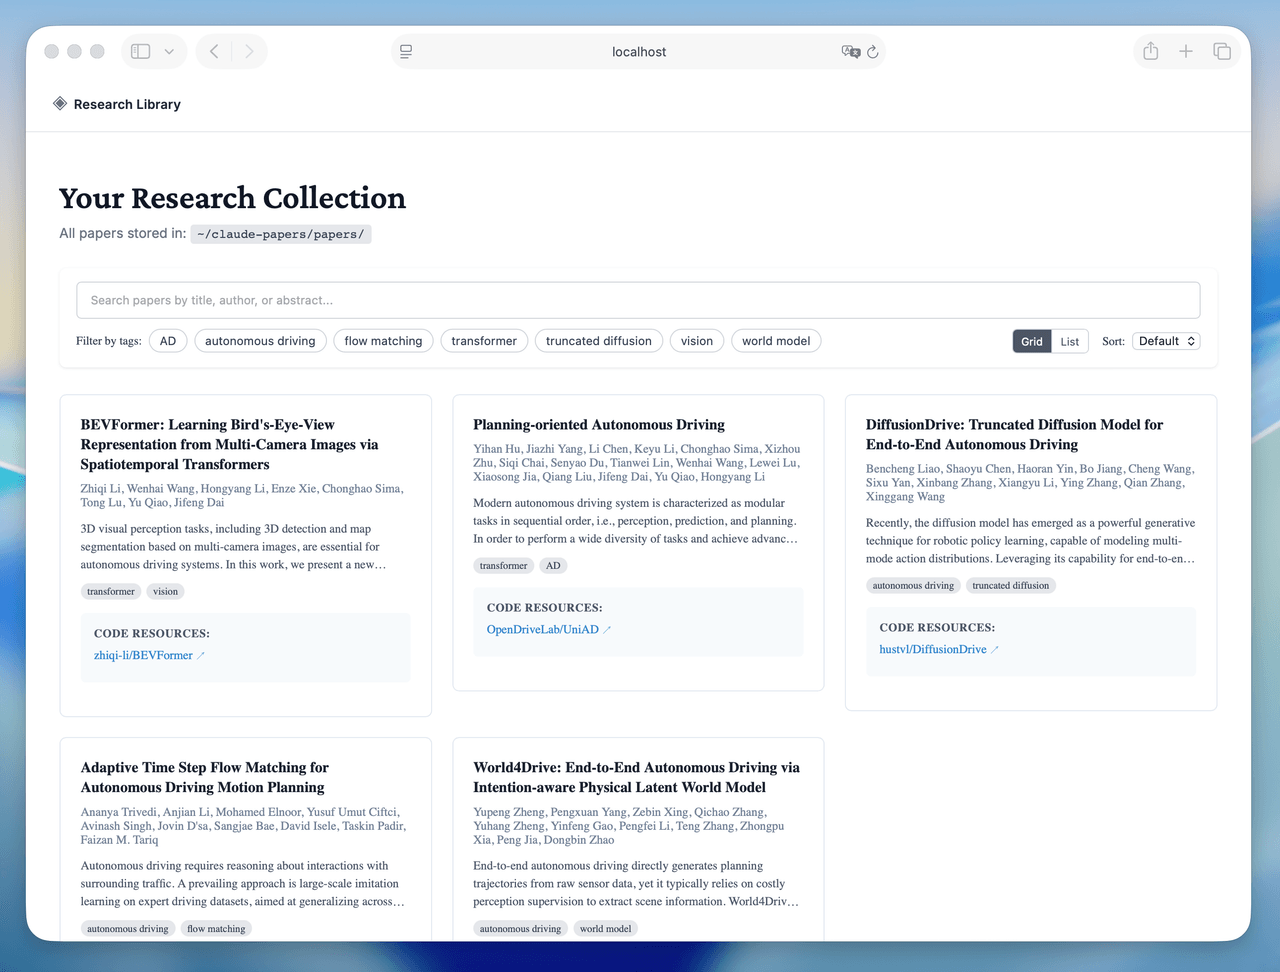 alaliqing/claude-paper
📖 Cross-agent research paper toolkit for Claude Code, Codex, OpenCode, and DeepSeek Harness—quick summaries, deep study…
-
 acryldev/acryl
ACRYL - Agent Context Relay Yielding Lifecycles. One persistent workspace, one canonical context, any coding agent.
-
 omdsh-dev/dsh-annotation
DSH Web 选中批注插件:选文字→批注→回车随消息发送;气泡隐藏批注块(零闪烁);回复按 Annotation N 逐条对照(可悬浮芯片)。官方 bundle,零核心改动
-
 Anionex/dsh-turn-rewind
deepseek harness对话和代码状态回退插件 | DSH — rewind conversation and workspace state, powered by a persistent Change Ledger
-
 Tyan66666/billion-context-dsh
Model-driven context management (Active Context Pruning / ACP) for the DeepSeek Harness — the model decides when and wha…
-
 qkycir-123/dsh-run2skill
Automatically turn successful DeepSeek Harness sessions into reusable, reviewable Agent Skills.