lpeixin/dsh-qualityforge
QualityForge is an enterprise-grade DeepSeek Harness QA plugin that automates systematic end-to-end testing and delivers P0–P3 severity-based, actionable reports and quality gates to help developers identify issues and prioritize fixes. QualityForge 是一个面向企业级项目的 DeepSeek Harness QA 插件,自动执行系统性端到端测试,并通过 P0–P3 严重度分级、可勾选的测试报告与质量门禁,帮助开发者快速识别问题并确定修复优先级。
Project Overview项目介绍
QualityForge is a DSH-native Cordis plugin that runs an enterprise-grade systematic audit over an already-completed project and produces a per-item checkable report with P0–P3 severity. It mounts inside DeepSeek Harness as a Cordis plugin that depends on the dsh.bundle.patch contract and ships a bundle-manifest, so any DSH version supporting Cordis loads it directly. The package itself is small, about 215 KB packed and around 726 KB unpacked, requires Node.js 20.11 or newer, and uses only Node built-ins with no native modules, so it runs unchanged on macOS, Linux and Windows. Twenty-seven unit tests ship in test/ and are executed with node --test, while npm run validate enforces the catalog contract and the preset mapping.
The workflow is a six-stage pipeline: reconnaissance, exhaustive checklist generation, running every discoverable preset, having the agent process items left over, emitting a checkable report, and finally negotiating fix scope before a re-test closes the loop. The catalog covers 45 domains, 290 methods and 1363 independently verifiable checks, including build & dependencies, static quality, unit and advanced testing, integration & contracts, API layer, UI & accessibility, E2E & acceptance, data, performance & capacity, security & compliance, reliability, observability & ops, engineering process, plus DSH-plugin-specific and open-source-readiness domains, and it ships at four depths of 331, 984, 1295 and 1363 items respectively. The project type is auto-detected from library, cli, service, web, desktop, mobile, plugin, data, ml or monorepo so inapplicable items are skipped with reasons rather than counted as passes, and the final report returns a single verdict of Blocked, Audit incomplete, Conditional or Ready.
Dependencies and first-run limits are deliberately tight: no external imports are allowed, named exports only without export default, the audited project is never modified, qf_exec keeps install off by default, qf_probe only reaches the loopback interface, and every write is restricted to .qualityforge/ inside the audited project. All intermediate artifacts stay under that folder so the report can be re-rendered, reviewed in a pull request and diffed between runs. The current report catalog, tool descriptions and the documents under docs/ are written in Simplified Chinese while an English locale is on the roadmap alongside SARIF and JUnit XML export, and the project is released under the MIT license by Peixin in 2026.
QualityForge 是一个面向 DeepSeek Harness(DSH)的原生插件,针对已完成的项目运行企业级系统化的审计检测。它在 DSH 中以 Cordis 插件的形式挂载,需 DSH 版本支持 Cordis 插件与 dsh.bundle.patch 契约,安装时从 npm 拉取约 215 KB 的 tarball,解压后约 726 KB。插件需要 Node.js ≥ 20.11,零外部依赖,仅使用 Node 内置模块,可跨 macOS、Linux 与 Windows 直接运行。
典型工作流覆盖六个阶段:侦察 → 穷尽式检查清单 → 执行可运行的预设 → 由 Agent 分析剩余项 → 输出可勾选报告 → 商定修复范围 → 重测关闭。报告内置 45 个领域、290 种方法、1363 个独立可验证检查项,按 smoke/standard/deep/exhaustive 四档深度展开。它通过探测项目类型(库、CLI、服务、Web、桌面、移动、插件、数据、ML、Monorepo)跳过不适用的检查,跳过项会附带理由而非计为通过。最终会给出 ⛔ Blocked / ⏳ Audit incomplete / ⚠️ Conditional / ✅ Ready 的发布裁决。
依赖与运行限制方面,插件禁止引入任何外部包,禁止默认导出,不修改被审计项目,qf_exec 默认关闭 install,qf_probe 仅访问回环地址,写入仅落在 .qualityforge/ 下。测试目录内置 27 项用例,可通过 node --test 运行,并以 npm run validate 校验目录契约。许可证为 MIT,2026 Peixin 现局对当前报告目录、检查项与文档主要为中文,未来规划英文输出与 SARIF / JUnit XML 导出。
请帮我安装这个 DSH 插件。安装前先完成【兼容性检查 + 安全性检查】,检查通过再动手。

插件:dsh-qualityforge(lpeixin/dsh-qualityforge)
仓库:https://github.com/lpeixin/dsh-qualityforge
本站详情页:https://www.yhbd.top/plugins/lpeixin-dsh-qualityforge/
本站登记:类型 client · 归类 原生 DSH 插件 · 许可证 MIT · ⭐ 4 · 最近提交 2026-10-01 · 主语言 JavaScript

按下面顺序执行,每步先把结论告诉我,再进入下一步:

【1 兼容性检查】
① 我这边:DSH 版本、Node 版本、操作系统、当前 profile(web / desktop)。
② 读它的 README、package.json、插件 manifest,列出它要求的 DSH 版本 / Node 版本 / 操作系统 / 外部依赖 / 需要另外先装的运行时。
③ 逐条比对,结论只写「满足 / 不满足 / 未知」三种;不满足的给出可行替代方案。
④ 检查是否和我已装的插件冲突:命令名重复、skill / tool 重名、端口占用、重复注册的 MCP server。

【2 安全性检查】
① 仓库可信度:和上面「本站登记」是否一致;star / fork 数、创建时间、最近提交,是否归档或长期停更。
② 安装脚本:逐行看 package.json 的 preinstall / install / postinstall,以及 install.sh、setup.ps1 之类脚本。出现 curl|bash、下载后直接执行、混淆代码、访问与插件功能无关的域名,立刻停下来告诉我,不要继续装。
③ 依赖:列出新增依赖,标出无人维护、或与知名包拼写近似的可疑包(typosquatting)。
④ 权限与副作用:它会读写哪些目录、访问哪些域名、需要哪些 DSH 权限(filesystem / network / shell / clipboard 等),以及怎么卸载和回滚。
⑤ 如果它要求 sudo / 管理员权限,或权限明显超出功能所需,先停下来问我。

【3 安装】
上面两步没有「不满足」和「高危项」时才执行;用官方推荐方式安装,不要自行提权。

【4 汇报】
用表格输出:检查项 / 结论 / 依据 / 是否需要我决策。拿不准的一律写「未知」并说明要我怎么确认——不要猜,也不要替我决定。
Send this message to DSH in your current session: it verifies compatibility and security first (answering met / not met / unknown item by item) and only installs once everything checks out — it will stop and ask you if it finds a high-risk item. The box scrolls; the copy is the full prompt. CLI install commands may not be accurate across systems, so DSH is the safer route.把上面这条消息直接发给当前会话里的 DSH:它会先核对兼容性与安全性(逐条给「满足 / 不满足 / 未知」),确认没问题再安装,有高危项会停下来问你。框内可滚动,复制到的是完整提示词;安装命令不一定准确,发给 DSH 更稳。
- Only 4 stars - very few users, little community feedback星标只有 4,几乎没人在用,遇到问题缺少社区反馈
- Desktop client: installation downloads an executable - verify the publisher and checksums桌面客户端:安装会下载可执行文件,请核对发布者与校验和
DSH walks through these 9 checksDSH 会逐条核对这 9 项
Compatibility兼容性
- DSH, Node, OS and profile requirementsDSH 版本 / Node 版本 / 操作系统 / profile 是否满足要求
- External dependencies and runtimes (Electron / Python / Docker, ...)外部依赖与运行时(Electron / Python / Docker 等)是否齐备
- Conflicts with installed plugins: command names, skill / tool names, ports, duplicate MCP registration与已装插件是否冲突:命令名、skill / tool 重名、端口占用、重复 MCP 注册
Security安全性
- Repo matches the facts registered here; archived or abandoned?仓库是否与页面登记一致,是否归档或长期停更
- Safety of preinstall / install / postinstall and install.sh / setup.ps1preinstall / install / postinstall 与 install.sh、setup.ps1 是否安全
- curl|bash, download-then-execute, obfuscation, unrelated domains → stop immediatelycurl|bash、下载即执行、混淆代码、无关域名 → 立刻停止
- Typosquatting or unmaintained packages among the new dependencies新增依赖里有没有 typosquatting 或无人维护的包
- Requested permissions vs. what the feature actually needs申请了哪些权限、是否超出功能所需(filesystem / network / shell / clipboard)
- Any sudo / admin requirement, plus uninstall and rollback是否要求 sudo / 管理员权限,以及卸载与回滚方式
Anything uncertain must be marked unknown with a note on how to confirm it. This site's signal screen is a static snapshot, not a security audit.拿不准的必须标「未知」并说明要我怎么确认。本站的信号筛查是静态快照,不能替代安全审计。
Or use CLI install (for developers)或使用命令行安装(适合开发者)
CLI Install命令行安装
dsh plugin --profile web add dsh-qualityforge把 lpeixin/dsh-qualityforge 加入你的 DSH 配置(web profile)即可启用。
READMEREADME
English | 简体中文


QualityForge is a DeepSeek Harness plugin that runs a systematic, enterprise-grade test pass over a finished project and produces a per-item checkable report with P0–P3 severity — a quality verdict, and the artifact developers and the Harness use to agree on what to fix and in which order.
| Question | What QualityForge gives you |
|---|---|
| Can this ship? | A verdict: ⛔ Blocked / ⏳ Audit incomplete / ⚠️ Conditional / ✅ Ready |
| What exactly is wrong? | 45 test domains, 290 methods, 1363 independently verifiable checks — each with a conclusion, evidence and a fix suggestion |
| What first? | Fix waves (Wave 1 clears blockers → Wave 2 criticals → …) plus a handoff sheet you can paste back into the Harness |
| What after fixing? | Tick items in the report → qf_update sync=true reads them back → qf_exec re-tests → only then does an item become verified |
The report, catalog, tool descriptions and the documents under
docs/are written in Chinese today; an English report locale is on the roadmap. Identifiers (QF-001), statuses and the JSON artifacts are language-neutral.
Why this exists
"The code is written" and "this is shippable" are two different claims, and the second one needs evidence. What usually gets in the way:
- Not knowing what to test — enterprise test practice lives in specs, checklists and people's heads; improvising leaves blind spots, and the blind spots are exactly where releases break.
- No trace of what was checked — commands get run, conclusions evaporate, and two weeks later nobody can say what was actually verified.
- Verdicts that cannot be negotiated — reports read like sentences; there is no structured way to say "this must be fixed, that risk we accept".
- Unclear fix scope — with dozens of findings, which come first, which are in this round, and how do we know a fix is really done?
Showing the opening section of the README — the full document lives in the repository以上为 README 开头摘要,完整文档在仓库内 · View the full README on GitHub →在 GitHub 查看完整 README →
Related相关推荐
-
 nexu-io/open-design
🎨 Best DeepSeek Harness Design Plugin. The open-source Claude Design alternative. 🖥️ Local-first desktop app. 🖼️ Your…
-
 EthanYoQ/Invoice-Downloader
电子发票整理与报销准备工具:从邮箱批量收集 PDF/OFD/XML 发票,OCR 识别、分类归档并生成 Excel 汇总;提供 Windows/macOS 桌面版与 DSH 插件。
-
 sunchaokun/PPT-Design-Skill
Precision PPT design skill for OpenCode/Claude Code/Codex, with 40,000+ styles, pixel-perfect Build Mode control, AI ima…
-
 THU-MAIC/dsh-openmaic
OpenMAIC for DeepSeek Harness: classrooms, slides, interactive widgets, and Socratic teaching
-
 HuanLinOTO/dsh-plugin-mineru
向模型暴露 MinerU 文档解析工具,将 PDF/图片/DOCX/PPTX/XLSX 转为结构化 Markdown/JSON | Exposes MinerU document-parsing tools to the model, co…
-
 jing-hy/picturereader
DSH plugin: pixel-to-text image reading for text-only models. image_scan/image_ocr/image_sample tools + image-reading sk…
-
 hellodigua/dsh-share
DSH 对话分享插件,分享单轮或多轮对话,可导出为图片或 Markdown。Share DSH Q&As or selected conversation groups as PNG or Markdown.
-
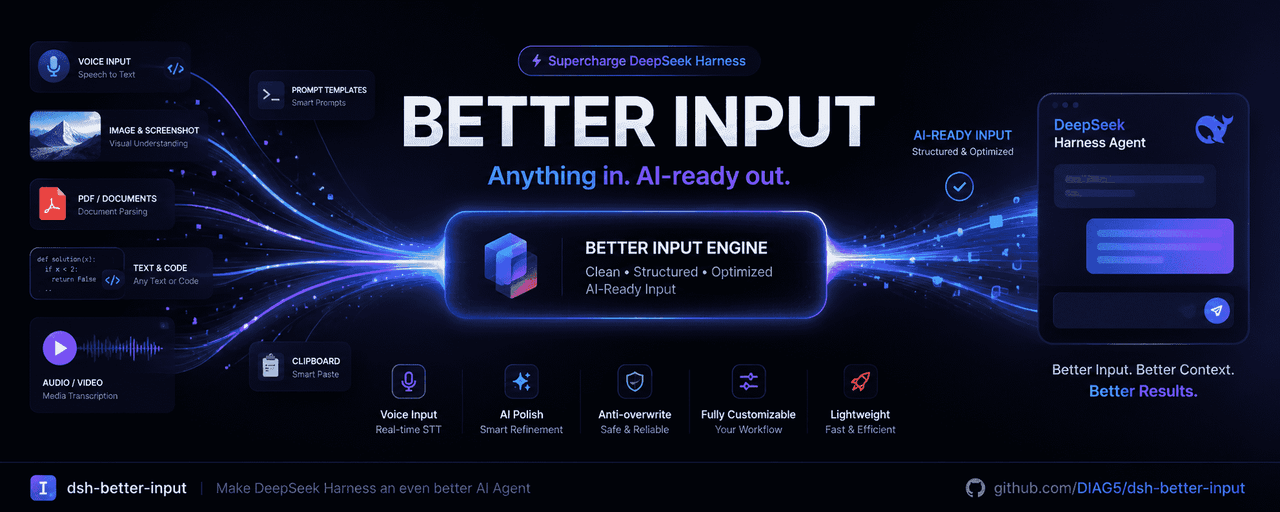 DIAG5/dsh-better-input
BetterInput是一套输入增强套件:语音识别、提示词优化、输入更多文件类型,各类文件转Md,交互体验优化等——把每一种喂给智能体的输入都变得更好。BetterInput is an input-enhancement suite — …