webkubor/dsh-env-inspector
DSH 环境自检:让读者看到自己电脑装了什么 —— 系统/CLI/DSH 插件/秘钥是否存在
Project Overview项目介绍
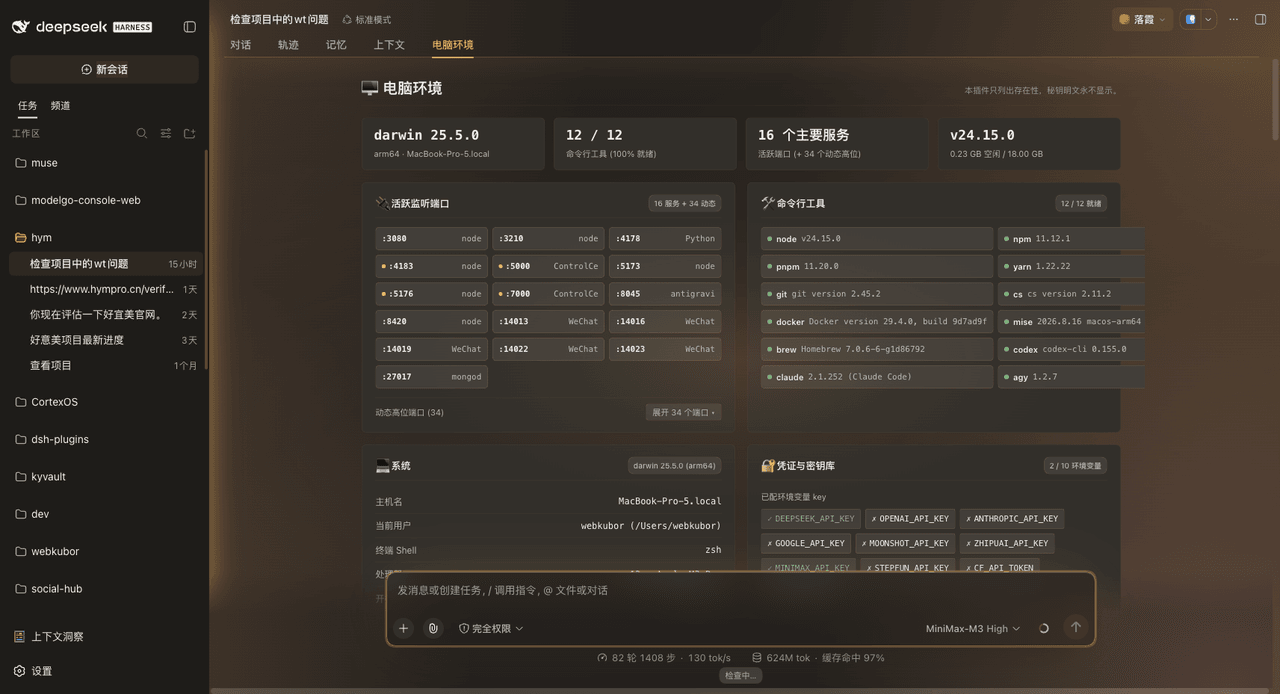
dsh-env-inspector is a native DeepSeek Harness (DSH) environment-inspection and port-operations plugin, distributed as the npm package @dsh-plugins/dsh-env-inspector and requiring DSH ≥0.1.5-rc.2. Built on Node.js native APIs and pure React, it carries zero runtime dependencies and ships as a DSH bundle that integrates through either the dsh plugin add @dsh-plugins/dsh-env-inspector command or a manual package.json entry that lists the package under dependencies and under dsh.profile.bundles, followed by ~/.dsh/restart.sh. Once restarted, the plugin exposes a top-nav "🖥️ 电脑环境" tab whose modern card dashboard reports four core Hero KPIs, full listening-port telemetry, CLI tool-chain status, and credential presence.
The plugin's central capability is live port discovery via lsof, with PATH augmentation so macOS daemons are captured, plus a one-click safe Kill action that revalidates PID-to-port mapping server-side, prefers SIGTERM, escalates to SIGKILL only when needed, and then auto-refreshes the dashboard so KPIs decrement immediately. Hard-coded protections permanently lock the DSH core port :3080, the host's own process.pid, and privileged system PIDs against accidental termination, while high ephemeral ports (49152+) are folded into a collapsible drawer to keep the view uncluttered, and ports bound to 0.0.0.0 are flagged with an amber warning dot to highlight potential LAN exposure. The same dashboard lists twelve common developer CLIs — node, npm, pnpm, yarn, git, cs, docker, mise, brew, codex, gemini, claude, opencode, agy — plus python3, go, and rustc when present, and surfaces loaded DSH profile bundles with their effective versions.
The intended audience is DSH developers who juggle multiple Node and Python services, hit recurring EADDRINUSE errors from orphaned listeners, and need a single dashboard to audit their local environment before collaboration or debugging sessions. Security commitments include never reading, outputting, or transmitting plaintext keys, no outbound traffic by default (the public egress IP check fires only on explicit user click), and a strict Sec-Fetch-Site: same-origin check on every API. The MIT-licensed roadmap promises process working-directory reverse lookup, a baseline-port diff mode highlighting ghost listeners, and a future package rename once maintainer accounts converge; the plugin is part of the webkubor DSH suite alongside dsh-bloom-theme, dsh-llm-hub, and dsh-user-mirror.
dsh-env-inspector 是一款面向 DeepSeek Harness(DSH)的原生环境自检与端口运维插件,基于 Node.js 原生 API 与纯 React 构建,零运行时依赖,通过 npm 包 @dsh-plugins/dsh-env-inspector 分发,要求 DSH 版本 ≥0.1.5-rc.2。它以现代卡片仪表盘的形式展示电脑环境,核心能力包括实时探测所有监听端口并支持鼠标一键安全释放占用进程、智能折叠高位动态端口、嗅探 12 款常见 CLI 工具链版本,以及高亮展示已配置生效的模型能力。安装方式为运行 dsh plugin add @dsh-plugins/dsh-env-inspector,或在 DSH profile 的 package.json 中将包加入 dependencies 与 dsh.profile.bundles,随后执行 ~/.dsh/restart.sh 重启,点击顶部导航栏的「🖥️ 电脑环境」Tab 即可启用。
典型使用场景是开发者在本地运行 DSH 与多种 Node/Python 服务后遭遇端口冲突报错,或需要快速核对系统工具链与凭据配置是否就绪。该插件通过 lsof 探针补全 macOS 守护进程最小 PATH 路径,区分核心服务端口与动态端口,并对全网监听端口打上黄色警告圆点。端口释放前会再次校验目标 PID 与端口一致性,优先发送 SIGTERM 平滑清理,未退出再升级为 SIGKILL,DSH 核心端口 :3080 与宿主自身 PID 永久锁定,严禁误杀。它适合频繁调试多服务、关注环境整洁与安全出向的 DSH 用户。
插件采用 MIT 协议开源,不输出、不读取、不传递任何密钥明文;默认不联网,公网出口 IP 检测仅在用户主动点击时触发一次;所有接口强制校验 Sec-Fetch-Site: same-origin,杜绝跨站探测。Roadmap 计划加入进程工作目录反查、基准端口对比模式以及账号收敛后的官方包名迁移。它隶属于 webkubor 的 DSH 精选扩展家族,同家族另有 dsh-bloom-theme、dsh-llm-hub、dsh-user-mirror 等主题与路由插件。
请帮我安装这个 DSH 插件。安装前先完成【兼容性检查 + 安全性检查】,检查通过再动手。

插件:dsh-env-inspector(webkubor/dsh-env-inspector)
仓库:https://github.com/webkubor/dsh-env-inspector
本站详情页:https://www.yhbd.top/plugins/webkubor-dsh-env-inspector/
本站登记:类型 plugin · 归类 原生 DSH 插件 · 许可证 MIT · ⭐ 15 · 最近提交 2026-10-02 · 主语言 JavaScript

按下面顺序执行,每步先把结论告诉我,再进入下一步:

【1 兼容性检查】
① 我这边:DSH 版本、Node 版本、操作系统、当前 profile(web / desktop)。
② 读它的 README、package.json、插件 manifest,列出它要求的 DSH 版本 / Node 版本 / 操作系统 / 外部依赖 / 需要另外先装的运行时。
③ 逐条比对,结论只写「满足 / 不满足 / 未知」三种;不满足的给出可行替代方案。
④ 检查是否和我已装的插件冲突:命令名重复、skill / tool 重名、端口占用、重复注册的 MCP server。

【2 安全性检查】
① 仓库可信度:和上面「本站登记」是否一致;star / fork 数、创建时间、最近提交,是否归档或长期停更。
② 安装脚本:逐行看 package.json 的 preinstall / install / postinstall,以及 install.sh、setup.ps1 之类脚本。出现 curl|bash、下载后直接执行、混淆代码、访问与插件功能无关的域名,立刻停下来告诉我,不要继续装。
③ 依赖:列出新增依赖,标出无人维护、或与知名包拼写近似的可疑包(typosquatting)。
④ 权限与副作用:它会读写哪些目录、访问哪些域名、需要哪些 DSH 权限(filesystem / network / shell / clipboard 等),以及怎么卸载和回滚。
⑤ 如果它要求 sudo / 管理员权限,或权限明显超出功能所需,先停下来问我。

【3 安装】
上面两步没有「不满足」和「高危项」时才执行;用官方推荐方式安装,不要自行提权。

【4 汇报】
用表格输出:检查项 / 结论 / 依据 / 是否需要我决策。拿不准的一律写「未知」并说明要我怎么确认——不要猜,也不要替我决定。
Send this message to DSH in your current session: it verifies compatibility and security first (answering met / not met / unknown item by item) and only installs once everything checks out — it will stop and ask you if it finds a high-risk item. The box scrolls; the copy is the full prompt. CLI install commands may not be accurate across systems, so DSH is the safer route.把上面这条消息直接发给当前会话里的 DSH:它会先核对兼容性与安全性(逐条给「满足 / 不满足 / 未知」),确认没问题再安装,有高危项会停下来问你。框内可滚动,复制到的是完整提示词;安装命令不一定准确,发给 DSH 更稳。
- 15 stars - an early-stage project星标 15,属于早期项目
DSH walks through these 9 checksDSH 会逐条核对这 9 项
Compatibility兼容性
- DSH, Node, OS and profile requirementsDSH 版本 / Node 版本 / 操作系统 / profile 是否满足要求
- External dependencies and runtimes (Electron / Python / Docker, ...)外部依赖与运行时(Electron / Python / Docker 等)是否齐备
- Conflicts with installed plugins: command names, skill / tool names, ports, duplicate MCP registration与已装插件是否冲突:命令名、skill / tool 重名、端口占用、重复 MCP 注册
Security安全性
- Repo matches the facts registered here; archived or abandoned?仓库是否与页面登记一致,是否归档或长期停更
- Safety of preinstall / install / postinstall and install.sh / setup.ps1preinstall / install / postinstall 与 install.sh、setup.ps1 是否安全
- curl|bash, download-then-execute, obfuscation, unrelated domains → stop immediatelycurl|bash、下载即执行、混淆代码、无关域名 → 立刻停止
- Typosquatting or unmaintained packages among the new dependencies新增依赖里有没有 typosquatting 或无人维护的包
- Requested permissions vs. what the feature actually needs申请了哪些权限、是否超出功能所需(filesystem / network / shell / clipboard)
- Any sudo / admin requirement, plus uninstall and rollback是否要求 sudo / 管理员权限,以及卸载与回滚方式
Anything uncertain must be marked unknown with a note on how to confirm it. This site's signal screen is a static snapshot, not a security audit.拿不准的必须标「未知」并说明要我怎么确认。本站的信号筛查是静态快照,不能替代安全审计。
Or use CLI install (for developers)或使用命令行安装(适合开发者)
CLI Install命令行安装
npx @deepseek-ai/dsh plugin --profile web add @dsh-plugins/dsh-env-inspector把 webkubor/dsh-env-inspector 加入你的 DSH 配置(web profile)即可启用。
READMEREADME
🖥️ dsh-env-inspector
看清你的电脑装了什么,一键释放残留占用的开发端口。
DeepSeek Harness (DSH) 环境自检与端口运维插件 —— 现代卡片仪表盘,零运行时依赖;网络出口检测仅在用户点击时发生,绝不展示秘钥明文。



电脑环境 Dashboard —— 4 项核心 Hero KPI 指标行 + 现代双列网格卡片,系统状态、工具链与端口一目了然。
🎯 解决什么痛点
| 场景 | 以前的困扰 | dsh-env-inspector 的解法 |
|---|---|---|
| 端口常遭占用报错 | 关了终端后残留的 Node/Python 进程仍霸占端口,下次启动频繁 EADDRINUSE |
实时探测所有监听端口,鼠标一键点击「×」安全释放(Kill 进程),页面即时自动刷新 |
| 全网监听未察觉 | 服务不经意监听在 0.0.0.0,暴露在局域网存在安全隐患 |
醒目黄色警告圆点标注全网监听端口,提醒开发者关注访问控制 |
| 繁杂端口视觉干扰 | 系统高位动态端口(49152+)动辄几十个,严重干扰排查 | 智能抽屉机制:常用开发端口一目了然,高位动态端口平滑折叠,支持一键展开/收起 |
| 排查环境低效繁琐 | 协同或调试时需频繁在终端反复敲 node -v、git --version、lsof 截图 |
顶部 Tab 独立大看板:操作系统、12 款常用 CLI 就绪状态、大模型 Key 存在性全局掌控 |
✨ 核心特性
Showing the opening section of the README — the full document lives in the repository以上为 README 开头摘要,完整文档在仓库内 · View the full README on GitHub →在 GitHub 查看完整 README →
Related相关推荐
-
 esengine/DeepSeek-Reasonix
A reliable coding agent for complex software engineering tasks.
-
 strukto-ai/mirage
The World's First Virtual Terminal for AI Agents
-
 chuspeeism/dashi-taskboard
现代化可灵活嵌入的任务面板,支持 Codex、DeepSeek Harness
-
 Aisland-SJL/dsh-worktable
🖥️ Agent-project workbench for DeepSeek Harness — sidebar app drawer + dockable split workspace + a live control room w…
-
 ccch1mneyyy/working-activity
Lively Working-line extension for pi CLI and DSH
-
 zhoushoujianwork/easyeda-agent
嘉立创EDA专业版(EasyEDA Pro)自动化:给 AI harness 装上画板的「手」—— 一套 typed 原理图/PCB 动作,CLI / Agent Skill / stdio MCP 三形态融合接入。承接嘉立创「不以卖板赚钱…
-
 pulseaiclub/phi
a coding agent, rpc plugin, sub-agents, hashline edits, and mcp
-
 Ikalus1988/MisakaNet
📚 A zero-dependency, git-backed micro-lesson library for AI Agents to asynchronously share and search verified debuggin…