clarknu/dsh-gateway
面向DeepSeek Harness Web界面的自包含HTTPS远程访问网关——作为dsh插件的Caddy层。
Project Overview项目介绍
clarknu/dsh-gateway is a plugin built exclusively for DeepSeek Harness (DSH), that adds encrypted HTTPS access and password authentication to DSH’s built-in web interface. It installs directly via DSH’s built-in plugin manager with the single command dsh plugin --profile web add dsh-gateway, and requires no external programs or dependencies to run after installation. After installation, you just need to restart your DSH web instance to activate the gateway, which supports remote access from any device on your local area network or over the public internet with port forwarding configured.
By default, after first installation, the gateway only listens on localhost 127.0.0.1 port 3443, and has no pre-configured user accounts, so it defaults to blocking all external access as a fail-closed security measure. To enable external access, you need to configure the listening address, user accounts, and other settings either through the dedicated Remote Gateway settings card in DSH’s web settings page or by editing the YAML configuration file at $DSH_HOME/settings.yaml. All configuration changes take effect immediately without requiring a restart of DSH or the gateway itself.
The plugin follows a security-first baseline, and will refuse to start if it detects default example credentials when listening on a non-localhost interface. It also recommends binding the core DSH web service only to the loopback address to ensure all remote access goes through the gateway’s authentication layer. An optional Windows tray utility is included to manage DSH instances without a visible command line window, and the entire project is released under the open source MIT license.
dsh-gateway 是专为 DeepSeek Harness Web 界面设计的原生插件,用于给 DSH 添加 HTTPS 加密和账号登录保护,实现 DSH Web 界面的远程访问。用户可通过 DSH 命令行直接安装:dsh plugin --profile web add dsh-gateway,无需额外依赖外部程序,安装后重启 DSH Web 应用即可使用。它支持从局域网或互联网访问,可自动为 IP 直连生成自签名证书,也支持用户配置自有域名证书,并自带登录限流保护。
安装完成后默认仅监听本机 127.0.0.1:3443,且无预设账号,处于默认拒接访问的安全状态。用户需要在 DSH 设置页的 Remote Gateway 卡片或直接编辑 $DSH_HOME/settings.yaml 配置监听地址、登录账号等参数,配置后热生效无需重启。支持一键使所有已登录会话失效,也支持多站点配置,只响应白名单内的域名或 IP 请求。
该插件遵循安全优先设计,默认不允许使用示例凭据在非本机地址启动,要求 DSH 本体仅绑定回环地址保证所有远程访问经过认证。还附带可选的 Windows 托盘工具,可隐藏命令行窗口,方便管理 DSH 实例。项目采用 MIT 许可证开源,核心逻辑独立可测试,用户可自行修改或二次开发。
请帮我安装这个 DSH 插件。安装前先完成【兼容性检查 + 安全性检查】,检查通过再动手。

插件:dsh-gateway(clarknu/dsh-gateway)
仓库:https://github.com/clarknu/dsh-gateway
本站详情页:https://www.yhbd.top/plugins/clarknu-dsh-gateway/
本站登记:类型 plugin · 归类 原生 DSH 插件 · 许可证 MIT · ⭐ 7 · 最近提交 2026-09-14 · 主语言 JavaScript

按下面顺序执行,每步先把结论告诉我,再进入下一步:

【1 兼容性检查】
① 我这边:DSH 版本、Node 版本、操作系统、当前 profile(web / desktop)。
② 读它的 README、package.json、插件 manifest,列出它要求的 DSH 版本 / Node 版本 / 操作系统 / 外部依赖 / 需要另外先装的运行时。
③ 逐条比对,结论只写「满足 / 不满足 / 未知」三种;不满足的给出可行替代方案。
④ 检查是否和我已装的插件冲突:命令名重复、skill / tool 重名、端口占用、重复注册的 MCP server。

【2 安全性检查】
① 仓库可信度:和上面「本站登记」是否一致;star / fork 数、创建时间、最近提交,是否归档或长期停更。
② 安装脚本:逐行看 package.json 的 preinstall / install / postinstall,以及 install.sh、setup.ps1 之类脚本。出现 curl|bash、下载后直接执行、混淆代码、访问与插件功能无关的域名,立刻停下来告诉我,不要继续装。
③ 依赖:列出新增依赖,标出无人维护、或与知名包拼写近似的可疑包(typosquatting)。
④ 权限与副作用:它会读写哪些目录、访问哪些域名、需要哪些 DSH 权限(filesystem / network / shell / clipboard 等),以及怎么卸载和回滚。
⑤ 如果它要求 sudo / 管理员权限,或权限明显超出功能所需,先停下来问我。

【3 安装】
上面两步没有「不满足」和「高危项」时才执行;用官方推荐方式安装,不要自行提权。

【4 汇报】
用表格输出:检查项 / 结论 / 依据 / 是否需要我决策。拿不准的一律写「未知」并说明要我怎么确认——不要猜,也不要替我决定。
Send this message to DSH in your current session: it verifies compatibility and security first (answering met / not met / unknown item by item) and only installs once everything checks out — it will stop and ask you if it finds a high-risk item. The box scrolls; the copy is the full prompt. CLI install commands may not be accurate across systems, so DSH is the safer route.把上面这条消息直接发给当前会话里的 DSH:它会先核对兼容性与安全性(逐条给「满足 / 不满足 / 未知」),确认没问题再安装,有高危项会停下来问你。框内可滚动,复制到的是完整提示词;安装命令不一定准确,发给 DSH 更稳。
- Only 7 stars - very few users, little community feedback星标只有 7,几乎没人在用,遇到问题缺少社区反馈
DSH walks through these 9 checksDSH 会逐条核对这 9 项
Compatibility兼容性
- DSH, Node, OS and profile requirementsDSH 版本 / Node 版本 / 操作系统 / profile 是否满足要求
- External dependencies and runtimes (Electron / Python / Docker, ...)外部依赖与运行时(Electron / Python / Docker 等)是否齐备
- Conflicts with installed plugins: command names, skill / tool names, ports, duplicate MCP registration与已装插件是否冲突:命令名、skill / tool 重名、端口占用、重复 MCP 注册
Security安全性
- Repo matches the facts registered here; archived or abandoned?仓库是否与页面登记一致,是否归档或长期停更
- Safety of preinstall / install / postinstall and install.sh / setup.ps1preinstall / install / postinstall 与 install.sh、setup.ps1 是否安全
- curl|bash, download-then-execute, obfuscation, unrelated domains → stop immediatelycurl|bash、下载即执行、混淆代码、无关域名 → 立刻停止
- Typosquatting or unmaintained packages among the new dependencies新增依赖里有没有 typosquatting 或无人维护的包
- Requested permissions vs. what the feature actually needs申请了哪些权限、是否超出功能所需(filesystem / network / shell / clipboard)
- Any sudo / admin requirement, plus uninstall and rollback是否要求 sudo / 管理员权限,以及卸载与回滚方式
Anything uncertain must be marked unknown with a note on how to confirm it. This site's signal screen is a static snapshot, not a security audit.拿不准的必须标「未知」并说明要我怎么确认。本站的信号筛查是静态快照,不能替代安全审计。
Or use CLI install (for developers)或使用命令行安装(适合开发者)
CLI Install命令行安装
dsh plugin --profile web add dsh-gateway把 clarknu/dsh-gateway 加入你的 DSH 配置(web profile)即可启用。
READMEREADME
dsh-gateway
为 DeepSeek Harness 的 Web 界面加一层「HTTPS 加密 + 账号登录」的远程访问网关:作为 dsh 插件安装,无需任何外部程序,装上即用。
A self-contained HTTPS + login gateway for the DeepSeek Harness web surface. Install it as a dsh plugin — no external programs needed.
它能做什么
- 远程访问 DSH Web 界面:在局域网内的另一台电脑或手机上,打开
https://本机IP:端口就能访问;配置好端口映射后,从互联网也能访问 - HTTPS 加密:全程加密传输;有域名可用自己的证书,没有域名(IP 直连)会自动生成证书
- 登录保护:访问前必须先登录;账号、密码、会话有效期都可配置,登录失败自动限速;密码不以明文存储
- 会话可一键全部失效:在设置页点一下,所有已登录的设备立即退出,下次访问需重新输入用户名和密码(不再担心旧登录残留)
- 多站点:一个网关可同时服务多个域名或 IP
- 完整体验:远程访问与本地一致,实时消息等长连接功能正常工作
- 配置热生效:改配置立即生效,无需重启
安装
dsh plugin --profile web add dsh-gateway
重启 web 应用后,网关默认只在本机 127.0.0.1:3443 上监听、且没有任何账号——谁都登录不进去(fail-closed,安全优先)。要让别人能访问,按下面的「快速开始」配置账号与监听地址。
快速开始
以"局域网内另一台机器访问"为例:
配置登录账号与监听地址(设置页的 Remote Gateway 卡片,或直接编辑
$DSH_HOME/settings.yaml):gateway: listenHost: '0.0.0.0' # 监听所有网卡,允许局域网访问 users: admin: 'scrypt$...' # 用 node scripts/hash-password.mjs '你的密码' 生成记住网关端口(默认
3443)。在另一台设备浏览器打开
https://本机IP:3443,首次访问需信任自签证书,然后登录即可使用。
从互联网访问:在路由器上做端口映射,把外部端口转发到本机 gateway.port,用公网 IP(或域名)访问;使用域名时建议配置自己的证书。
注意:示例中的
admin / change-me只是演示用。只要该凭据仍在生效,网关就拒绝在非本机地址上启动。
配置
所有配置走 $DSH_HOME/settings.yaml 的 gateway: 段,也可以在 DSH 设置页的 Remote Gateway 卡片里直接修改(两者完全等价:同样校验、持久化、热生效)。
gateway:
  enabled: true            # false = 完全停用
  listenHost: '127.0.0.1'  # 监听地址:127.0.0.1 = 仅本机;0.0.0.0 = 所有网卡
  port: 3443               # 对外端口
  upstream: ''             # 留空 = 自动跟随 DSH web 服务端口
  sessionDays: 30          # 会话有效期(天)
  loginFailLimit: 5        # 每 IP 连续登录失败次数上限
  lockoutSeconds: 60       # 超过上限后的锁定秒数
  users:                   # 登录账号(值为密码哈希,推荐)
    admin: 'scrypt$...'
  sites:                   # 站点列表:只响应这里列出的域名/IP
    - hosts: ['你的域名', '你的IP']
      cert: '证书路径'      # 留空 = 自动生成
      key: '密钥路径'
- 默认
users为空、listenHost为127.0.0.1:不配置 = 无人可登录、仅本机可达 sites[].hosts支持*.example.com通配;网关只响应白名单内的域名/IP- 密码生成哈希:
node scripts/hash-password.mjs '你的密码';设置页保存的密码会自动哈希,无需手动生成
设置页配置面板
安装后,DSH 设置页会出现 Remote Gateway 卡片,可完成:
- 查看运行状态(运行中 / 已停用 / 异常 / 重启中,右上角状态点实时反映)
- 启用 / 停用、一键重启——每次操作都有明确反馈("正在重启… → 重启成功",失败显示原因)
- 修改绑定 IP 与端口:保存后监听自动重启,并等待就绪后提示结果
- 管理登录账号:新增 / 修改 / 删除(删除有确认),密码自动哈希存储
- 使所有登录会话失效:一键让所有已登录设备退出(有确认),下次访问需重新登录
- 查看最近日志(每 3 秒自动刷新)
Showing the opening section of the README — the full document lives in the repository以上为 README 开头摘要,完整文档在仓库内 · View the full README on GitHub →在 GitHub 查看完整 README →
Related相关推荐
-
 Ayuilos/Miffan
RikkaHub fork,Android AI 客户端。支持 ChatGPT 订阅登录使用、跨应用划词悬浮翻译、助手工作区文件隔离、远程工作区、文档与 HTML 预览、可定制动态角色。
-
 cloveric/tarocub
The local-first answer to Grok Bot, OpenAI dots and Meta Muse: always-on personal AI bots that run on your own machine a…
-
 HuanLinOTO/dsh-plugin-aigc-canvas
provider-agnostic AIGC HTTP 桥 + 无限画布 + ffmpeg 后处理,13 个工具含画布连边/reroll/媒体编辑 | Provider-agnostic AIGC HTTP bridge + infinit…
- huermi/dsh-deepseek-web-adapter 免费的 DeepSeek 网页版(chat.deepseek.com)LLM 服务提供方,用于 DeepSeek Harness——无需 API 密钥。自动启动网关,支持工具调用和连续对话。Free DeepSeek Web (chat.d…
- Victor-770/dsh-commandcode-provider A Command Code LLM provider plugin for DeepSeek Harness (dsh) — supporting all subscription plans (incl. Go & Pro) via S…
-
 zmh2000829/DSH-agent-bridge
Use Grok Build inside DeepSeek Harness Web through ACP
-
 wenzetan/dsh-llm-newapi
NewAPI (OpenAI-compatible gateway) LLM provider plugin for DeepSeek Harness (dsh): chat-only model discovery + Web setti…
-
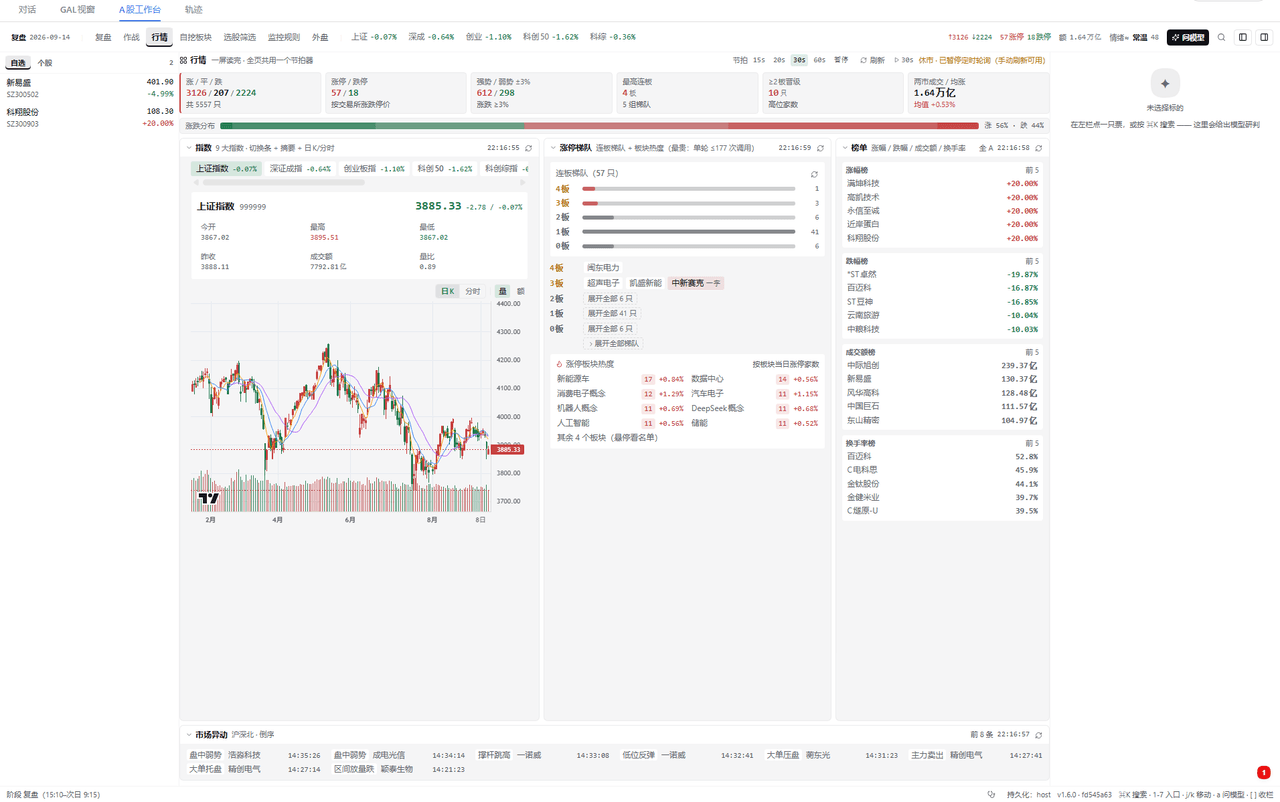 LisonEvf/dsh-stock-panel
把 DSH 会话窗口变成 A 股盯盘执行台:行情仪表盘 · 盘后复盘七步 · 模型作战思路 · 自挖板块(无监督共动聚类 + LLM 命名)· 个股工作台 · 选股筛选 · 监控提醒