fieldnote-ops/keyringseam
面向DeepSeek Harness的独立macOS钥匙串凭据提供程序,附带已签名并经过公证的通用辅助程序。
Project Overview项目介绍
KeyringSeam is a macOS credential provider plugin for DeepSeek Harness. It stores credentials in a private Apple Data Protection Keychain, requiring explicit device owner authentication for all operations. Use it for isolated credential storage on macOS. Note it is a release candidate with no completed independent security review.
这是适用于DeepSeek Harness的macOS凭证供应插件,将凭证存储在苹果私有受保护钥匙串中,每次读写操作都需要设备所有者授权验证。目前为发布候选版本,尚未经过独立安全审核,适合macOS用户测试隔离存储凭证的需求。
请帮我了解并安装插件:【keyringseam】【https://github.com/fieldnote-ops/keyringseam】Send this message to DSH in your current session. CLI install commands may not be accurate across systems — DSH will figure it out for you.把上面这条消息直接发给当前会话里的 DSH,让它帮你了解并安装。安装命令不一定准确,发给 DSH 更稳。
Or use CLI install (for developers)或使用命令行安装(适合开发者)
CLI Install命令行安装
dsh plugin --profile web add github:fieldnote-ops/keyringseam#v0.2.0-rc.1把 fieldnote-ops/keyringseam 加入你的 DSH 配置(web profile)即可启用。
READMEREADME
KeyringSeam

KeyringSeam is an independently maintained macOS credential provider for the DeepSeek Harness ctx.credentials seam. The 0.2.0-rc.1 candidate replaces the legacy file-Keychain helper with a Developer ID-signed, notarized Broker app that stores managed values in a private Data Protection Keychain access group and asks for explicit device-owner authentication before get, set, or unset.
Release status:
v0.2.0-rc.1is a public release candidate. Local Agent-isolation acceptance, DSH consumer boot, Apple notarization, stapling, Gatekeeper, quarantined native/Intel launches, and public archive hash verification have passed. The 3-machine/24-hour external acceptance round is intentionally deferred; independent security review and independent-user adoption are not claimed. The published v0.1.3 tag remains the legacy storage-only release and must not be described as Agent isolation.
KeyringSeam is an independent, AI-assisted open-source project by FIELD NOTE. It is not affiliated with, sponsored by, or endorsed by DeepSeek or Apple. DeepSeek Harness is named only to describe compatibility; macOS and Keychain are Apple trademarks.
Proof at a glance
| Surface | Verified behavior |
|---|---|
| Broker boundary | Persistent stdin/stdout framing, empty child environment, no secret-bearing argv, bounded requests/responses, serialized operations, and lifecycle disposal. |
| Keychain policy | Private exact access group TU8DF2JWHF.org.fieldnote.keyringseam.broker, Data Protection Keychain, device-only item protection, and explicit device-owner authentication for every secret-bearing operation. |
| Same-user attacks | Independent Security.framework reader returns errSecMissingEntitlement (-34018); /usr/bin/security cannot find the item; a copied raw Broker is rejected; canceled direct invocation returns -128 with no value. |
| Binary provenance | Universal arm64 + x86_64 Developer ID Application signature, Hardened Runtime, secure timestamp, embedded profile, accepted Apple notarization 8941cae5-75a5-4f1c-bdfb-998d1ce578c3, staple, Gatekeeper, and quarantine launch checks. |
| Harness integration | Isolated DSH 0.1.0-rc.6 plugin add, composed profile replacement, Web boot HTTP 200, and a DSH bash-tool attempt that failed closed without returning a value. |
Independent security review and independent-user adoption are not claimed.
Install the public release candidate
dsh is not a system-global command. Install the pinned preview CLI and pnpm in the environment where you will run Harness:
npm install --global pnpm @deepseek-ai/dsh@0.1.0-rc.6
dsh --version
pnpm --version
Install the pinned public release candidate. Use a disposable credential for the first run and review the generated profile diff before using a production credential:
dsh plugin --profile web add github:fieldnote-ops/keyringseam#v0.2.0-rc.1
The previous v0.1.3 command remains available for rollback and is explicitly legacy storage-only:
dsh plugin --profile web add github:fieldnote-ops/keyringseam#v0.1.3
Security design
- The provider launches one fixed, signed Broker app per provider lifetime over anonymous pipes. It passes no host environment and no command-line arguments to the Broker.
- Every
get,set, andunsetperforms an explicit device-owner authentication. Cancellation, timeout, missing entitlements, invalid signatures, locked Keychain, malformed frames, and native failure return errors; there is no plaintext or legacy-helper fallback. - The Broker targets macOS 13 or newer and contains Apple Silicon and Intel slices. Consumer machines do not need Swift, Xcode, or Apple command-line developer tools at runtime.
- Environment values remain read-only and highest priority. Project and user
.envfallbacks remain below the managed Keychain source. - A user who approves an unexpected authentication prompt, a compromised macOS account, debugger access to the trusted Harness host, and the trusted host itself remain outside the boundary.
Maintainer verification
npm ci
npm run check
node scripts/broker-architecture-smoke.mjs native
node scripts/broker-architecture-smoke.mjs x86_64
Building a new Broker requires the exact Developer ID identity and the approved provisioning profile:
KEYRINGSEAM_SIGN_IDENTITY='Developer ID Application: Legal Name (TEAMID)' \
KEYRINGSEAM_PROVISIONING_PROFILE='/absolute/path/to/profile.provisionprofile' \
npm run build:broker
The signed app is notarized with the locally stored keyringseam-notary profile through scripts/notarize-broker.sh. Never bypass secure timestamps or staple validation.
See Agent isolation design and SECURITY.md for the threat model, acceptance boundary, migration policy, and evidence limits.
Related相关推荐
- Nagi-ovo/voyager Enhancement suite for Gemini, AI Studio, Claude & ChatGPT — plus a prompt manager for any websites, DeepSeek Harness inc…
-
 crafter-station/petdex
A public gallery of animated pets for Codex, Claude Code, DeepSeek Harness, Hermes, OpenCode, Gemini CLI, and more.
-
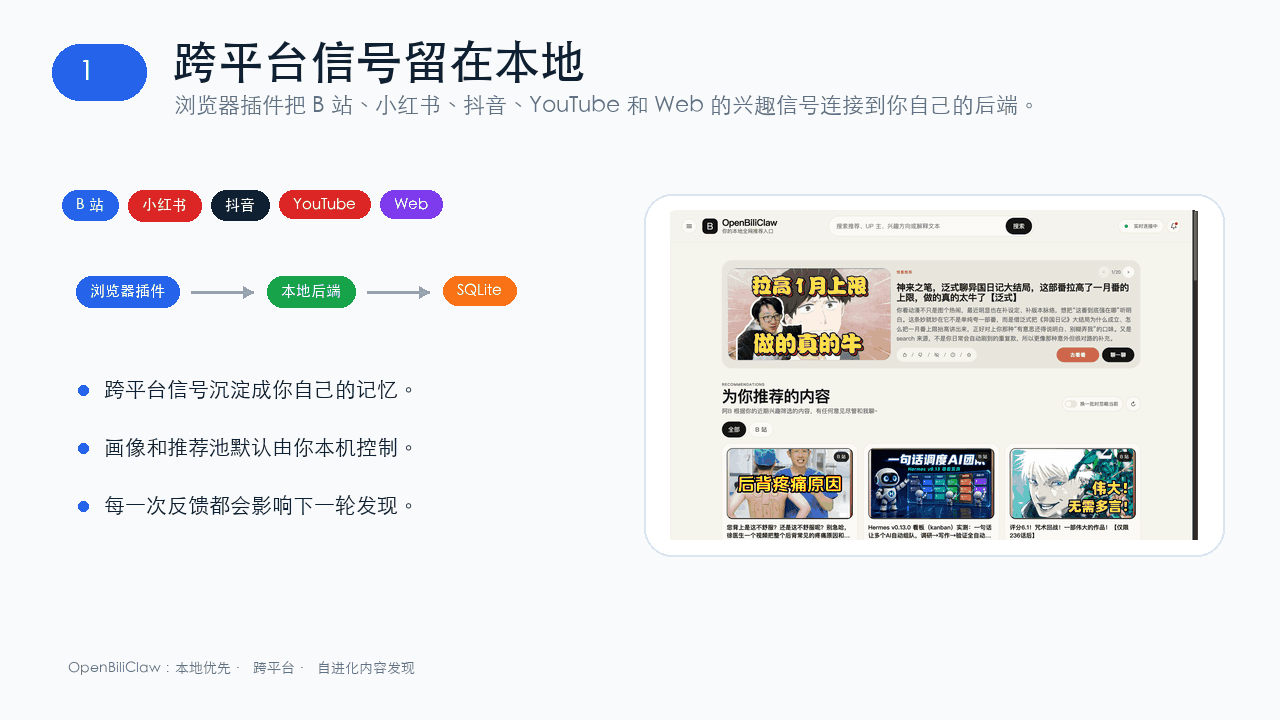 whiteguo233/OpenBiliClaw
本地私有、开源的自进化跨平台 AI 内容发现 Agent:先理解你,再主动从 B站、小红书、抖音、YouTube、X、知乎、Reddit、微博等平台与开放 Web 寻找内容。(支持 deepseek harness 插件) | Local-…
-
 edison7009/EchoBird
One-click install + model switch:Claude Code,Codex CLI (OpenAI), Grok Build (xAI), DeepSeek Harness, Kimi Code (Moonshot…
-
 V1ki/dsh-plugin-subscriptions
Use ChatGPT (Codex), Claude, and Grok (X Premium) subscriptions as DeepSeek Harness LLM providers — OAuth login in the w…
-
 Nwflower/dsh-chat-import
Import 14+ external agent chat histories (Claude Code, Codex, ChatGPT, Cursor, Gemini, Reasonix, opencode, ZCode, Grok B…
-
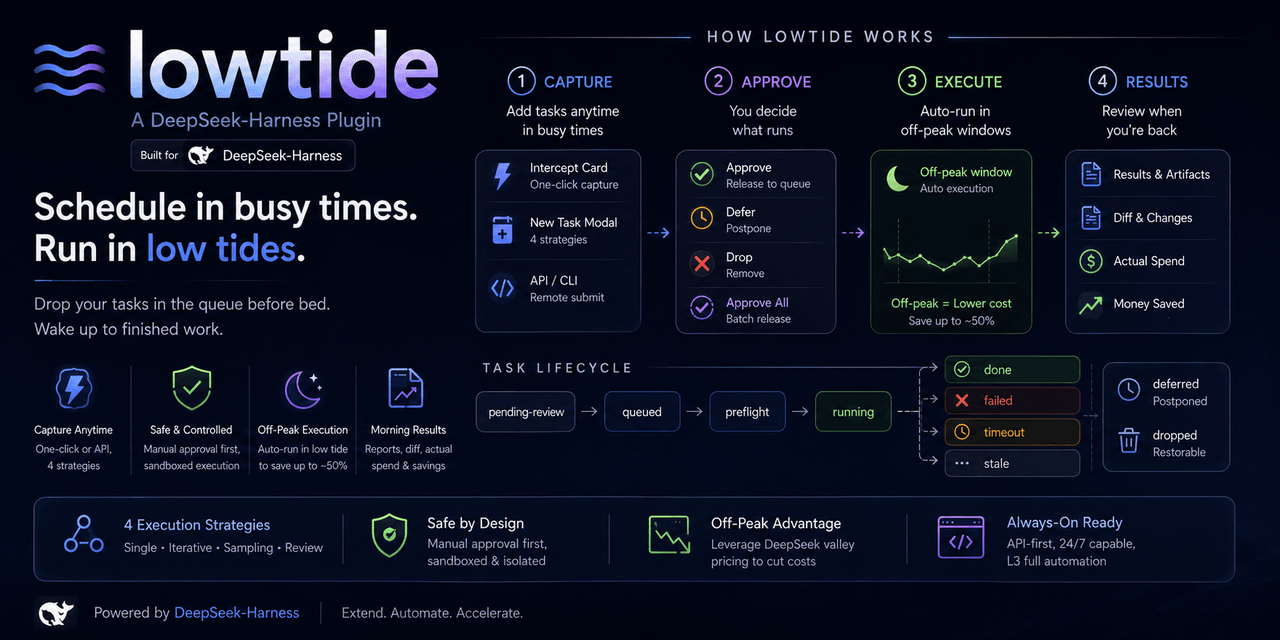 KelaoHu/dsh-lowtide
Time-shifting task delegation for DeepSeek Harness (dsh): plan tasks at leisure, they run unattended off-peak, come back…
-
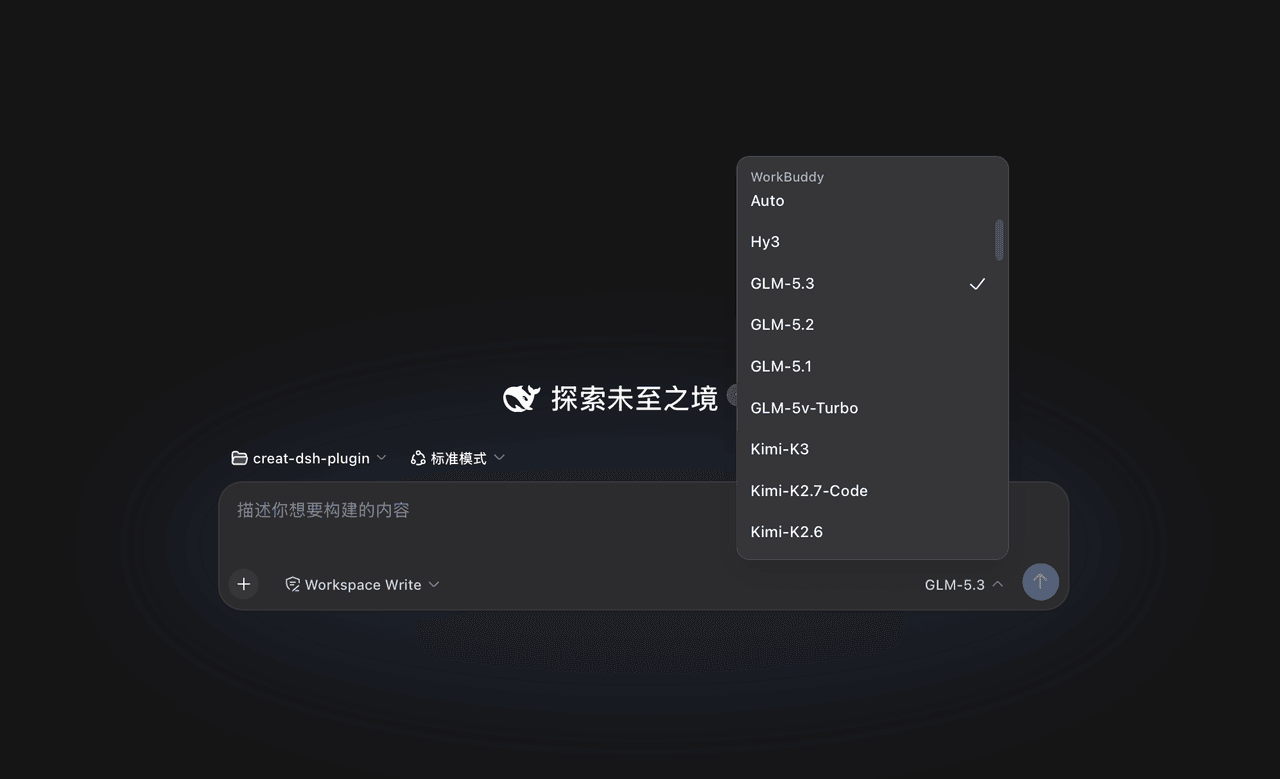 corrinehu/dsh-workbuddy-connect
将 WorkBuddy 桌面 App 包含的模型自动接入 DeepSeek Harness,零配置使用。Bring the models in the WorkBuddy desktop app into DeepSeek Harness …