hxy91819/dsh-auth
Caddy-fronted administrator authentication for DeepSeek Harness: Argon2id, revocable sessions, bilingual UI, zero upstream forks.
Project Overview项目介绍
dsh-auth is an unofficial community-built native plugin for DeepSeek Harness (DSH) that adds secure administrator authentication to the DSH web application. It locks DSH to only listen on the loopback interface, and deploys a project-owned Caddy reverse proxy with forward authentication to protect all access to pages, APIs, downloads, SSE streams, and WebSockets. To install the latest stable version, users can run sudo npm install -g dsh-auth to get the CLI, then execute sudo dsh-auth setup to start the interactive configuration process. Version 0.2.0 is a breaking release, so users with older legacy deployments must uninstall the previous version before running the new setup.
This plugin is intended for system administrators who need to add access control to a publicly deployed DSH web instance. The interactive setup workflow guides users through selecting the existing DSH systemd service, choosing an administrator initialization method, setting the public HTTPS hostname, and configuring TLS mode. Before making any changes to the host system, the installer outputs a full plan of the changes it will make and requires explicit user confirmation to proceed. Users can also run the dsh-auth plan command to preview the planned changes without making any modifications to the filesystem.
dsh-auth is released under the permissive MIT open source license. Supported deployment environments are limited to Linux systems running on x64 or ARM64 hardware, with systemd, Node.js 24.7 or newer, and DSH Web version 0.1.0-rc.7 or higher. This release supports only one administrator identity per installation, and does not include support for multiple accounts, self-service password recovery, multi-factor authentication, or multi-tenancy. All passwords are stored as Argon2id hashes, plaintext credentials are never saved to disk, and session cookies are secured with standard industry security hardening attributes.
dsh-auth 是专门为 DeepSeek Harness(DSH)开发的社区原生身份验证插件,用于为 DSH Web 应用添加安全的管理员登录功能。它将 DSH 服务限制仅在环回地址监听,同时通过项目自带的 Caddy 服务配置 forward_auth 边缘认证,保护所有页面、API、下载、SSE 流和 WebSocket 连接,避免未授权访问。当前最新版本是 0.2.0,针对旧版部署做了不兼容升级,旧配置需要重新安装。
该插件适合需要为公开部署的 DSH Web 服务添加访问控制的管理员使用。安装时需要先通过 npm 全局安装 CLI 工具,然后执行 sudo dsh-auth setup 进入交互式配置流程。安装程序会询问 DSH 服务单元、管理员初始化方式(密码或登录令牌)、HTTPS 主机名和 TLS 模式,展示预执行计划,获得用户确认后才会修改系统配置。
dsh-auth 采用 MIT 许可证开源,正常部署要求运行环境为 Linux x64 或 ARM64 架构,需要 systemd、Node.js 24.7 或更新版本,以及 DSH Web 0.1.0-rc.7 或以上版本。当前版本每个安装实例仅支持一个管理员身份,不支持多账号、多租户、自助找回账户和 MFA 等功能。密码以 Argon2id 哈希存储,不会保存明文。
请帮我安装这个 DSH 插件。安装前先完成【兼容性检查 + 安全性检查】,检查通过再动手。

插件:dsh-auth(hxy91819/dsh-auth)
仓库:https://github.com/hxy91819/dsh-auth
本站详情页:https://www.yhbd.top/plugins/hxy91819-dsh-auth/
本站登记:类型 plugin · 归类 原生 DSH 插件 · 许可证 MIT · ⭐ 6 · 最近提交 2026-09-21 · 主语言 TypeScript

按下面顺序执行,每步先把结论告诉我,再进入下一步:

【1 兼容性检查】
① 我这边:DSH 版本、Node 版本、操作系统、当前 profile(web / desktop)。
② 读它的 README、package.json、插件 manifest,列出它要求的 DSH 版本 / Node 版本 / 操作系统 / 外部依赖 / 需要另外先装的运行时。
③ 逐条比对,结论只写「满足 / 不满足 / 未知」三种;不满足的给出可行替代方案。
④ 检查是否和我已装的插件冲突:命令名重复、skill / tool 重名、端口占用、重复注册的 MCP server。

【2 安全性检查】
① 仓库可信度:和上面「本站登记」是否一致;star / fork 数、创建时间、最近提交,是否归档或长期停更。
② 安装脚本:逐行看 package.json 的 preinstall / install / postinstall,以及 install.sh、setup.ps1 之类脚本。出现 curl|bash、下载后直接执行、混淆代码、访问与插件功能无关的域名,立刻停下来告诉我,不要继续装。
③ 依赖:列出新增依赖,标出无人维护、或与知名包拼写近似的可疑包(typosquatting)。
④ 权限与副作用:它会读写哪些目录、访问哪些域名、需要哪些 DSH 权限(filesystem / network / shell / clipboard 等),以及怎么卸载和回滚。
⑤ 如果它要求 sudo / 管理员权限,或权限明显超出功能所需,先停下来问我。

【3 安装】
上面两步没有「不满足」和「高危项」时才执行;用官方推荐方式安装,不要自行提权。

【4 汇报】
用表格输出:检查项 / 结论 / 依据 / 是否需要我决策。拿不准的一律写「未知」并说明要我怎么确认——不要猜,也不要替我决定。
Send this message to DSH in your current session: it verifies compatibility and security first (answering met / not met / unknown item by item) and only installs once everything checks out — it will stop and ask you if it finds a high-risk item. The box scrolls; the copy is the full prompt. CLI install commands may not be accurate across systems, so DSH is the safer route.把上面这条消息直接发给当前会话里的 DSH:它会先核对兼容性与安全性(逐条给「满足 / 不满足 / 未知」),确认没问题再安装,有高危项会停下来问你。框内可滚动,复制到的是完整提示词;安装命令不一定准确,发给 DSH 更稳。
- Only 6 stars - very few users, little community feedback星标只有 6,几乎没人在用,遇到问题缺少社区反馈
DSH walks through these 9 checksDSH 会逐条核对这 9 项
Compatibility兼容性
- DSH, Node, OS and profile requirementsDSH 版本 / Node 版本 / 操作系统 / profile 是否满足要求
- External dependencies and runtimes (Electron / Python / Docker, ...)外部依赖与运行时(Electron / Python / Docker 等)是否齐备
- Conflicts with installed plugins: command names, skill / tool names, ports, duplicate MCP registration与已装插件是否冲突:命令名、skill / tool 重名、端口占用、重复 MCP 注册
Security安全性
- Repo matches the facts registered here; archived or abandoned?仓库是否与页面登记一致,是否归档或长期停更
- Safety of preinstall / install / postinstall and install.sh / setup.ps1preinstall / install / postinstall 与 install.sh、setup.ps1 是否安全
- curl|bash, download-then-execute, obfuscation, unrelated domains → stop immediatelycurl|bash、下载即执行、混淆代码、无关域名 → 立刻停止
- Typosquatting or unmaintained packages among the new dependencies新增依赖里有没有 typosquatting 或无人维护的包
- Requested permissions vs. what the feature actually needs申请了哪些权限、是否超出功能所需(filesystem / network / shell / clipboard)
- Any sudo / admin requirement, plus uninstall and rollback是否要求 sudo / 管理员权限,以及卸载与回滚方式
Anything uncertain must be marked unknown with a note on how to confirm it. This site's signal screen is a static snapshot, not a security audit.拿不准的必须标「未知」并说明要我怎么确认。本站的信号筛查是静态快照,不能替代安全审计。
Or use CLI install (for developers)或使用命令行安装(适合开发者)
CLI Install命令行安装
dsh plugin --profile web add github:hxy91819/dsh-auth把 hxy91819/dsh-auth 加入你的 DSH 配置(web profile)即可启用。
READMEREADME
dsh-auth
English | 简体中文


Unofficial community plugin for DeepSeek Harness. Add a secure administrator login to the DeepSeek Harness Web app. dsh-auth keeps Harness on loopback and installs a project-owned Caddy forward_auth edge for pages, APIs, downloads, SSE, and WebSockets.
Version 0.2.0 is a breaking upgrade from legacy v1 deployments. Previous installer flags, Nginx-managed installations, and old sessions are not migrated. Uninstall the previous installation, then run setup again.
Quick start
Interactive setup
Install the published CLI, then start from an existing DSH Web systemd service whose upstream listens only on loopback:
sudo npm install -g dsh-auth
sudo dsh-auth setup
npm install -g dsh-auth installs the current stable CLI, and the installer pins that same version in the selected DSH profile. For controlled production rollout, install the exact version approved by your supply-chain policy:
sudo npm install -g dsh-auth@0.2.3
Plugin pre-install is not enabled authentication
dsh plugin --profile web add dsh-auth (or a local tarball) only adds the bundle to the Web profile. With both core environment variables absent the bundle stays dormant: Web keeps booting normally, no authentication routes or settings UI appear, and nothing is exposed. A partially supplied configuration still fails loudly instead of booting. Enabling authentication always requires the globally installed CLI and sudo dsh-auth setup; the plugin command never creates secrets, installs Caddy, or protects anything.
When setup finds a pre-installed bundle whose package name, version, and build content exactly match the running CLI, it adopts it: no package is reinstalled, and the bundle keeps external ownership. Any other pre-installed build is refused before the host changes. Rollback and uninstall leave an adopted bundle in place; without managed configuration it simply returns to dormancy.
Showing the opening section of the README — the full document lives in the repository以上为 README 开头摘要,完整文档在仓库内 · View the full README on GitHub →在 GitHub 查看完整 README →
Related相关推荐
- ranxianglei/billion-context 基本稳定可用 A context-compression plugin for small context windows (a 100K context is enough), token savings (5x fewer tokens…
-
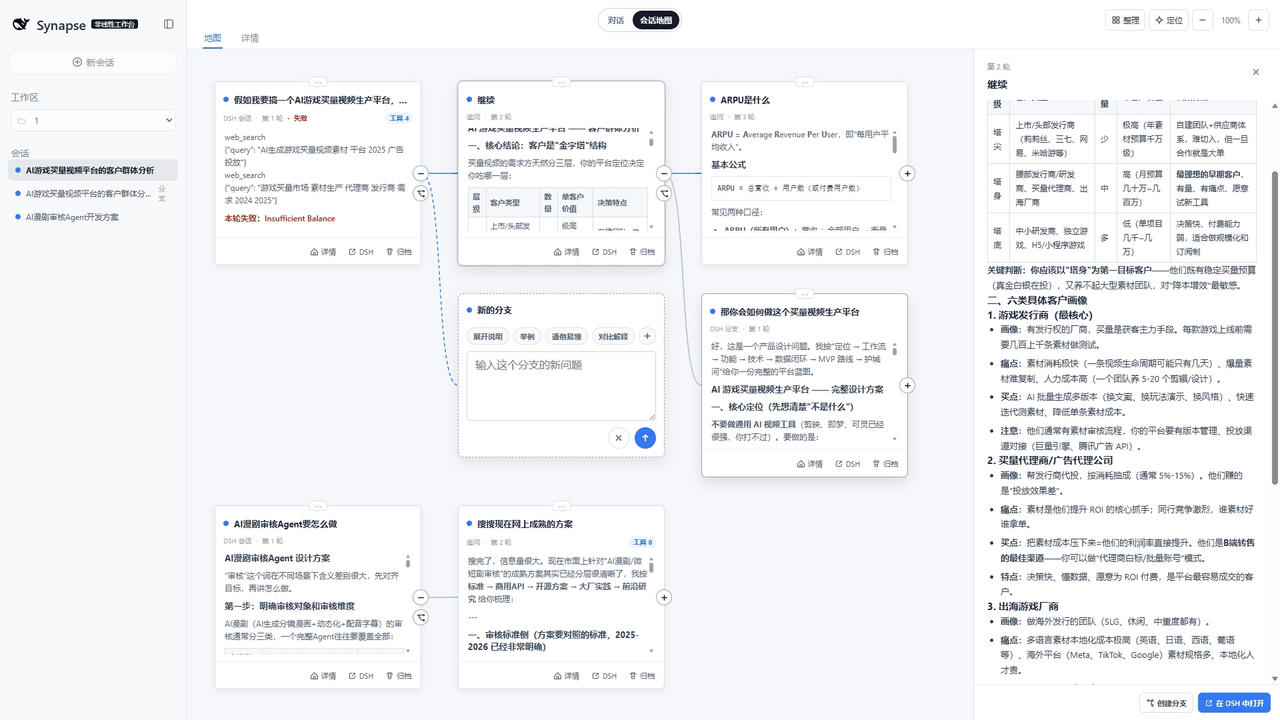 liangmianya/dsh-synapse
A visual, non-linear conversation workspace plugin for DeepSeek Harness ; A canvas-based session explorer and branching …
-
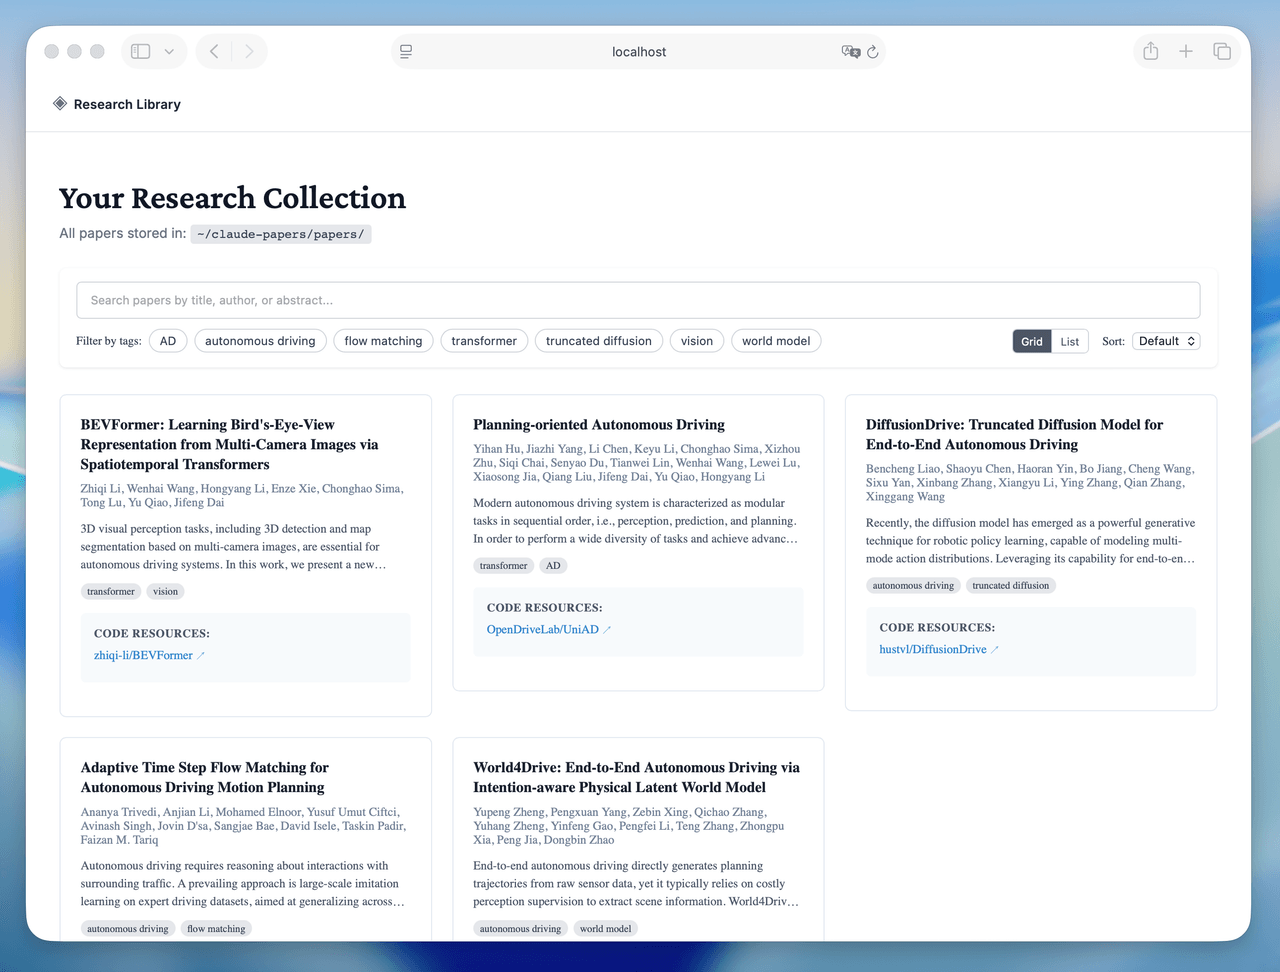 alaliqing/claude-paper
📖 Cross-agent research paper toolkit for Claude Code, Codex, OpenCode, and DeepSeek Harness—quick summaries, deep study…
-
 acryldev/acryl
ACRYL - Agent Context Relay Yielding Lifecycles. One persistent workspace, one canonical context, any coding agent.
-
 omdsh-dev/dsh-annotation
DSH Web 选中批注插件:选文字→批注→回车随消息发送;气泡隐藏批注块(零闪烁);回复按 Annotation N 逐条对照(可悬浮芯片)。官方 bundle,零核心改动
-
 Anionex/dsh-turn-rewind
deepseek harness对话和代码状态回退插件 | DSH — rewind conversation and workspace state, powered by a persistent Change Ledger
-
 Tyan66666/billion-context-dsh
Model-driven context management (Active Context Pruning / ACP) for the DeepSeek Harness — the model decides when and wha…
-
 qkycir-123/dsh-run2skill
Automatically turn successful DeepSeek Harness sessions into reusable, reviewable Agent Skills.