onlyqzq/dsh-riskproof
Risk-aware approval layer for high-risk AI Agent tool calls
Project Overview项目介绍
This is a DSH-native plugin that provides provenance-aware execution security for tool calls within the DeepSeek Harness agent framework. It hooks into DSH's native tool pipeline at the pre-execute and result stages, tracks data origins across multiple sequential tool calls, detects risky cross-tool data flows, and blocks dangerous execution before any sensitive side effects occur. To install from the current release candidate, you first build the npm tarball from source with npm pack --pack-destination artifacts, then run dsh plugin add on the generated tarball, and the plugin registers automatically after a DSH profile restart.
It adds a persistent security beacon to the side of your DSH conversation, which updates automatically every time a tool call completes. You can click the beacon any time to open a compact overview that shows call distribution statistics, the last 24 risk checks, up to three recent risk chains, and clear counts of allowed, blocked, and attention-needed calls. You can also use a set of /riskproof DSH commands to manually pull a full provenance trace, adjust task scope to read-only or local-only mode, or run an isolated demo rehearsal of risk detection. This plugin targets DSH users who want extra protection against unintended sensitive data flows across tool calls.
RiskProof is released under the permissive open-source Apache 2.0 license, so it is free to use, modify, and distribute, with no associated cost for any use case. The current 0.3.0 release candidate has been fully validated on DSH versions 0.1.0-rc.7 and 0.1.2-rc.1, and works on both Chrome desktop and narrow-viewport DSH web instances. It is important to note that RiskProof does not replace core system security tools like OS process sandboxes, network firewalls, endpoint malware scanners, or credential vaults, and it does not provide full semantic data loss prevention. It only adds provenance tracking for observable DSH tool call flows.
这是一款专为 DeepSeek Harness (DSH) 开发的原生执行安全插件,用于追踪工具输入数据的来源,检测风险跨工具数据流,在危险副作用执行前终止操作。它直接挂载到 DSH 的工具调用管道,在预执行和结果阶段介入完成污点分析与策略判定,安装后会自动在对话侧边生成持久安全 beacon 入口。你可以通过构建 npm 压缩包后使用 dsh plugin add 命令完成安装。
面向需要提升 DSH 代理工具调用安全性的开发人员与普通用户,适合关注数据泄露风险、需要拦截敏感数据跨工具流动的场景。使用时,普通工具调用会自动更新安全 beacon 状态,用户点击即可打开概览面板查看调用分布、最近风险链和统计数据,也可以通过 /riskproof 系列命令手动触发溯源报告、调整任务权限模式。插件使用确定性分析,不依赖大模型做分类判定。
本插件遵循 Apache-2.0 开源协议,无需付费使用,当前 0.3.0 版本候选已在 DSH 0.1.0-rc.7 到 0.1.2-rc.1 多个版本验证通过,支持 Chrome 桌面端和窄屏 Web 环境。它不替代操作系统沙箱、网络防火墙、端点安全等基础安全设施,也不提供全语义数据泄露防护,仅针对可观测的工具调用流程提供可配置的来源溯源防护。
请帮我安装这个 DSH 插件。安装前先完成【兼容性检查 + 安全性检查】,检查通过再动手。

插件:dsh-riskproof(onlyqzq/dsh-riskproof)
仓库:https://github.com/onlyqzq/dsh-riskproof
本站详情页:https://www.yhbd.top/plugins/onlyqzq-dsh-riskproof/
本站登记:类型 plugin · 归类 原生 DSH 插件 · 许可证 Apache-2.0 · ⭐ 7 · 最近提交 2026-09-22 · 主语言 TypeScript

按下面顺序执行,每步先把结论告诉我,再进入下一步:

【1 兼容性检查】
① 我这边:DSH 版本、Node 版本、操作系统、当前 profile(web / desktop)。
② 读它的 README、package.json、插件 manifest,列出它要求的 DSH 版本 / Node 版本 / 操作系统 / 外部依赖 / 需要另外先装的运行时。
③ 逐条比对,结论只写「满足 / 不满足 / 未知」三种;不满足的给出可行替代方案。
④ 检查是否和我已装的插件冲突:命令名重复、skill / tool 重名、端口占用、重复注册的 MCP server。

【2 安全性检查】
① 仓库可信度:和上面「本站登记」是否一致;star / fork 数、创建时间、最近提交,是否归档或长期停更。
② 安装脚本:逐行看 package.json 的 preinstall / install / postinstall,以及 install.sh、setup.ps1 之类脚本。出现 curl|bash、下载后直接执行、混淆代码、访问与插件功能无关的域名,立刻停下来告诉我,不要继续装。
③ 依赖:列出新增依赖,标出无人维护、或与知名包拼写近似的可疑包(typosquatting)。
④ 权限与副作用:它会读写哪些目录、访问哪些域名、需要哪些 DSH 权限(filesystem / network / shell / clipboard 等),以及怎么卸载和回滚。
⑤ 如果它要求 sudo / 管理员权限,或权限明显超出功能所需,先停下来问我。

【3 安装】
上面两步没有「不满足」和「高危项」时才执行;用官方推荐方式安装,不要自行提权。

【4 汇报】
用表格输出:检查项 / 结论 / 依据 / 是否需要我决策。拿不准的一律写「未知」并说明要我怎么确认——不要猜,也不要替我决定。
Send this message to DSH in your current session: it verifies compatibility and security first (answering met / not met / unknown item by item) and only installs once everything checks out — it will stop and ask you if it finds a high-risk item. The box scrolls; the copy is the full prompt. CLI install commands may not be accurate across systems, so DSH is the safer route.把上面这条消息直接发给当前会话里的 DSH:它会先核对兼容性与安全性(逐条给「满足 / 不满足 / 未知」),确认没问题再安装,有高危项会停下来问你。框内可滚动,复制到的是完整提示词;安装命令不一定准确,发给 DSH 更稳。
- Only 7 stars - very few users, little community feedback星标只有 7,几乎没人在用,遇到问题缺少社区反馈
DSH walks through these 9 checksDSH 会逐条核对这 9 项
Compatibility兼容性
- DSH, Node, OS and profile requirementsDSH 版本 / Node 版本 / 操作系统 / profile 是否满足要求
- External dependencies and runtimes (Electron / Python / Docker, ...)外部依赖与运行时(Electron / Python / Docker 等)是否齐备
- Conflicts with installed plugins: command names, skill / tool names, ports, duplicate MCP registration与已装插件是否冲突:命令名、skill / tool 重名、端口占用、重复 MCP 注册
Security安全性
- Repo matches the facts registered here; archived or abandoned?仓库是否与页面登记一致,是否归档或长期停更
- Safety of preinstall / install / postinstall and install.sh / setup.ps1preinstall / install / postinstall 与 install.sh、setup.ps1 是否安全
- curl|bash, download-then-execute, obfuscation, unrelated domains → stop immediatelycurl|bash、下载即执行、混淆代码、无关域名 → 立刻停止
- Typosquatting or unmaintained packages among the new dependencies新增依赖里有没有 typosquatting 或无人维护的包
- Requested permissions vs. what the feature actually needs申请了哪些权限、是否超出功能所需(filesystem / network / shell / clipboard)
- Any sudo / admin requirement, plus uninstall and rollback是否要求 sudo / 管理员权限,以及卸载与回滚方式
Anything uncertain must be marked unknown with a note on how to confirm it. This site's signal screen is a static snapshot, not a security audit.拿不准的必须标「未知」并说明要我怎么确认。本站的信号筛查是静态快照,不能替代安全审计。
Or use CLI install (for developers)或使用命令行安装(适合开发者)
CLI Install命令行安装
dsh plugin --profile web add dsh-riskproof@0.4.1把 onlyqzq/dsh-riskproof 加入你的 DSH 配置(web profile)即可启用。
READMEREADME
RiskProof
Provenance-aware execution security for DeepSeek Harness.
Track where tool inputs came from. Detect risky cross-tool data flows. Stop sensitive side effects before execution.
Start here
| Goal | Read |
|---|---|
| Install and try it | Quick Start · Installation |
| Tune protection and task scope | Configuration |
| Understand or contribute to the project | Architecture · Development |
| Find security boundaries and version records | Documentation index |
See protection beside your conversation
A persistent RiskProof security beacon sits beside the DSH conversation. Ordinary tool calls update it automatically. Click to open a compact overview; activity never opens it for you.
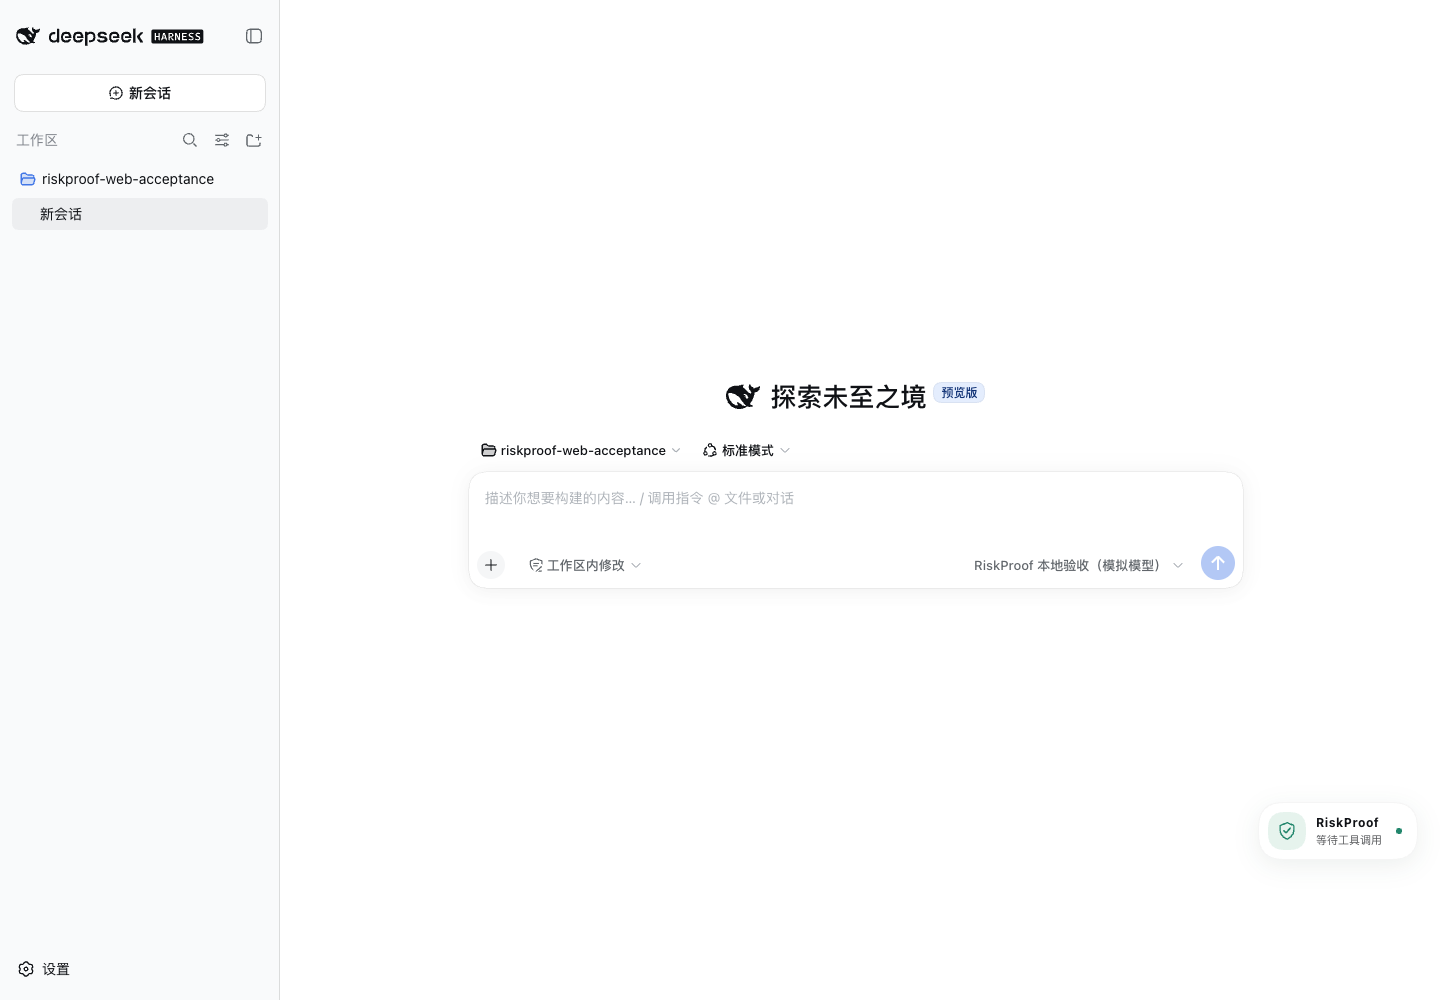
- Waits honestly for tool activity; there is no continuous simulated scan.
- Shows pending execution receipts and briefly acknowledges newly checked calls.
- Displays a call-distribution ring, the last 24 checks and up to three recent risk chains.
- Follows the selected conversation and removes stale charts when its connection is unavailable.
- Separates initial sync from disconnection, offers manual reconnect, and displays task scope and record limits.
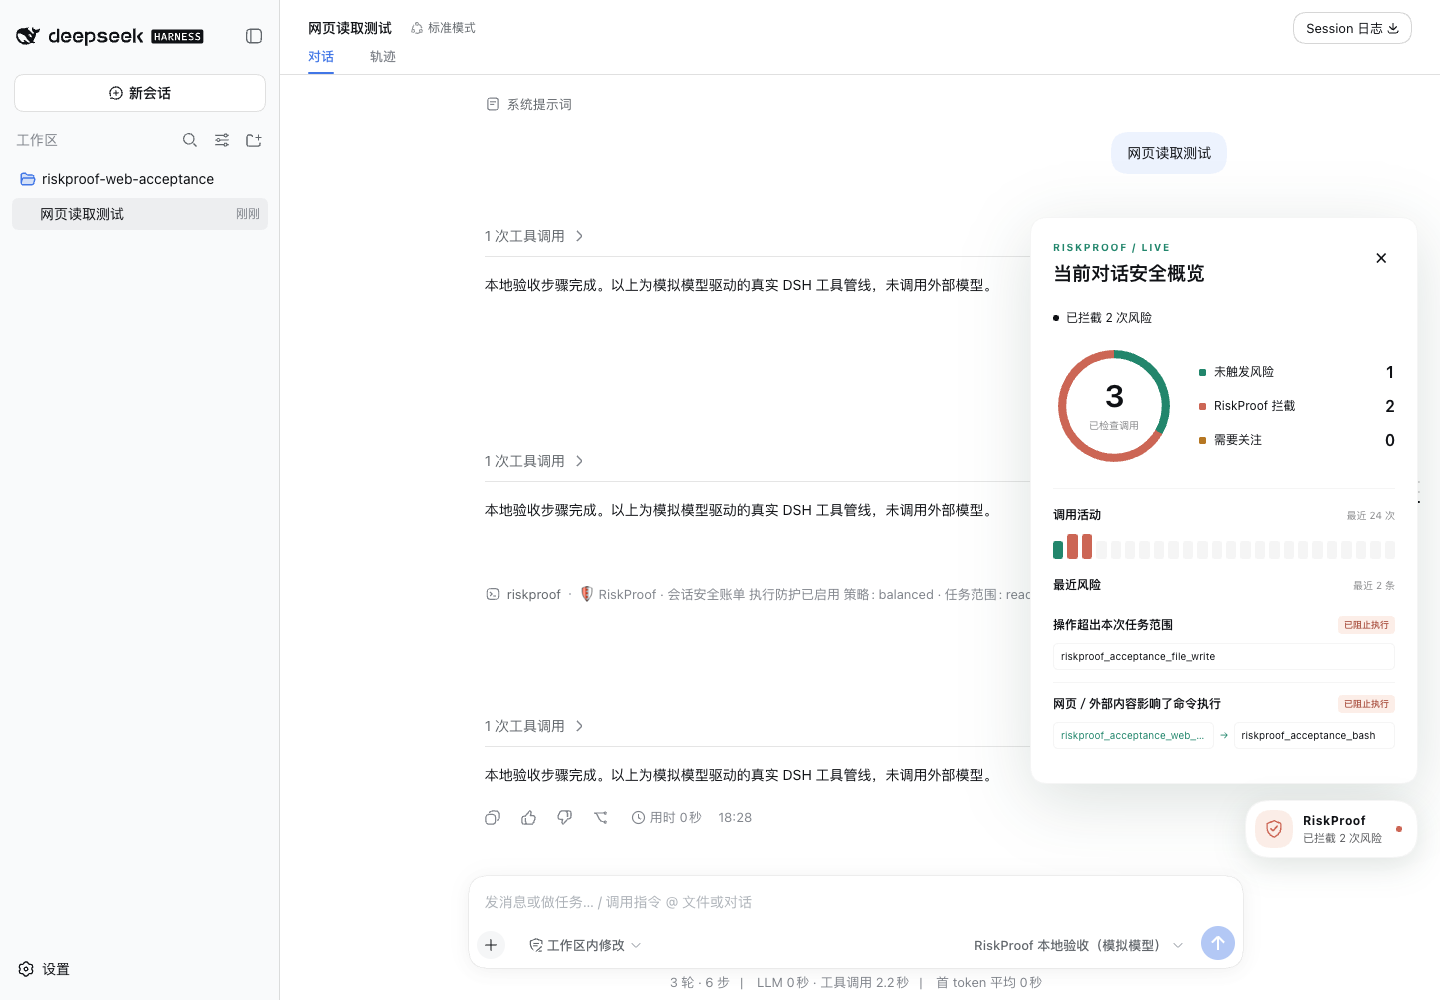
Real DSH Web screenshots; a local test model produced these records through the actual Agent/tool pipeline. Normal use does not require a rehearsal.
The chart counts calls with no triggered risk, calls blocked by RiskProof, and calls needing attention. It does not invent a safety score. Observe mode, disabled recording and disabled detection features are identified. Counts cover retained records in the current plugin run. Not triggering a rule does not establish that an operation is safe.
Commands remain secondary entries; long output is collapsed by default:
| Need | DSH command |
|---|---|
| Open the compact overview | /riskproof |
| Read the text provenance report | /riskproof trace |
| Restrict to inspection | /riskproof task read-only |
| Keep tool capabilities local | /riskproof task local-only |
| Restore ordinary task scope | /riskproof task standard |
| Optional isolated rehearsals | /riskproof demo |
Showing the opening section of the README — the full document lives in the repository以上为 README 开头摘要,完整文档在仓库内 · View the full README on GitHub →在 GitHub 查看完整 README →
Related相关推荐
-
 Minglink/dsh-infinite-gen-4
DeepSeek v4.1 flash 网络安全红队工具(无限四代) 求 Star 收藏 ⭐欢迎大家提交项目的改进
-
 kenryu42/cc-safety-net
A pre-execution guard for AI coding agents. It blocks destructive Git and file system commands, plus common attempts to …
-
 hyhmrright/brooks-lint
AI code reviews grounded in 12 classic engineering books — decay risk diagnostics with book citations, severity labels, …
-
 toby-bridges/api-relay-audit
Local security audit for AI API relays and LLM proxies: detects prompt injection, model substitution, tool-call rewritin…
-
 hashgraph-online/hol-guard
Open-source antivirus for AI agents: block risky tools, secret access, prompt injection, malicious packages, MCP servers…
-
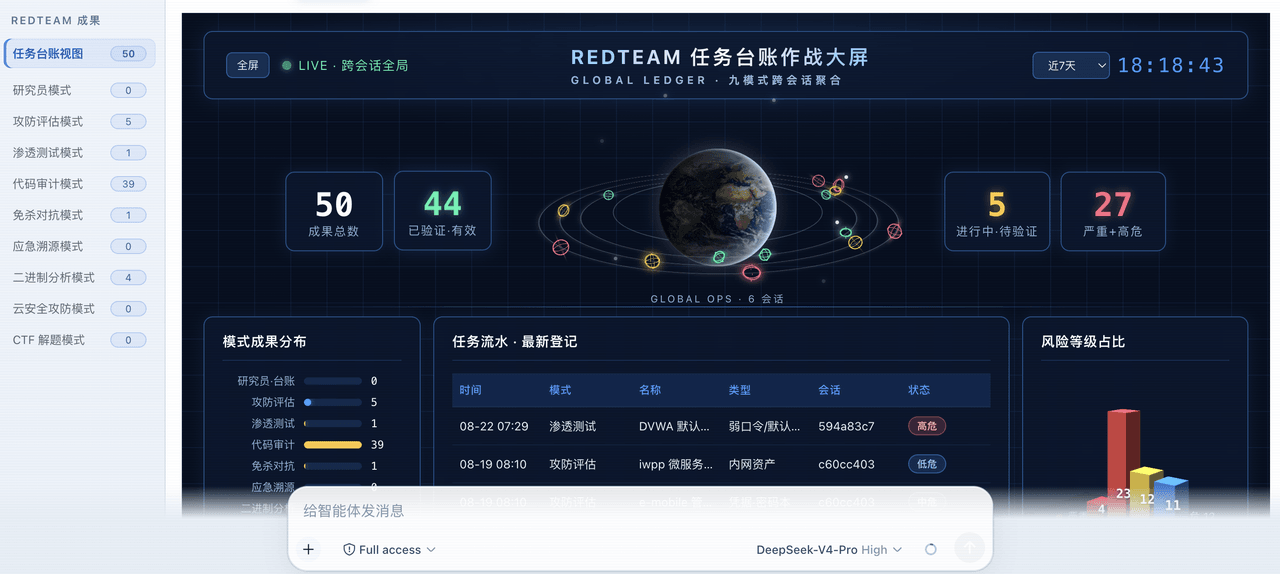 SeaOf0/dsh-redteam-model
基于dsh web实现的多种模式,目的是服务于redteam进行授权的安全研究,覆盖渗透测试、红队评估、代码审计等范围领域,请勿用于非法行为。(允许二开,赋予模块各位自己的业务逻辑,方法论只有自己熟练的才好用,好的方法论=好的生态)
-
 howmp/dsh-pentest
面向 DeepSeek Harness(dsh)的渗透测试模式 @CloverSecLabs
-
 saya-ch/dsh-mobile
DeepSeek Harness 的 Android App 与安全远程访问插件,支持局域网/远程连接和高度自定义的移动界面与扩展能力。