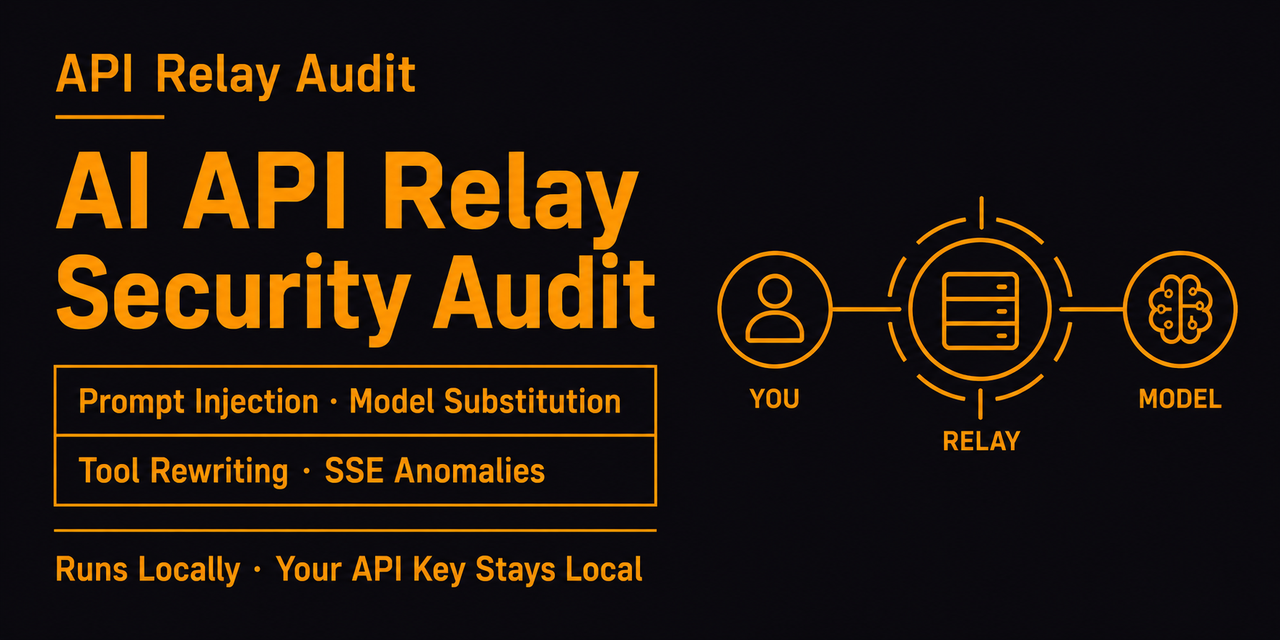
toby-bridges/api-relay-audit
针对AI API中转与LLM代理的本地安全审计:检测提示注入、模型替代、工具调用篡改、SSE异常、错误泄露及Web3钱包风险。
Project Overview项目介绍
API Relay Audit is a native plugin for DeepSeek Harness that provides local security auditing for third-party AI API relays and LLM proxies, and it also supports integration with OpenClaw and Hermes agent frameworks. It runs a series of 14 test probes against a target relay to detect hidden prompt injection, context truncation, unauthorized model substitution, and response stream anomalies. After completing the probes, it generates a human-readable Markdown report that includes evidence for each finding and ranks each risk from LOW to HIGH. To install the plugin within DSH, users can run the command dsh plugin add github:toby-bridges/api-relay-audit#v2.4.0 directly from the DSH CLI.
This tool is intended for any user that relies on a third-party AI API relay, especially developers who plan to use a relay for coding agent automation, package installation suggestions, or Web3 wallet-related operations. When using the DSH plugin, it automatically pulls the base URL, API key, and model configuration from your existing DSH provider profile, so you do not need to manually re-enter these details. It runs the full audit suite with a single slash command /relay-audit right within DSH, and outputs the report directly to your DSH workspace. For users who want a lower-cost quick check, you can add the --connectivity flag to reduce the number of probes and cut down on token usage.
The standalone version of API Relay Audit only depends on Python's standard library and the system-installed curl command, so you do not need to install any additional Python packages to run it. The project is released under the open-source AGPL-3.0 license, and there is no cost to use it for any purpose permitted by the license terms. It is important to note that this tool does not certify a relay as safe, and it does not replace manual security review or ongoing operational monitoring. Inconclusive or ambiguous probe results are left visible in the report for manual review, rather than automatically marked as clean.
API Relay Audit 是一款针对第三方 AI API 中转、LLM 代理的本地安全审计工具,同时也是 DeepSeek Harness 的原生插件,也兼容 OpenClaw、Hermes 等其他 AI 代理框架。它会检测中转服务是否存在隐藏提示注入、上下文截断、模型替换、响应异常等风险行为,最终生成带风险分级的可查阅 Markdown 审计报告。用户既可以通过 DSH 插件命令一键安装调用,也可以直接拉取独立 Python 脚本离线运行审计。
这款工具面向使用第三方 AI API 中转服务的用户,尤其是打算将中转用于编码代理自动化、包安装建议、钱包相关操作的开发者。典型工作流程是,用户指定需要审计的中转 URL、API 密钥和运行配置,工具发送多组测试探针收集中转行为数据,最终生成本地审计报告,所有敏感数据仅保存在用户本地,不会外传。用户可以根据报告结果判断中转服务是否可信,再决定是否投入正式流量使用。
该工具独立运行仅依赖 Python 标准库和系统 curl,API 密钥只会发送到用户指定的中转地址,不会留存到其他地方。项目采用 AGPL-3.0 开源许可,不收取任何费用,也不会为任何中转服务颁发安全认证,无法替代人工安全审查和线上监控。对于无法得出结论的探测结果,工具会保留在报告中供用户人工判断,不会默认标记为安全。
请帮我安装这个 DSH 插件。安装前先完成【兼容性检查 + 安全性检查】,检查通过再动手。

插件:api-relay-audit(toby-bridges/api-relay-audit)
仓库:https://github.com/toby-bridges/api-relay-audit
本站详情页:https://www.yhbd.top/plugins/toby-bridges-api-relay-audit/
本站登记:类型 plugin · 归类 原生 DSH 插件 · 许可证 AGPL-3.0 · ⭐ 865 · 最近提交 2026-10-03 · 主语言 Python

按下面顺序执行,每步先把结论告诉我,再进入下一步:

【1 兼容性检查】
① 我这边:DSH 版本、Node 版本、操作系统、当前 profile(web / desktop)。
② 读它的 README、package.json、插件 manifest,列出它要求的 DSH 版本 / Node 版本 / 操作系统 / 外部依赖 / 需要另外先装的运行时。
③ 逐条比对,结论只写「满足 / 不满足 / 未知」三种;不满足的给出可行替代方案。
④ 检查是否和我已装的插件冲突:命令名重复、skill / tool 重名、端口占用、重复注册的 MCP server。

【2 安全性检查】
① 仓库可信度:和上面「本站登记」是否一致;star / fork 数、创建时间、最近提交,是否归档或长期停更。
② 安装脚本:逐行看 package.json 的 preinstall / install / postinstall,以及 install.sh、setup.ps1 之类脚本。出现 curl|bash、下载后直接执行、混淆代码、访问与插件功能无关的域名,立刻停下来告诉我,不要继续装。
③ 依赖:列出新增依赖,标出无人维护、或与知名包拼写近似的可疑包(typosquatting)。
④ 权限与副作用:它会读写哪些目录、访问哪些域名、需要哪些 DSH 权限(filesystem / network / shell / clipboard 等),以及怎么卸载和回滚。
⑤ 如果它要求 sudo / 管理员权限,或权限明显超出功能所需,先停下来问我。

【3 安装】
上面两步没有「不满足」和「高危项」时才执行;用官方推荐方式安装,不要自行提权。

【4 汇报】
用表格输出:检查项 / 结论 / 依据 / 是否需要我决策。拿不准的一律写「未知」并说明要我怎么确认——不要猜,也不要替我决定。
Send this message to DSH in your current session: it verifies compatibility and security first (answering met / not met / unknown item by item) and only installs once everything checks out — it will stop and ask you if it finds a high-risk item. The box scrolls; the copy is the full prompt. CLI install commands may not be accurate across systems, so DSH is the safer route.把上面这条消息直接发给当前会话里的 DSH:它会先核对兼容性与安全性(逐条给「满足 / 不满足 / 未知」),确认没问题再安装,有高危项会停下来问你。框内可滚动,复制到的是完整提示词;安装命令不一定准确,发给 DSH 更稳。
- This site's static screen found no obvious risk signal (stars, license, activity, manifest)本站静态筛查没发现明显风险信号(星标、许可证、更新活跃度、清单完整度)
DSH walks through these 9 checksDSH 会逐条核对这 9 项
Compatibility兼容性
- DSH, Node, OS and profile requirementsDSH 版本 / Node 版本 / 操作系统 / profile 是否满足要求
- External dependencies and runtimes (Electron / Python / Docker, ...)外部依赖与运行时(Electron / Python / Docker 等)是否齐备
- Conflicts with installed plugins: command names, skill / tool names, ports, duplicate MCP registration与已装插件是否冲突:命令名、skill / tool 重名、端口占用、重复 MCP 注册
Security安全性
- Repo matches the facts registered here; archived or abandoned?仓库是否与页面登记一致,是否归档或长期停更
- Safety of preinstall / install / postinstall and install.sh / setup.ps1preinstall / install / postinstall 与 install.sh、setup.ps1 是否安全
- curl|bash, download-then-execute, obfuscation, unrelated domains → stop immediatelycurl|bash、下载即执行、混淆代码、无关域名 → 立刻停止
- Typosquatting or unmaintained packages among the new dependencies新增依赖里有没有 typosquatting 或无人维护的包
- Requested permissions vs. what the feature actually needs申请了哪些权限、是否超出功能所需(filesystem / network / shell / clipboard)
- Any sudo / admin requirement, plus uninstall and rollback是否要求 sudo / 管理员权限,以及卸载与回滚方式
Anything uncertain must be marked unknown with a note on how to confirm it. This site's signal screen is a static snapshot, not a security audit.拿不准的必须标「未知」并说明要我怎么确认。本站的信号筛查是静态快照,不能替代安全审计。
Or use CLI install (for developers)或使用命令行安装(适合开发者)
CLI Install命令行安装
dsh plugin --profile web add "github:toby-bridges/api-relay-audit#${DSH_PLUGIN_REF}"把 toby-bridges/api-relay-audit 加入你的 DSH 配置(web profile)即可启用。
READMEREADME
API Relay Audit
Local security audit for AI API relays and LLM proxies.
Your Agent Is Mine: what you can test locally
Your Agent Is Mine documents malicious API relays injecting payloads and exfiltrating credentials. Anthropic's September 10, 2026 report describes fraudulent Claude resellers swapping models and harvesting credentials through their client tooling. In his September 11 disclosure, co-author Chaofan Shou reports buying router data containing users' credentials.
API Relay Audit is an independent, local security audit tool for AI API relays and LLM proxies, informed by the paper. The current release checks observable relay behavior and generates a Markdown report covering:
- Prompt and context signals: hidden prompt injection, instruction override, and context truncation.
- Response integrity: changes to pinned package-command text, error-response leakage, and SSE stream anomalies.
- Reviewable findings: per-step evidence and
LOW / MEDIUM / HIGHsummaries; inconclusive probes remain visible.
See the output: example report (synthetic fixture) · Try it: run a local audit · Coverage and limits
The standalone script uses Python's standard library plus curl. Your API key
is sent only to the relay URL you choose.
Showing the opening section of the README — the full document lives in the repository以上为 README 开头摘要,完整文档在仓库内 · View the full README on GitHub →在 GitHub 查看完整 README →
Related相关推荐
-
 saya-ch/dsh-mobile
DeepSeek Harness 的 Android App 与安全远程访问插件,支持局域网/远程连接和高度自定义的移动界面与扩展能力。
-
 liguobao/ds-harness-remote
一个基于 DeepSeek Harness 插件机制构建的多端远程访问方案,通过安全、低延迟、端到端加密的 P2P 优先网络,支持从 PC、Android 和 Web 随时访问并操作远程 Harness 和 CodeX。 (A multi-…
-
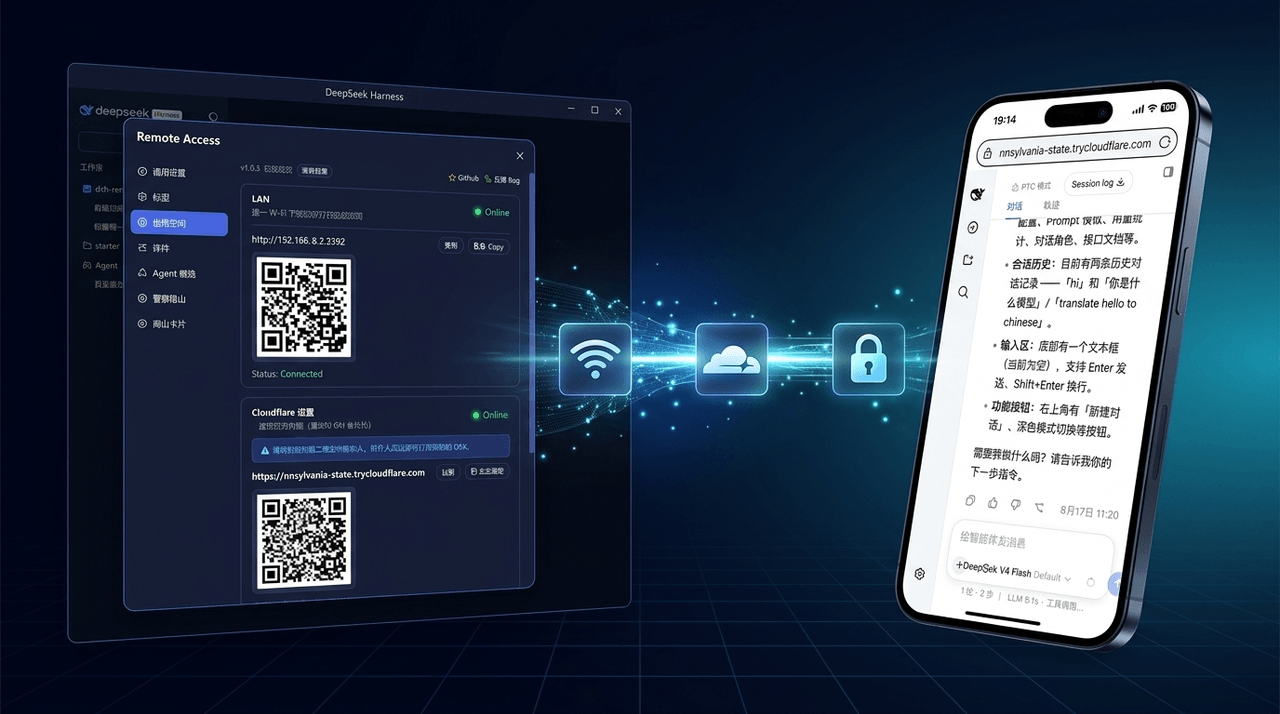 wenbin-wb/dsh-bridge
🚀 DeepSeek Harness 多通道远程访问与安全守护插件 | 局域网扫码直连、Cloudflare / 自建公网隧道、微信 / QQ / 飞书 / Telegram 机器人全生命周期对话 | 内置全协议访问安全认证、后台防篡改与…
-
 summer1238/dsh-remote-web-gateway
手机平板远程 DeepSeek Harness:扫码即可继续使用电脑上的 DSH,无需远程桌面 / SSH / 公网 IP,支持一次性配对、Github授权加密登录,独立设备授权与随时撤销,实现远程连接很简单,但安全才是我们所想要的。
-
 sorsama/deepseek-harness-mobile
Android companion for DeepSeek Harness | chat, goals, approvals & notifications from your phone, over your LAN. Kotlin +…
-
 lxzy-7/dsh-plugin-guard
Install safety net for DeepSeek Harness: pre-install snapshots, one-click/automatic rollback, guarded boot, and incident…
-
 Blank-not-black/dsh-Remote
DSH Remote · 口袋里的 DSH 控制台 会话 · 审批 · 提问 · 文件传输,局域网 / Tailscale 直连 多服务器自动选优,聊天记录离线可看 带 Token 鉴权,数据只在你的设备之间流动 Sessions · ap…
-
 PlutoKeating/dsh-lark-bot
DeepSeek Harness (dsh) 接入飞书/Lark bot,扫码即用:流式卡片、项目工作区、并行任务、多角色 Agent、跨会话通知、对话内模型/密钥管理与安全网守护(dsh 崩溃后飞书仍可自救)。A scan-to-conn…