
pandashere/dsh-self-control-guard
DeepSeek Harness 宿主退出与重启工作流自控守卫插件。
Project Overview项目介绍
This is a native DSH plugin built exclusively for DeepSeek Harness, designed to prevent accidental termination of the DSH host process by AI agents during plugin development. When agents accidentally run kill commands targeting the host, it intercepts the command before execution and blocks it permanently. It then guides the model to use controlled exit and restart tools instead of arbitrary kill commands, and leaves a full audit trail of every attempt. To install, you first build the plugin with npm install and npm pack, then add the generated tarball to your DSH profile via the official DSH CLI command.
This plugin is targeted at DSH plugin developers who work on extending the DeepSeek Harness platform. The workflow is straightforward: whenever the AI agent runs a canonical kill command targeting the host DSH process in the bash tool, the plugin catches it at the pre-execute hook and blocks it. It then injects a guidance message that teaches the agent to use the pre-registered hidden controlled exit tools instead. These tools are registered upfront but hidden from the model’s tool list, so they can only be invoked by name after the agent learns of them from the interception message.
The plugin requires Node.js 22 or newer, and version 0.1.0-rc.6 of @deepseek-ai/dsh to run, and it is released under the open-source MIT license. It is designed as a UX interception layer, not a security boundary, so it only intercepts literal kill commands and does not handle dynamic construction like variable splicing or direct system calls. Installing from a source link is not supported, so you must always build and pack it to a tarball before installing it to your DSH profile. It has no browser bundle, so you will need to verify its activation in the DSH web plugin settings after installation.
这是一个专为DeepSeek Harness(DSH)开发的原生安全插件,核心功能是防止DSH插件开发过程中AI代理意外杀死DSH宿主进程,避免任务中断和工作内容丢失。它会拦截bash工具中高置信度的宿主终止尝试,强硬拒绝执行对应命令,同时引导模型使用受控的退出和重启工具,并留下完整审计痕迹。它自带DSH插件打包清单,可按照官方流程安装到任意DSH配置文件中使用。
该插件主要面向DSH插件开发者,工作流十分清晰:当AI代理在bash中输入杀死宿主进程的命令(如kill $PPID、pkill dsh、killall dsh等),插件会在命令执行前拦截并拒绝执行,同时向模型注入引导信息,告知它使用dsh_self_exit和可选的dsh_self_restart工具完成受控退出。这两个工具提前注册但默认隐藏,不会出现在模型工具列表中,只有模型通过引导信息得知名称后才能调用。
该插件依赖Node.js 22或更高版本,以及v0.1.0-rc.6版本的@deepseek-ai/dsh,采用MIT许可证开源。它仅拦截字面形式的终止命令,不处理动态构造的变量拼接、编码、系统调用等场景,设计定位是UX拦截层而非安全边界。使用者需要通过npm打包生成tar包后,再通过DSH CLI命令安装到目标配置文件中,不支持源码链接安装。
请帮我安装这个 DSH 插件。安装前先完成【兼容性检查 + 安全性检查】,检查通过再动手。

插件:dsh-self-control-guard(pandashere/dsh-self-control-guard)
仓库:https://github.com/pandashere/dsh-self-control-guard
本站详情页:https://www.yhbd.top/plugins/pandashere-dsh-self-control-guard/
本站登记:类型 plugin · 归类 原生 DSH 插件 · 许可证 MIT · ⭐ 4 · 最近提交 2026-08-13 · 主语言 TypeScript

按下面顺序执行,每步先把结论告诉我,再进入下一步:

【1 兼容性检查】
① 我这边:DSH 版本、Node 版本、操作系统、当前 profile(web / desktop)。
② 读它的 README、package.json、插件 manifest,列出它要求的 DSH 版本 / Node 版本 / 操作系统 / 外部依赖 / 需要另外先装的运行时。
③ 逐条比对,结论只写「满足 / 不满足 / 未知」三种;不满足的给出可行替代方案。
④ 检查是否和我已装的插件冲突:命令名重复、skill / tool 重名、端口占用、重复注册的 MCP server。

【2 安全性检查】
① 仓库可信度:和上面「本站登记」是否一致;star / fork 数、创建时间、最近提交,是否归档或长期停更。
② 安装脚本:逐行看 package.json 的 preinstall / install / postinstall,以及 install.sh、setup.ps1 之类脚本。出现 curl|bash、下载后直接执行、混淆代码、访问与插件功能无关的域名,立刻停下来告诉我,不要继续装。
③ 依赖:列出新增依赖,标出无人维护、或与知名包拼写近似的可疑包(typosquatting)。
④ 权限与副作用:它会读写哪些目录、访问哪些域名、需要哪些 DSH 权限(filesystem / network / shell / clipboard 等),以及怎么卸载和回滚。
⑤ 如果它要求 sudo / 管理员权限,或权限明显超出功能所需,先停下来问我。

【3 安装】
上面两步没有「不满足」和「高危项」时才执行;用官方推荐方式安装,不要自行提权。

【4 汇报】
用表格输出:检查项 / 结论 / 依据 / 是否需要我决策。拿不准的一律写「未知」并说明要我怎么确认——不要猜,也不要替我决定。
Send this message to DSH in your current session: it verifies compatibility and security first (answering met / not met / unknown item by item) and only installs once everything checks out — it will stop and ask you if it finds a high-risk item. The box scrolls; the copy is the full prompt. CLI install commands may not be accurate across systems, so DSH is the safer route.把上面这条消息直接发给当前会话里的 DSH:它会先核对兼容性与安全性(逐条给「满足 / 不满足 / 未知」),确认没问题再安装,有高危项会停下来问你。框内可滚动,复制到的是完整提示词;安装命令不一定准确,发给 DSH 更稳。
- Only 4 stars - very few users, little community feedback星标只有 4,几乎没人在用,遇到问题缺少社区反馈
DSH walks through these 9 checksDSH 会逐条核对这 9 项
Compatibility兼容性
- DSH, Node, OS and profile requirementsDSH 版本 / Node 版本 / 操作系统 / profile 是否满足要求
- External dependencies and runtimes (Electron / Python / Docker, ...)外部依赖与运行时(Electron / Python / Docker 等)是否齐备
- Conflicts with installed plugins: command names, skill / tool names, ports, duplicate MCP registration与已装插件是否冲突:命令名、skill / tool 重名、端口占用、重复 MCP 注册
Security安全性
- Repo matches the facts registered here; archived or abandoned?仓库是否与页面登记一致,是否归档或长期停更
- Safety of preinstall / install / postinstall and install.sh / setup.ps1preinstall / install / postinstall 与 install.sh、setup.ps1 是否安全
- curl|bash, download-then-execute, obfuscation, unrelated domains → stop immediatelycurl|bash、下载即执行、混淆代码、无关域名 → 立刻停止
- Typosquatting or unmaintained packages among the new dependencies新增依赖里有没有 typosquatting 或无人维护的包
- Requested permissions vs. what the feature actually needs申请了哪些权限、是否超出功能所需(filesystem / network / shell / clipboard)
- Any sudo / admin requirement, plus uninstall and rollback是否要求 sudo / 管理员权限,以及卸载与回滚方式
Anything uncertain must be marked unknown with a note on how to confirm it. This site's signal screen is a static snapshot, not a security audit.拿不准的必须标「未知」并说明要我怎么确认。本站的信号筛查是静态快照,不能替代安全审计。
Or use CLI install (for developers)或使用命令行安装(适合开发者)
CLI Install命令行安装
dsh plugin --profile web add github:pandashere/dsh-self-control-guard把 pandashere/dsh-self-control-guard 加入你的 DSH 配置(web profile)即可启用。
READMEREADME
self-control-guard
English | 中文
A self-control guard for the DeepSeek Harness host process.
Why
When developing DSH plugins, an agent frequently — by accident or by a misfired command — kills its own host process (pkill dsh, kill -9 <host-pid>, kill $PPID, killall dsh). The session dies mid-task, work is lost, and there is no audit trail. This plugin is designed to prevent agent self-termination: it intercepts high-confidence host-kill attempts from the bash tool, hard-denies them, teaches the model the controlled exit tool, and leaves an audit trail.
It does three things:
- Intercepts high-confidence attempts to terminate the host from the
bashtool (canonicalkill <host-pid>,kill $PPID,pkill dsh,killall dshforms) with a monotonic hard denial that nopre-executelistener can force-allow. - Teaches the model the controlled tools —
dsh_self_exitalways, anddsh_self_restartonly whenrestartEnabled: true(hidden by default — TBD, see Known Limitations) — by injecting a pinned guidance message right after an interception. The tools are registered up front but hidden: they never appear in the model-facing tool list (hidden: truekeeps them out ofschemas()), so an unassisted model cannot discover them by enumeration — yet they stay callable by name, so a caller that learns them from outside the tool list (the guard's denial text, a user instruction, another tool) can invoke them immediately. - Runs a token-confirmed graceful exit/restart through the launcher's existing seams: the headless runner's
ctx.headlessIo.exit(code)(code-exact) on one-shot runs, and the launcher'sSIGTERMgraceful shutdown on long-lived surfaces (web).
Design stance: this is a UX/interception layer, not a security boundary. The matcher recognizes canonical kill forms at the simple-command level inside a bounded shell command list (; && || | |& &, newlines, comments, quoting, ( list ) / { list; } groups, redirections (target word opaque)); dynamic construction ($VAR, $(...), backticks, globs, heredocs), shell functions, unsupported compound syntax, and parser-limit failures abstain. Variable splicing, encodings, interpreters, process-group signals, PTY, MCP, Code Runtime, cordis_mount, and direct syscalls are all documented out-of-scope (see Interception coverage and Known Limitations). The OS can always kill the host; the guard's job is to make the model reach for the controlled tools instead, and to leave an audit trail when it does.
Showing the opening section of the README — the full document lives in the repository以上为 README 开头摘要,完整文档在仓库内 · View the full README on GitHub →在 GitHub 查看完整 README →
Related相关推荐
-
 PerryLink/dsh-auto-review
Second-model AI auto-review for DeepSeek Harness approval requests: a read-only reviewer subagent returns structured all…
-
 PerryLink/dsh-mcp-panel
MCP management console for the official DeepSeek Harness MCP client: /mcp command with health diagnostics and pipeline t…
- LaplaceYoung/oh-my-dsh oh-my-dsh:面向 DSH (DeepSeek Harness) 的插件生态——700+ 插件,只通过扩展接缝注册,不修改 agent-loop 骨架
-
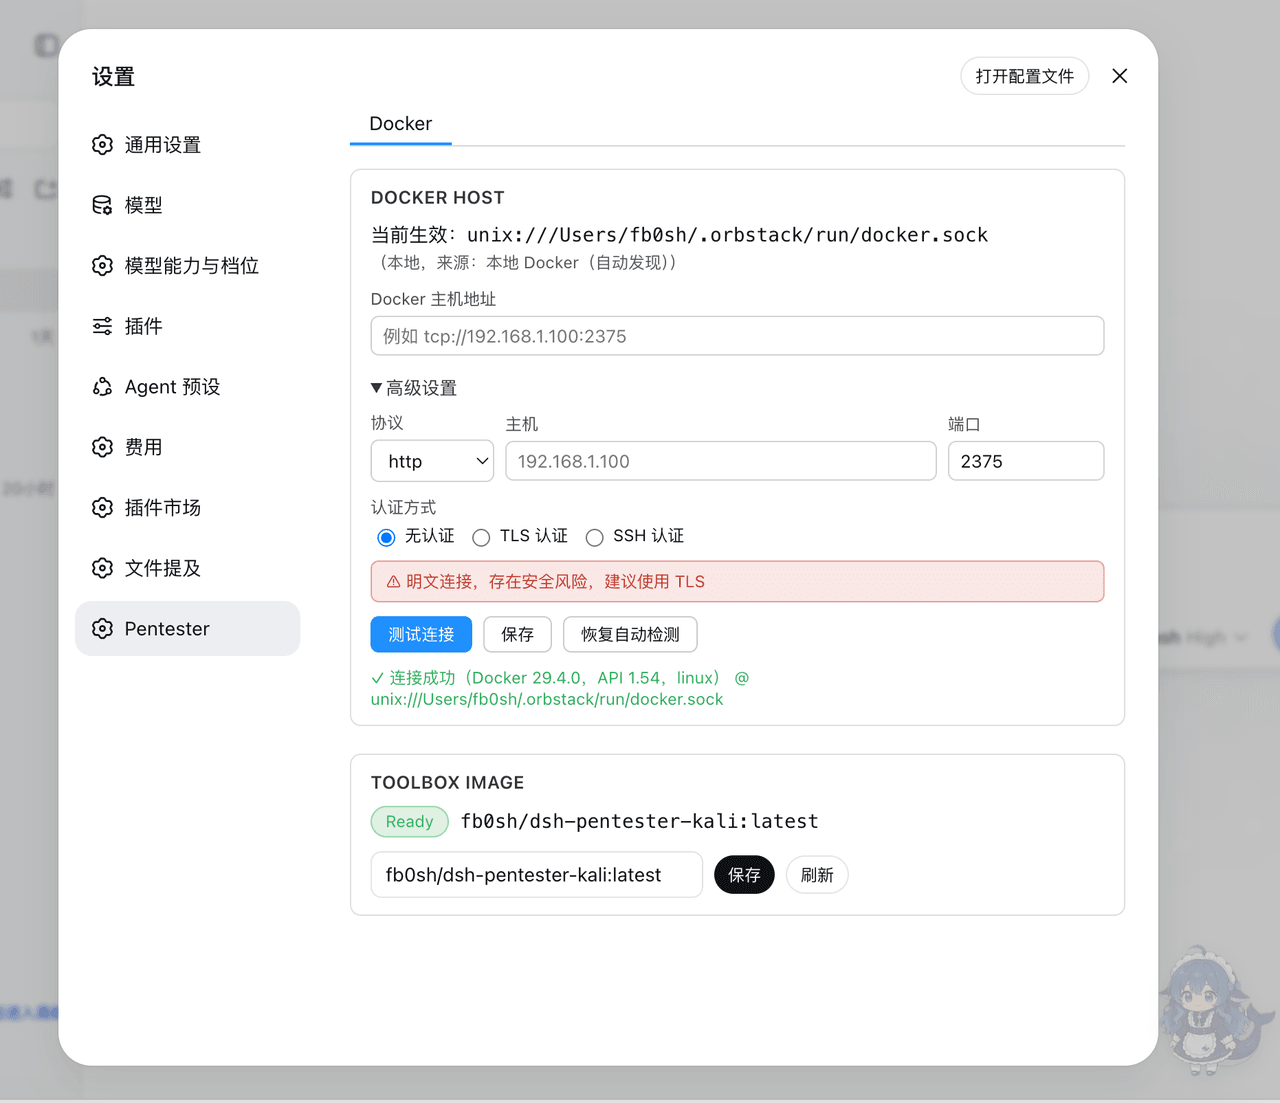 fb0sh/dsh-pentester
基于 DeepSeek Harness 的多 Agent PTES 渗透测试编排插件,支持自动化侦察、漏洞分析、验证与报告,使用 Docker/Kali 隔离工具箱 | Multi-agent PTES penetration testin…
-
 shaokeyibb/dsh-plugin-product-subagents
Role-based Codex / Claude Code / ACP subagent providers for the DeepSeek Harness — continuable children, durable session…
- PerryLink/dsh-skill-pack-security Security-audit skill pack + plugin_vet supply-chain gate for DeepSeek Harness (dsh): 8 bilingual agent skills (secret sc…
-
 lusblead/dsh-Kingdom
在 DSH 中建立属于你的 Agent 王国——让 Agent 拥有角色、权限、领地与治理秩序,并通过事实验证机制与权威账本,让每一次执行、声明与裁决都可核验、可追溯。
-
 JayZz210l/deepseek-harness-for-ide
把 DeepSeek Harness 完整搬进 JetBrains IDE:智能体对话、工具审批、目标与计划、子智能体与 Workflow。装插件、配一次 API Key,即可对话。DeepSeek Harness — agent chat…