ateen18/dsh-plugin-security-review
A security review plugin for DeepSeek Harness (dsh) plugins. Once installed, every other plugin is statically reviewed before it is installed or loaded: dangerous code, vulnerabilities, and supply-chain risks are analyzed, a review report is produced, and an install recommendation is given. At runtime it keeps auditing the installed
catalog descriptioncatalog 简介 / catalog description:Security review gate for DeepSeek Harness (dsh) plugins: static pre-install vetting of malicious code, vulnerabilities and supply-chain risks (with deobfuscation decoding), runtime audit, optional tool-call guard, and a one-click web review/install/uninstall panel.
Project Overview项目介绍
dsh-plugin-security-review is a security gate for DeepSeek Harness plugins. It provides three layers: pre-install static review of source for dangerous code, vulnerabilities, and supply-chain risks with deobfuscation decoding; runtime auditing that disables dangerous plugins via managed cordis patches; and in-session tools plus a web panel for reviewing, installing, and uninstalling plugins. Use it when vetting untrusted plugin sources or enforcing centralized plugin risk policy. Note: static analysis cannot cover native binaries, runtime-downloaded code, or heavily obfuscated payloads, so block verdicts indicate strong risk signals, not proven malice.
dsh-plugin-security-review 是 DeepSeek Harness 的安全审查插件,提供三层防护:安装前静态审查危险代码、漏洞与供应链风险(含反混淆解码),运行时持续审计并自动禁用危险插件,会话内支持工具调用审查与一键网页面板管理。在安装来源不可信的插件或需要集中管控插件风险时使用。注意:静态分析无法覆盖原生二进制、运行时下载代码及重度混淆载荷,阻断仅代表存在强风险信号,并非恶意定论;首次启动时早于本插件加载的插件可能有短暂运行窗口,下次启动由托管 patch 块阻止。
请帮我了解并安装插件:【dsh-plugin-security-review】【https://github.com/ateen18/dsh-plugin-security-review】Send this message to DSH in your current session. CLI install commands may not be accurate across systems — DSH will figure it out for you.把上面这条消息直接发给当前会话里的 DSH,让它帮你了解并安装。安装命令不一定准确,发给 DSH 更稳。
Or use CLI install (for developers)或使用命令行安装(适合开发者)
CLI Install命令行安装
dsh-safe-plugin add dsh-plugin-security-review把 ateen18/dsh-plugin-security-review 加入你的 DSH 配置(web profile)即可启用。
READMEREADME
dsh-plugin-security-review

Security review gate for dsh plugins — static pre-install vetting of malicious code, vulnerabilities and supply-chain risks (with deobfuscation decoding), runtime audit, optional tool-call guard, and a one-click web review/install/uninstall panel.
A security review plugin for DeepSeek Harness (dsh) plugins. Once installed, every other plugin is statically reviewed before it is installed or loaded: dangerous code, vulnerabilities, and supply-chain risks are analyzed, a review report is produced, and an install recommendation is given. At runtime it keeps auditing the installed roster and disables dangerous plugins.
See README.zh.md for the Chinese quick start.
Full user guides:
- English: docs/USER_GUIDE.en.md
- 中文(简体): docs/使用说明.md
Three layers
| Layer | When | What it does |
|---|---|---|
| 1. Install gate | before install (dsh-safe-plugin add) |
downloads source without running any install scripts, analyzes it, prints the report; block refuses the install, warn needs confirmation, pass forwards to dsh plugin add --ignore-scripts |
| 2. Runtime gate | after dsh boots | audits every out-of-tree plugin in the profile (cached); blocked plugins are disabled via loader.update(id,{disabled:true}) and written into a managed disabled: true block in the profile's cordis.patch.yml, so their code is never imported on the next boot |
| 3. In-session tools | during sessions | security_review / security_review_status tools review any plugin/source directory and read historical reports |
Install
dsh-safe-plugin add dsh-plugin-security-review
# or: dsh plugin --profile web add dsh-plugin-security-review
The package declares dsh.bundle, so the dsh plugin manager joins it into
dsh.profile.bundles automatically.
Review and install other plugins
dsh-safe-plugin add dsh-plugin-foo       # review + install
dsh-safe-plugin add ./local-plugin-dir
dsh-safe-plugin add https://github.com/me/plugin.git
dsh-safe-plugin review dsh-plugin-foo   # review only
dsh-safe-plugin review . --ignore test/fixtures   # skip fixtures dirs
dsh-safe-plugin list                    # historical reports
dsh-safe-plugin verify                  # re-review installed plugins
Reports
- Score (0-100), verdict
pass / warn / block / audit, per-finding detail (severity, category, file:line, snippet, recommendation) and an install recommendation. - Persisted under
$DSH_HOME/security-review/:reports/latest/<name>.md(markdown),reports/history/*.json,index.json. - The web settings UI gains a
security-reviewsection (policy, auto-disable switch, allowlist).
Known limitations
- Static analysis cannot cover native binaries, runtime-downloaded code, or
heavily obfuscated payloads;
blockmeans strong risk signals, not proof of malice. - The runtime gate deterministically blocks plugin imports that happen after
this plugin applies; plugins that start earlier in the same boot batch
load for a few milliseconds before the boot audit disables them, and the
managed patch block keeps them from loading on the next boot. Use
dsh-safe-plugin addfor deterministic pre-install blocking. - Blocking a plugin that provides services other rows
injectfails boot loudly with the missing service named — that is dsh's fail-loud contract. - Transitive dependencies are checked by name heuristics only (no full source scan of the whole dependency tree).
- A review-engine failure degrades to
warn(fail-open) so the reviewer itself can never brick dsh; re-check withdsh-safe-plugin verify.
Development
npm test # analyzer unit tests (no dsh needed; run from this dir)
License: MIT
Related相关推荐
-
 Minglink/dsh-infinite-gen-4
DeepSeek v4.1 flash 网络安全红队工具(无限四代) — jailbreak prompts and test suite for DeepSeek 求 Star 收藏 ⭐欢迎大家提交项目的改进
-
 toby-bridges/api-relay-audit
Local security audit for AI API relays and LLM proxies: detects prompt injection, model substitution, tool-call rewritin…
-
 howmp/dsh-pentest
面向 DeepSeek Harness(dsh)的渗透测试模式 @CloverSecLabs
-
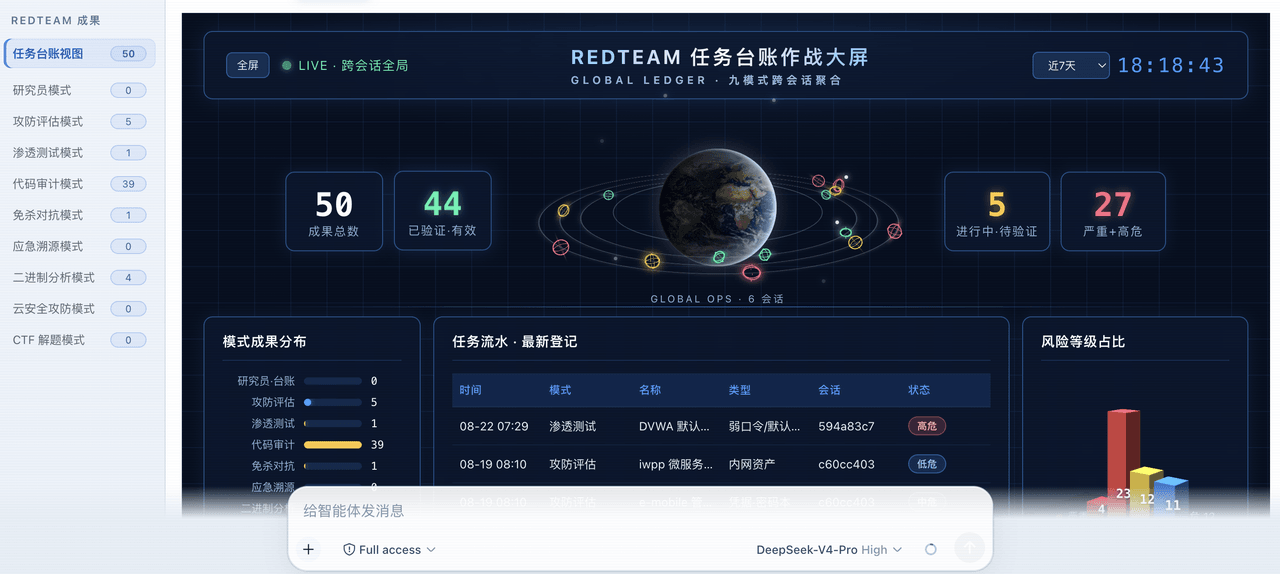 SeaOf0/dsh-redteam-model
基于dsh web实现的多种模式,目的是服务于redteam进行授权的安全研究,覆盖渗透测试、红队评估、代码审计等范围领域,请勿用于非法行为。(允许二开,赋予模块各位自己的业务逻辑,方法论只有自己熟练的才好用,好的方法论=好的生态)
-
 saya-ch/dsh-mobile
DeepSeek Harness 的 Android App 与安全远程访问插件,支持局域网/远程连接和高度自定义的移动界面与扩展能力。
-
 liguobao/ds-harness-remote
一个基于 DeepSeek Harness 插件机制构建的多端远程访问方案,通过安全、低延迟、端到端加密的 P2P 优先网络,支持从 PC、Android 和 Web 随时访问并操作远程 Harness 和 CodeX。 (A multi-…
-
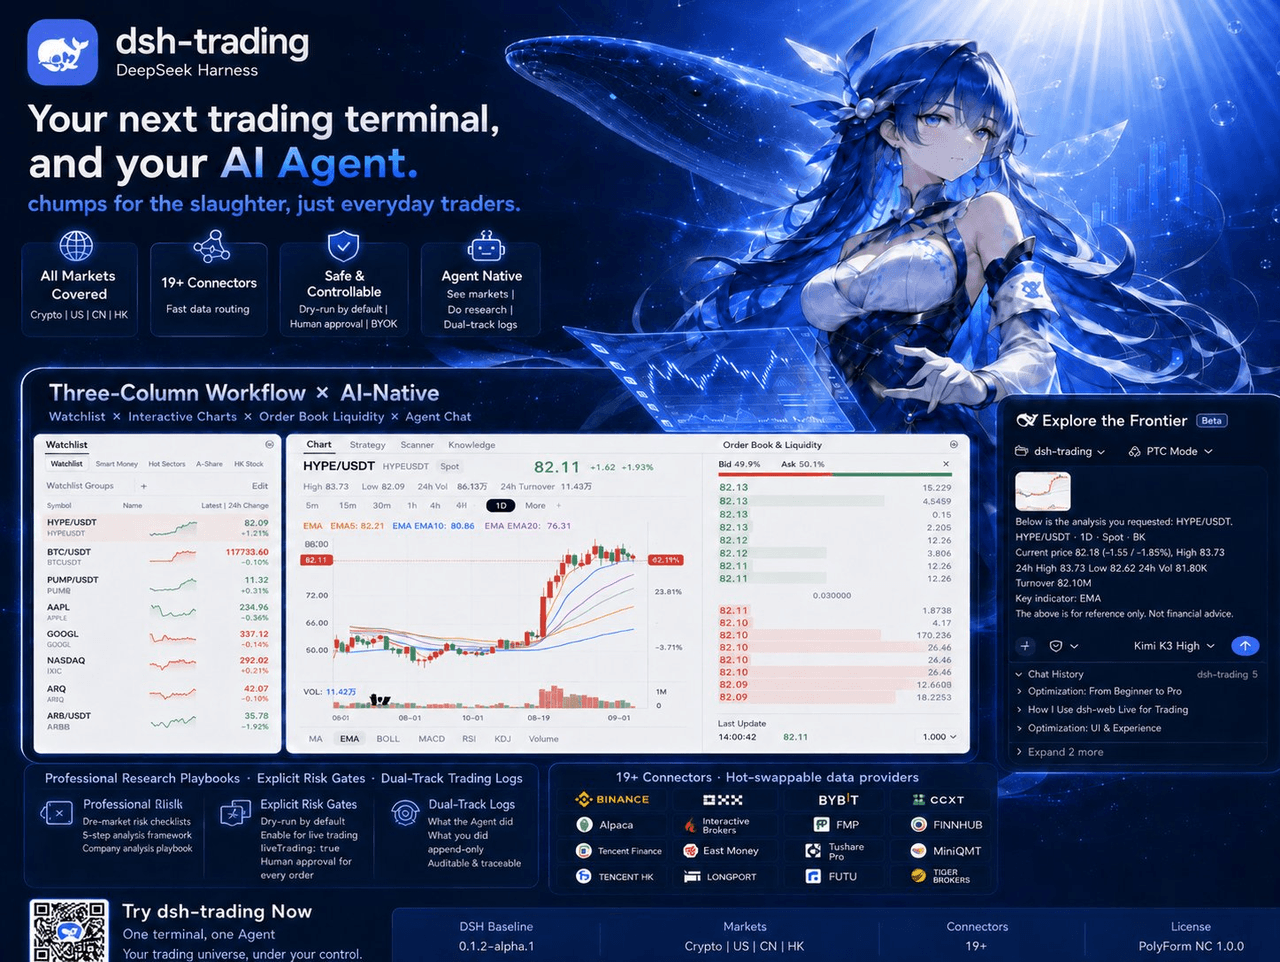 zhu1090093659/dsh-trading
Agent-native trading terminal built on DeepSeek Harness. Crypto, US, CN and HK in one three-column GUI, 19+ hot-swappabl…
-
 PerryLink/dsh-auto-review
Second-model AI auto-review for DeepSeek Harness approval requests: a read-only reviewer subagent returns structured all…