deCOLE118/dsh-sitemap
在 DSH 侧边栏一键打开「站点地图」:按主机树形组织工作区侦察到的接口,每个站点有专属配色,支持搜索、接口详情(方法 / 参数 / 出现次数 / 来源)、一键复制 curl;还带一个 Cookie 保险库——导入浏览器导出的 cookie 后自动标注哪些站点能带着身份访问,src 工作流可以直接自取 cookie 注入浏览器测试。
catalog descriptioncatalog 简介 / catalog description:站点地图(Yakit 风格):DeepSeek Harness 侧边栏树形接口地图,搜索 / 接口详情 / 一键复制 curl,数据实时同步
Project Overview项目介绍
This is a native plugin built exclusively for DeepSeek Harness (DSH) that ports Yakit’s popular sitemap interaction into the DSH environment. It organizes interfaces discovered during workspace reconnaissance into a host-based tree structure, with features for real-time search, viewing full interface details like HTTP methods, parameters, occurrence counts and sources, and one-click copying of curl commands. It also includes a cookie vault that automatically matches imported browser cookies to their corresponding domains, and pre-built artifacts are included in the repository so you don’t need to compile from source after cloning.
The plugin adds a dedicated one-click entry to the bottom of the DSH sidebar, so you can open the full-screen sitemap directly within the DSH app without switching windows. On your first use, you need to click the “Regenerate” button to trigger the plugin to scan for common reconnaissance file formats in your workspace, then generate a full sitemap from the found data. This tool is designed for security testers who need to organize target assets and test interfaces, turning scattered unorganized request logs into a clear, easily navigable structure. Each host gets a unique assigned color from a 14-color palette to make it easier to distinguish different targets at a glance.
The plugin supports both Chinese and English interfaces, and exposes four tools that can be called directly within DSH SRC workflows, including regenerating the sitemap, querying interfaces, fetching matching cookies, and importing cookies directly from workflows. It is released under the permissive BSD-3-Clause open source license, and users are only permitted to use it for authorized security testing per the project’s disclaimer. If you need to modify the plugin or rebuild from source, you can run npm install followed by npm run build to generate new working artifacts.
这是一个专为DeepSeek Harness(DSH)开发的原生插件,将Yakit风格的站点地图交互体验引入DSH。它可以把工作区中侦察到的接口按主机树形整理,支持搜索接口、查看接口详情(方法、参数、出现次数、来源)、一键复制curl请求,还自带Cookie保险库功能,能自动匹配导入的浏览器Cookie对应站点。安装方式为克隆仓库到DSH插件目录后重启DSH即可激活。
插件在DSH侧边栏底部添加了专属一键入口,点击即可在应用内打开全屏站点地图。首次使用需要点击「重新生成」按钮,插件会自动扫描工作区中的多种常见格式侦察文件,全量合成生成站点地图数据。这个工具非常适合需要整理资产和测试接口的安全测试人员使用,能帮你把零散杂乱的请求记录整理得清晰直观。
插件支持中英双语界面,每个主机会自动从14色盘中分配一种配色方便区分,还提供四个可在SRC工作流中直接调用的工具,支持自动刷新地图、查询接口、获取Cookie等操作。本插件采用BSD-3-Clause开源许可证,构建产物已预先提交到仓库,无需自行编译即可使用,仅允许用于已获授权的安全测试。
请帮我安装这个 DSH 插件。安装前先完成【兼容性检查 + 安全性检查】,检查通过再动手。

插件:dsh-sitemap(deCOLE118/dsh-sitemap)
仓库:https://github.com/deCOLE118/dsh-sitemap
本站详情页:https://www.yhbd.top/plugins/decole118-dsh-sitemap/
本站登记:类型 plugin · 归类 原生 DSH 插件 · 许可证 BSD-3-Clause · ⭐ 3 · 最近提交 2026-08-21 · 主语言 TypeScript

按下面顺序执行,每步先把结论告诉我,再进入下一步:

【1 兼容性检查】
① 我这边:DSH 版本、Node 版本、操作系统、当前 profile(web / desktop)。
② 读它的 README、package.json、插件 manifest,列出它要求的 DSH 版本 / Node 版本 / 操作系统 / 外部依赖 / 需要另外先装的运行时。
③ 逐条比对,结论只写「满足 / 不满足 / 未知」三种;不满足的给出可行替代方案。
④ 检查是否和我已装的插件冲突:命令名重复、skill / tool 重名、端口占用、重复注册的 MCP server。

【2 安全性检查】
① 仓库可信度:和上面「本站登记」是否一致;star / fork 数、创建时间、最近提交,是否归档或长期停更。
② 安装脚本:逐行看 package.json 的 preinstall / install / postinstall,以及 install.sh、setup.ps1 之类脚本。出现 curl|bash、下载后直接执行、混淆代码、访问与插件功能无关的域名,立刻停下来告诉我,不要继续装。
③ 依赖:列出新增依赖,标出无人维护、或与知名包拼写近似的可疑包(typosquatting)。
④ 权限与副作用:它会读写哪些目录、访问哪些域名、需要哪些 DSH 权限(filesystem / network / shell / clipboard 等),以及怎么卸载和回滚。
⑤ 如果它要求 sudo / 管理员权限,或权限明显超出功能所需,先停下来问我。

【3 安装】
上面两步没有「不满足」和「高危项」时才执行;用官方推荐方式安装,不要自行提权。

【4 汇报】
用表格输出:检查项 / 结论 / 依据 / 是否需要我决策。拿不准的一律写「未知」并说明要我怎么确认——不要猜,也不要替我决定。
Send this message to DSH in your current session: it verifies compatibility and security first (answering met / not met / unknown item by item) and only installs once everything checks out — it will stop and ask you if it finds a high-risk item. The box scrolls; the copy is the full prompt. CLI install commands may not be accurate across systems, so DSH is the safer route.把上面这条消息直接发给当前会话里的 DSH:它会先核对兼容性与安全性(逐条给「满足 / 不满足 / 未知」),确认没问题再安装,有高危项会停下来问你。框内可滚动,复制到的是完整提示词;安装命令不一定准确,发给 DSH 更稳。
- Only 3 stars - very few users, little community feedback星标只有 3,几乎没人在用,遇到问题缺少社区反馈
DSH walks through these 9 checksDSH 会逐条核对这 9 项
Compatibility兼容性
- DSH, Node, OS and profile requirementsDSH 版本 / Node 版本 / 操作系统 / profile 是否满足要求
- External dependencies and runtimes (Electron / Python / Docker, ...)外部依赖与运行时(Electron / Python / Docker 等)是否齐备
- Conflicts with installed plugins: command names, skill / tool names, ports, duplicate MCP registration与已装插件是否冲突:命令名、skill / tool 重名、端口占用、重复 MCP 注册
Security安全性
- Repo matches the facts registered here; archived or abandoned?仓库是否与页面登记一致,是否归档或长期停更
- Safety of preinstall / install / postinstall and install.sh / setup.ps1preinstall / install / postinstall 与 install.sh、setup.ps1 是否安全
- curl|bash, download-then-execute, obfuscation, unrelated domains → stop immediatelycurl|bash、下载即执行、混淆代码、无关域名 → 立刻停止
- Typosquatting or unmaintained packages among the new dependencies新增依赖里有没有 typosquatting 或无人维护的包
- Requested permissions vs. what the feature actually needs申请了哪些权限、是否超出功能所需(filesystem / network / shell / clipboard)
- Any sudo / admin requirement, plus uninstall and rollback是否要求 sudo / 管理员权限,以及卸载与回滚方式
Anything uncertain must be marked unknown with a note on how to confirm it. This site's signal screen is a static snapshot, not a security audit.拿不准的必须标「未知」并说明要我怎么确认。本站的信号筛查是静态快照,不能替代安全审计。
Or use CLI install (for developers)或使用命令行安装(适合开发者)
CLI Install命令行安装
dsh plugin --profile web add github:deCOLE118/dsh-sitemap把 deCOLE118/dsh-sitemap 加入你的 DSH 配置(web profile)即可启用。
READMEREADME
dsh-sitemap
DeepSeek Harness(DSH)站点地图插件 · 把 Yakit 的站点地图交互搬进 DSH
在 DSH 侧边栏一键打开「站点地图」:按主机树形组织工作区侦察到的接口,每个站点有专属配色,支持搜索、接口详情(方法 / 参数 / 出现次数 / 来源)、一键复制 curl;还带一个 Cookie 保险库——导入浏览器导出的 cookie 后自动标注哪些站点能带着身份访问,src 工作流可以直接自取 cookie 注入浏览器测试。
设计来源
Yakit 里的「站点地图」我觉得做得很好,就借鉴了它的交互:把发现的所有接口按主机自动归类,形成一棵可展开、可搜索的树:
hosts
└── account.example.com
    └── /user/webrest/v1/login.do
做资产梳理和接口测试时,这棵树比零散的请求记录直观得多。本插件把同样的体验带到 DSH,并且补了两个 Yakit 没有的东西:每个站点一种颜色(一眼分清目标),和cookie 覆盖标注(哪些站点能直接以已登录身份访问,不用再猜)。
特性
- 🗺 侧边栏入口:点击「站点地图」打开应用内全屏地图(中 / 英双语)
- 🎨 站点配色:每个主机名哈希到 14 色盘里的一种,主机圆点、接口选中色统一
- 🌲 主机树:主机 → 接口路径两级树,可折叠、显示统计
- 🔍 实时搜索:按主机名 / 接口路径过滤
- 📋 接口详情:方法、参数、出现次数、来源文件;一键复制 curl、新窗口打开
- ♻️ 重新生成:从工作区侦察文件全量覆盖合成
sitemap_data.json——历史残留站点一次清空 - 🗑 清除:站点树上每个主机可单独删除;顶部「清空」一键删掉整张地图
- 🍪 Cookie 保险库:导入 Cookie-Editor 的 JSON / Header String / Netscape 三种格式,按域名自动匹配并给站点打「🍪 n」标注,详情页可一键复制该站点的 Cookie header
- 🛠 src 工作流工具:
sitemap_query/sitemap_cookie/sitemap_regen/sitemap_import_cookie四个 agent 工具,工作流自己取数、取 cookie,不用用户复制粘贴
使用方法
站点地图
- 侧边栏底部点击「🗺 站点地图」打开地图
- 第一次打开时点「重新生成」:插件扫描工作区侦察文件,全量合成
sitemap_data.json - 右侧「刷新」随时重新读取;「清空」删除整张地图;悬停主机点 🗑 删除单个站点
数据从哪来? 点「重新生成」时插件扫描工作区根目录下这些侦察文件(没找到的自动跳过):
| 文件 | 投进去什么 |
|---|---|
all_host_apis.json |
主机 → 接口路径列表 |
urls_by_host.json / cvp_urls_by_host.json |
主机 → 完整 URL(自动取 host + path) |
hll_apis.json |
纯路径数组(挂到名为 hll 的虚拟主机下) |
sdp_apis.json |
{path, method, count} 对象数组(挂到 sdp 下) |
什么时候触发? 「重新生成」和「刷新」都是点一下拉一次,无缓存;生成器会覆盖写输出文件,所以老站点会随之消失。文件不存在时弹窗显示空状态。生成 / 删除后无需重启 DSH。
Cookie 保险库
- 在真实浏览器用 Cookie-Editor 扩展导出目标站点的 cookie(JSON 或 Header String,Netscape 也行)
- 站点地图弹窗右上角「🍪 保险库」→ 粘贴 → 导入(Header 形式记得填「适用域名」)
- 导入后插件按域名匹配:地图上覆盖到的站点会挂
🍪 n角标,接口详情页列出匹配的 cookie,点一下复制 Cookie header - cookie 存在工作区
dsh-sitemap-cookies.json(跟sitemap_data.json同目录),不进插件仓库、不上传 GitHub
src 工作流怎么用
插件加载后,SRC 会话的 agent 自动获得四个工具,典型开场:
sitemap_regen— 用工作区侦察文件刷新资产底图sitemap_query— 查主机 / 接口,挑测试目标sitemap_cookie host=目标域名— 取该站点的 Cookie header 与明细browser_add_cookies(dsh-tool-playwright 提供的工具)写入共享浏览器 →browser_navigate访问目标,即带着身份测试
Showing the opening section of the README — the full document lives in the repository以上为 README 开头摘要,完整文档在仓库内 · View the full README on GitHub →在 GitHub 查看完整 README →
Related相关推荐
-
 Jesseovo/last30days-skill-cn
last30days-cn 是一个 AI Agent 技能(Skill),能够自动搜索中国互联网 8 大主流平台最近 30 天的内容,综合分析后生成有据可查的研究报告。
-
 omdsh-dev/dsh-genui
GenUI for DeepSeek Harness: interactive UI components rendered inline in assistant replies via the dsh-ui fence — layout…
-
 evoelsewhere/evoflux
Evoflux is an open-source, local-first workspace where AI agents build software, conduct deep research, automate browser…
-
 jiaererw/dsh-plugin-chrome
DeepSeek Harness browser visualization plugin: a visible Chrome window per session, 16 chrome_* agent tools, live view i…
-
 tiantianlaolao/dsh-astock-research
A股个股研究助手 - DeepSeek Harness (dsh) 插件:股票搜索/历史公告/财报/画像/信号科普,附合规 skill
- fufengyuan/dsh-stool-plugin DSH 运维工具箱插件。将 stool 运维 CLI 的全部能力注册为 DSH 模型可调用的工具,无需手动操作即可让 Agent 自动执行服务器管理、日志搜索、数据库查询、CI/CD 部署等操作。
-
 Tencent/BrowserSkill
Let AI agents use your real, logged-in browser without interrupting your work. CLI + extension for browser automation ac…
-
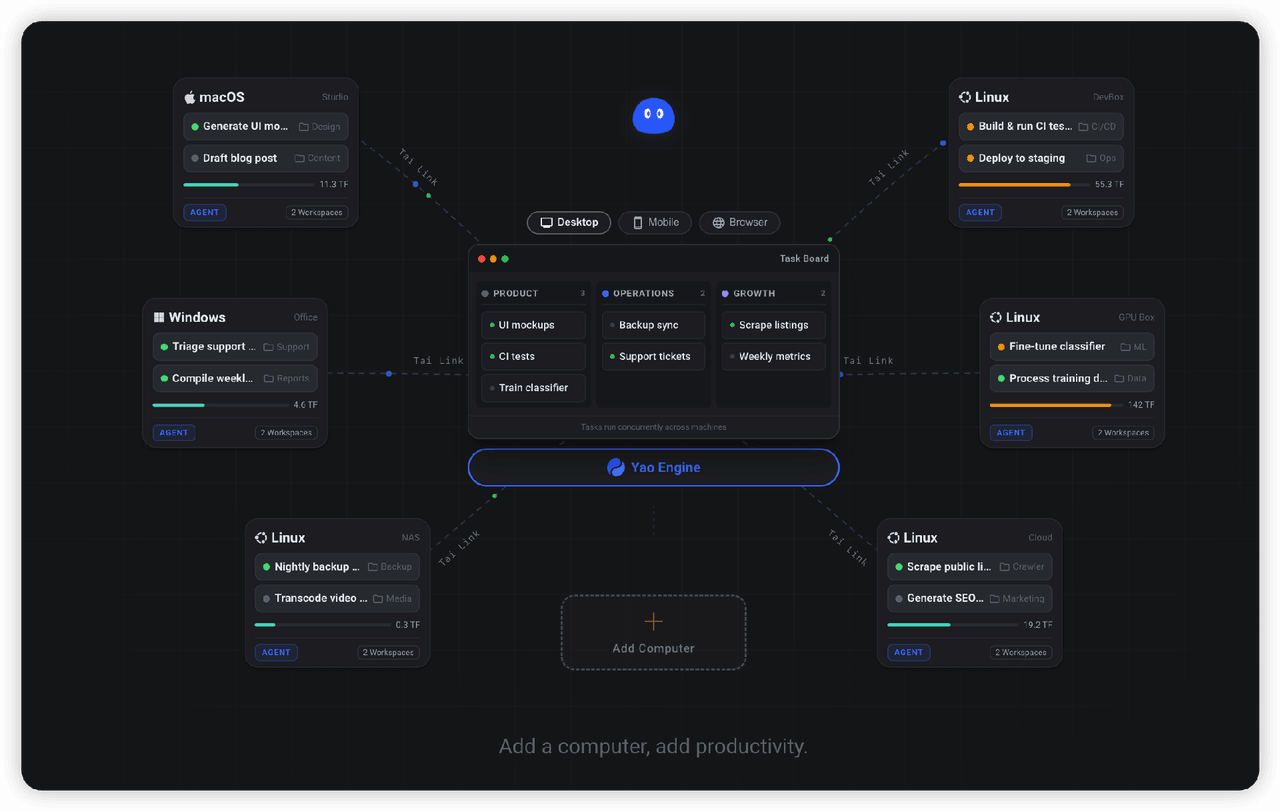 YaoApp/yao
✨ All your agents and workspaces in one place, on every device you own. Track tasks on a board, accessible from desktop,…