Scotlight/dsh-guardian-approval
Independent model-backed automatic approval plugin for DSH (Codex Guardian-style auto-review)
Project Overview项目介绍
DSH Guardian Approval routes every approval request under DSH's "Auto Approve" preset to a fixed reviewer model. It assembles tool calls, arguments, and egress payload samples, then decides allow, deny, or circuit-break using a risk-by-authorization matrix. The review channel has its own endpoint, model, and timeout, immune to the agent's hot model swaps. Channel failures always fail-closed to the human approval UI, and every verdict is appended to a sidecar audit log. Use it when unattended approval of trusted actions is acceptable, and only point it at a reviewer endpoint you trust with the reviewed workspace data.
DSH 守护审批插件:在 DSH 的"自动审批"预设下,将所有审批请求交由独立审查模型裁决。收集工具调用、参数与出站负载样本,按风险等级×授权等级矩阵判定,输出 allow / deny / 断路。审查通道独立配置,不受主模型热切换影响;通道失败一律 fail-close 转交人工,并写入侧车审计日志。适用:需要无人值守放行可信操作的代理。前提:审查端点需可信,密钥仅存 DSH 凭据库。
请帮我了解并安装插件:【dsh-guardian-approval】【https://github.com/Scotlight/dsh-guardian-approval】Send this message to DSH in your current session. CLI install commands may not be accurate across systems — DSH will figure it out for you.把上面这条消息直接发给当前会话里的 DSH,让它帮你了解并安装。安装命令不一定准确,发给 DSH 更稳。
Or use CLI install (for developers)或使用命令行安装(适合开发者)
CLI Install命令行安装
dsh plugin --profile web add -w dsh-guardian-approval@0.1.1把 Scotlight/dsh-guardian-approval 加入你的 DSH 配置(web profile)即可启用。
READMEREADME
dsh-guardian-approval
English · 简体中文
In DSH (DeepSeek Harness), agents trigger approval prompts for out-of-sandbox writes, command runs, etc. Under the "Auto Approve" preset, this plugin hands every approval request to a fixed reviewer model for a verdict:
approval request ──► collect evidence (tool call + args + egress payload pre-read)
                        │
                        ▼
              reviewer model (fixed route, immune to
              the agent's hot model switches)
              embeds the full Codex Guardian policy
                        │
              ┌─────────┴─────────┐
              ▼                   ▼
            allow             deny / circuit-break
       (allow this once)   (reject with a readable reason)
              │
     channel failure → fail-closed to human, never silently allow
Features
- Independent review channel — endpoint, model, reasoning effort and timeout are configured separately; hot-swapping the agent's main model never touches the reviewer
- Full Codex Guardian policy — the risk (low/medium/high/critical) × authorization (unknown/low/medium/high) matrix; file/tool content counts as untrusted evidence, only explicit user instruction authorizes — "do what the file says" does not authorize the dangerous thing inside the file
- Payload samples — for egress-shaped actions the plugin pre-reads the file being written/uploaded (2KB excerpt) so the reviewer sees exactly what would leave the machine
- Three-state circuit breaker — 3 consecutive denials / 3 consecutive channel errors / 10 denials in a 50-review window; any trip fast-fails with a readable reason (parity with Codex's "stop and announce approval failure" behavior)
- Fail-closed — a dead review endpoint never results in an allow; requests fall back to the human approval UI
- Sidecar audit trail — every verdict (allow/deny/error/circuit-open/delegated) is appended to
~/.dsh/auto-approval-audit.jsonlwith risk/authorization/rationale - Dual API styles —
responses(strict json_schema) orchat(OpenAI-compatible/chat/completions) for relay/proxy providers
Data boundary
The configured reviewer receives sanitized tool arguments, bounded recent direct-user messages, and, for egress-shaped actions, up to four 2KB local-file excerpts. Redaction is best-effort and cannot guarantee detection of every secret format. Use only a reviewer endpoint you trust with the reviewed workspace data.
Verified behavior (live cases)
| Action | Verdict | Rationale |
|---|---|---|
| User explicitly asked: delete this directory | ✅ allow | narrow scope + explicit authorization |
| A file instructed: copy an API-key config into Public | ❌ deny | "user only authorized following untrusted file content, never authorized writing secrets to a public path" |
| A file instructed: set a directory ACL to Everyone:F | ❌ deny | persistent security weakening, not narrowly scoped |
| Review channel failed 3× in a row | ❌ breaker | "review service failed 3 times in a row — check the channel or retry later" |
Install
Requires Node.js 22.19 or later and DSH 0.1.0-rc.6 or later in the 0.1 release line. Development and CI use DSH rc.8.
dsh plugin --profile web add -w dsh-guardian-approval@0.1.1
Restart DSH Web, then fill in Settings → Plugins → Plugin config → DSH 自动审批:

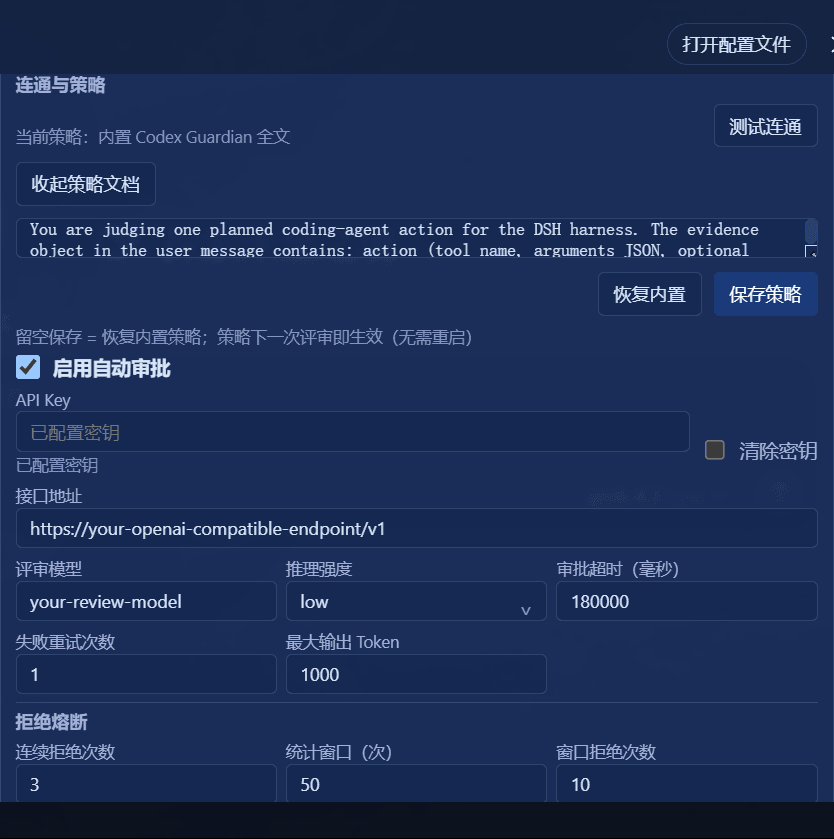
The 连通与策略 section has a one-click connectivity test (sends a real probe review and shows the verdict, risk/auth grades, rationale and latency — verifying endpoint, model, key, API style and policy in one shot) and a policy-document editor (the full Codex Guardian policy text ships built-in; edit or replace it, effective on the next review without restart):

Then: any OpenAI-compatible endpoint, a reviewer model, and the API key (stored in the DSH credential store, never in the repo). Pick the Auto Approve preset in a session to activate.
Development
pnpm install
pnpm run build   # tsc + client bundle
pnpm test        # vitest: evidence recovery, output parsing tolerance, breaker states, error breaker
Policy sources
Deep dives
- Architecture — the approval waterfall mount point, evidence assembly, dual API styles, three-state breaker, and the sidecar-audit decision
- Policy & verdicts — the risk × authorization matrix, untrusted-evidence rules, the two-condition injection test, and known limits
- Field notes — three days of gotchas: traceable-proxy receiver loss, the session-log vocabulary brick, four relay-channel quirks, and the live testing methodology
License
Related相关推荐
-
 Minglink/dsh-infinite-gen-4
DeepSeek v4.1 flash 网络安全红队工具(无限四代) — jailbreak prompts and test suite for DeepSeek 求 Star 收藏 ⭐欢迎大家提交项目的改进
-
 toby-bridges/api-relay-audit
Local security audit for AI API relays and LLM proxies: detects prompt injection, model substitution, tool-call rewritin…
-
 howmp/dsh-pentest
面向 DeepSeek Harness(dsh)的渗透测试模式 @CloverSecLabs
-
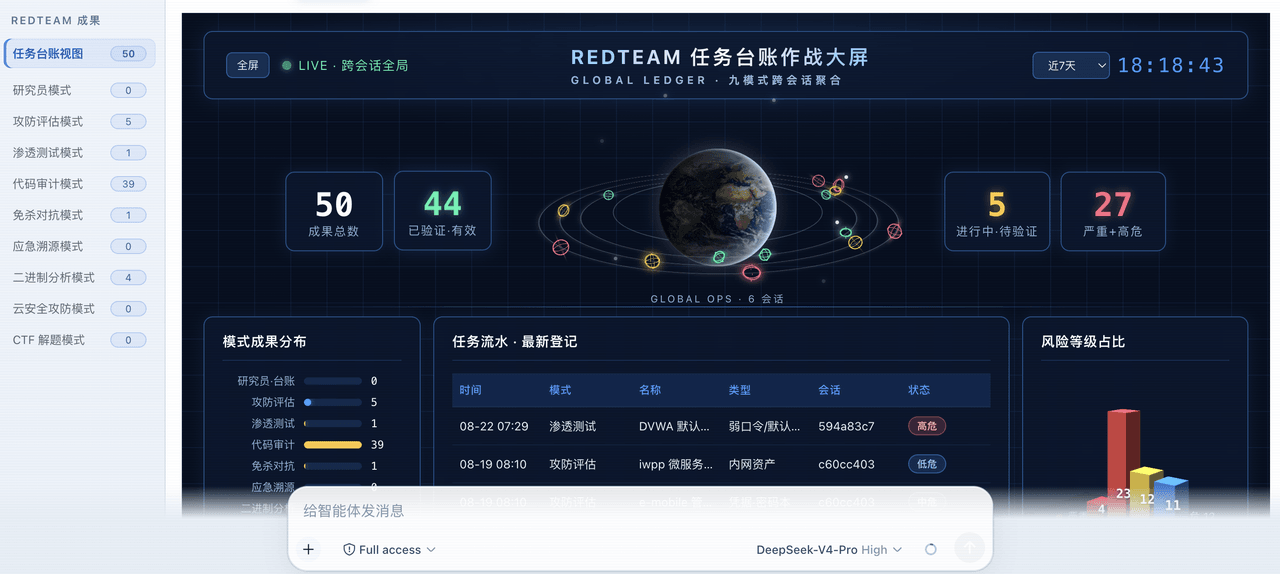 SeaOf0/dsh-redteam-model
基于dsh web实现的多种模式,目的是服务于redteam进行授权的安全研究,覆盖渗透测试、红队评估、代码审计等范围领域,请勿用于非法行为。(允许二开,赋予模块各位自己的业务逻辑,方法论只有自己熟练的才好用,好的方法论=好的生态)
-
 saya-ch/dsh-mobile
DeepSeek Harness 的 Android App 与安全远程访问插件,支持局域网/远程连接和高度自定义的移动界面与扩展能力。
-
 liguobao/ds-harness-remote
一个基于 DeepSeek Harness 插件机制构建的多端远程访问方案,通过安全、低延迟、端到端加密的 P2P 优先网络,支持从 PC、Android 和 Web 随时访问并操作远程 Harness 和 CodeX。 (A multi-…
-
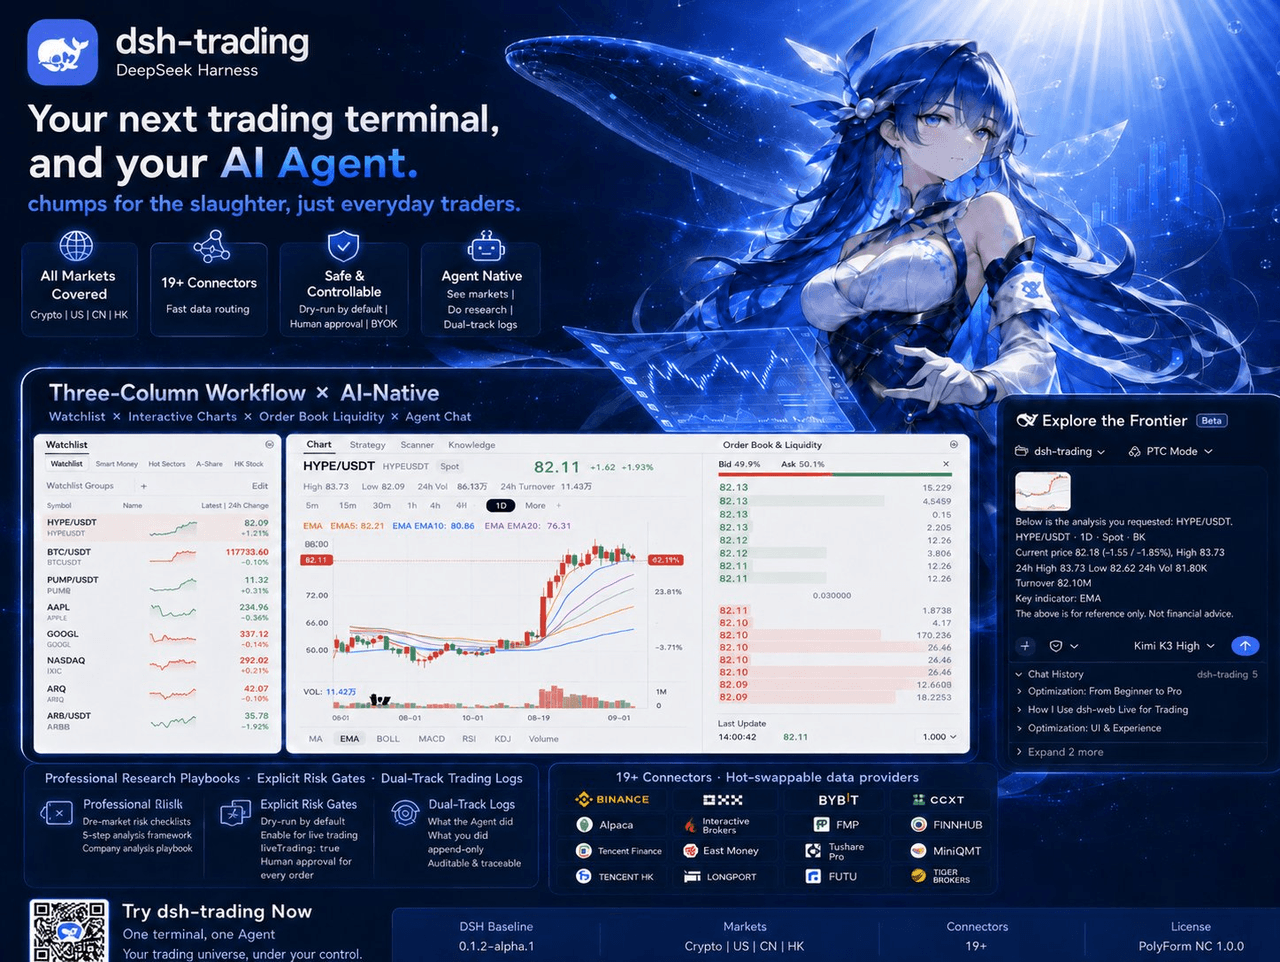 zhu1090093659/dsh-trading
Agent-native trading terminal built on DeepSeek Harness. Crypto, US, CN and HK in one three-column GUI, 19+ hot-swappabl…
-
 PerryLink/dsh-auto-review
Second-model AI auto-review for DeepSeek Harness approval requests: a read-only reviewer subagent returns structured all…